




Table of contents
- Q1: What Is Managed SIEM, and Why Are Security Teams Shifting to It?
- Q2: How Does Managed SIEM Actually Work Behind the Scenes? (Log Collection to Threat Response)
- Q3: What Services Are Typically Included in a Managed SIEM Engagement?
- Q4: Self-Managed vs. Co-Managed vs. Fully Managed SIEM: Which Model Fits Your Organization?
- Q5: What Are the Real Benefits and Limitations of Managed SIEM?
- Q6: Managed SIEM vs. MDR vs. XDR vs. SOC vs. MSSP: How Do These Models Differ?
- Q7: How Does Managed SIEM Support Compliance Frameworks Like SOC 2, HIPAA, and ISO 27001?
- Q8: What Should Security Leaders Evaluate Before Choosing a Managed SIEM Provider?
- Q9: What Does Day 1 to Day 90 With a Managed SIEM Provider Actually Look Like?
- Q10: How Do the Leading Managed SIEM and SOC Providers Compare?
- Frequently Asked Questions
Q1: What Is Managed SIEM, and Why Are Security Teams Shifting to It?
Managed SIEM is a security operations model where a third-party provider handles the deployment, tuning, monitoring, and management of your Security Information and Event Management platform, including log collection, event correlation, threat detection, and incident escalation, so your internal team doesn’t have to build or staff a 24/7 SOC from scratch.
SIEM vs Managed SIEM: What Changes for Your Team
SIEM is the technology. It collects, analyzes, and correlates log and event data from across your infrastructure to detect and respond to threats. Managed SIEM is the operating model: a provider sets up, maintains, and fine-tunes that SIEM, and watches what it finds.
The difference is who does the work. A SIEM platform takes deep knowledge and continuous training to run well, and with a traditional SIEM your own team carries all of it. With managed SIEM, the provider takes on the daily operation, and you can still own the platform and the data.
| What differs | Traditional SIEM | Managed SIEM |
|---|---|---|
| Who runs it | Your in-house team | An outsourced provider |
| Cost | Higher upfront costs, plus ongoing maintenance | Lower initial costs, predictable monthly fees |
| Expertise | Requires in-house security expertise | Specialized security professionals from the provider |
| Deployment | Slower, with extensive setup | Faster deployment and configuration |
| Maintenance and updates | Your team handles them | The provider handles them |
| Scalability | May require major infrastructure upgrades | Scales with your organization’s needs |
| Monitoring hours | Set by your own staffing | 24/7 from the provider’s analysts |
| Detection tuning | Your team, between other work | The provider’s detection engineers |
The SIEM itself can be the same in both columns: Splunk, Microsoft Sentinel, Elastic, or QRadar. What changes is who tunes the rules, who keeps the platform healthy, and who answers the alert at 3 AM.
Why the Shift Is Accelerating
The math stopped working for most organizations. In the 2025 ISC2 Cybersecurity Workforce Study, 33% of organizations said they lack the budget to staff their security teams adequately, and 29% said they cannot afford to hire staff with the skills they need. The gap is now about skills as much as headcount, and budget cuts make both harder to close.
Meanwhile, log volumes are exploding. Cloud workloads, SaaS sprawl, hybrid environments: every tool you add generates telemetry that your SIEM needs to ingest, normalize, and correlate. Running a SIEM 24/7 requires multiple shifts of analysts, incident responders, and management staff, and the U.S. Bureau of Labor Statistics puts the 2025 median pay for an information security analyst at $129,180 a year. That bill grows again as your datasets and complexity grow.
Compliance adds its own pressure. SOC 2, HIPAA, ISO 27001, and PCI DSS each require continuous monitoring evidence that auditors verify. GDPR requires breach notification to the supervisory authority within 72 hours, and SOX audits test the IT controls behind financial reporting. Your SIEM is the audit trail, and if nobody’s tuning the rules or watching the alerts at 3 AM, that audit trail becomes a liability.
The Problem With Legacy Approaches
Here’s what I’ve seen across hundreds of engagements: organizations typically land in one of two broken states.
Legacy MSSP monitoring gives you “alerts without context,” meaning checkbox coverage built on rigid playbooks, with little real-time understanding of the threat. You get a dashboard and no answers.
Pure-play SIEM tools give you “technology without operational expertise.” You buy Splunk or Elastic, configure it once, and watch detection quality decay within months because nobody’s tuning the correlation rules to match your evolving environment.
Managed SIEM is the convergence: technology, expertise, and 24/7 operational coverage. It’s the acknowledgment that tools alone don’t save the day: people, process, and tools working together do.
How UnderDefense Approaches Managed SIEM
If your team has spent years tuning detections, the worst outcome of a provider switch is losing them. The UnderDefense Agentic AI SOC works on top of your existing SIEM, whether that’s Elastic, Splunk, or another platform, so you retain full ownership of your data, correlation rules, and business logic. That design is a lesson learned from watching organizations lose years of custom detection tuning when they switch providers.
As one CISO who works with UnderDefense put it during a recent session, if your MDR provider owns your SIEM, you start over on detection engineering every time you renegotiate a contract. UnderDefense handles everything from detection engineering to 3 AM escalations, with a 20-minute SLA response time for critical alerts, and you keep control.
Q2: How Does Managed SIEM Actually Work Behind the Scenes? (Log Collection to Threat Response)
Most articles on managed SIEM say “it collects logs and detects threats” but never explain what actually happens between raw log ingestion and a confirmed incident landing on your desk. If you’re trusting a provider with your security telemetry, you deserve operational transparency, stage by stage.
The Six-Stage Pipeline
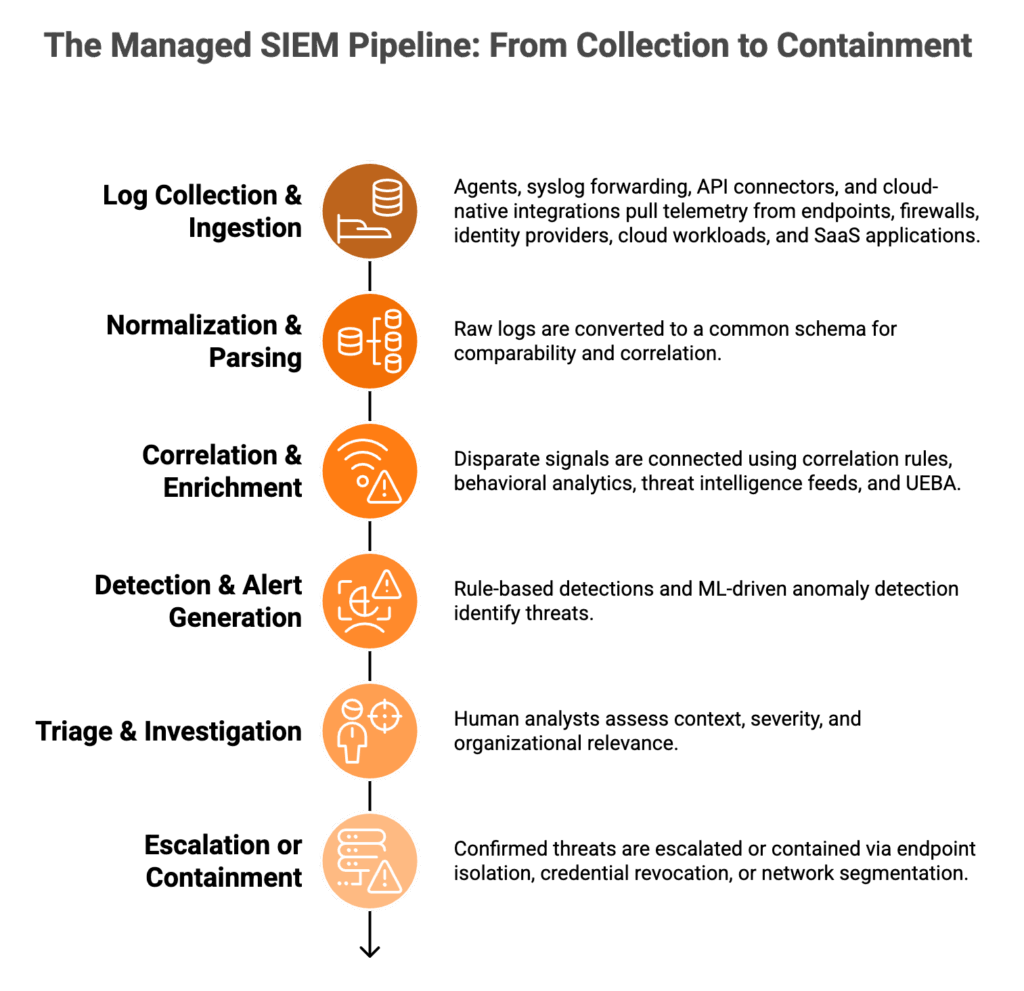
Here’s the full managed SIEM pipeline, step by step:
- Log collection and ingestion pulls telemetry through agents, syslog forwarding, API connectors, and cloud-native integrations from endpoints, firewalls, identity providers (Okta, Microsoft Entra ID), cloud workloads (AWS CloudTrail, GCP), and SaaS applications. Every relevant data source gets onboarded.
- Normalization and parsing converts raw logs from dozens of formats, such as CrowdStrike events, Okta authentication logs, AWS CloudTrail entries, and Palo Alto firewall alerts, to a common schema so they’re comparable and correlatable. Without this step, your SIEM is just a log warehouse.
- Correlation and enrichment is where signal emerges from noise. Correlation rules, behavioral analytics, threat intelligence feeds, and UEBA (User and Entity Behavior Analytics) connect disparate signals, tying a failed VPN login to a credential dump on the dark web to an unusual file download on an endpoint.
- Detection and alert generation combines rule-based detections that catch known patterns with ML-driven anomaly detection that catches deviations from baseline behavior. Both should map to the MITRE ATT&CK framework so you can see exactly which tactics and techniques are being flagged.
- Triage and investigation puts human analysts on context, severity, and organizational relevance. This is the step that separates real threats from noise, and it’s the step most providers shortcut.
- Escalation or containment hands confirmed threats to your team with full context, or contains them directly through endpoint isolation, credential revocation, or network segmentation.
The Gap Most Buyers Miss
The critical differentiator lives between Step 4 (detection) and Step 6 (response). Most managed SIEM providers stop at detection. They generate the alert and throw it over the wall to your team with a “please investigate” ticket.
Here’s the operational reality: many behavioral alerts require context that technology alone can’t provide. Did Jane log in from a new location, or was her account compromised? Did your IT admin run that PowerShell script, or was it an attacker? If you had time, you’d ask, but at 2 AM your analyst is triaging 47 other alerts.
How UnderDefense Closes the Loop
When a detection fires at 2 AM, you need someone who can tell a legitimate user from a compromised account before your team wakes up. The Agentic AI SOC runs this entire pipeline, ingesting from 250+ tools, with about 2 minutes from alert to triage, and concierge analysts verify suspicious activity directly with affected users via Slack, Teams, or email.
When the detection says “unusual OAuth grant at 2:41 AM,” the analyst messages the user to confirm, and if they didn’t authorize it, UnderDefense revokes the token and contains the session.
That’s 96% MITRE ATT&CK coverage backed by the one thing pure automation can’t deliver: human judgment applied at speed. The Agentic AI SOC runs this entire workflow in a single, auditable view.
Q3: What Services Are Typically Included in a Managed SIEM Engagement?
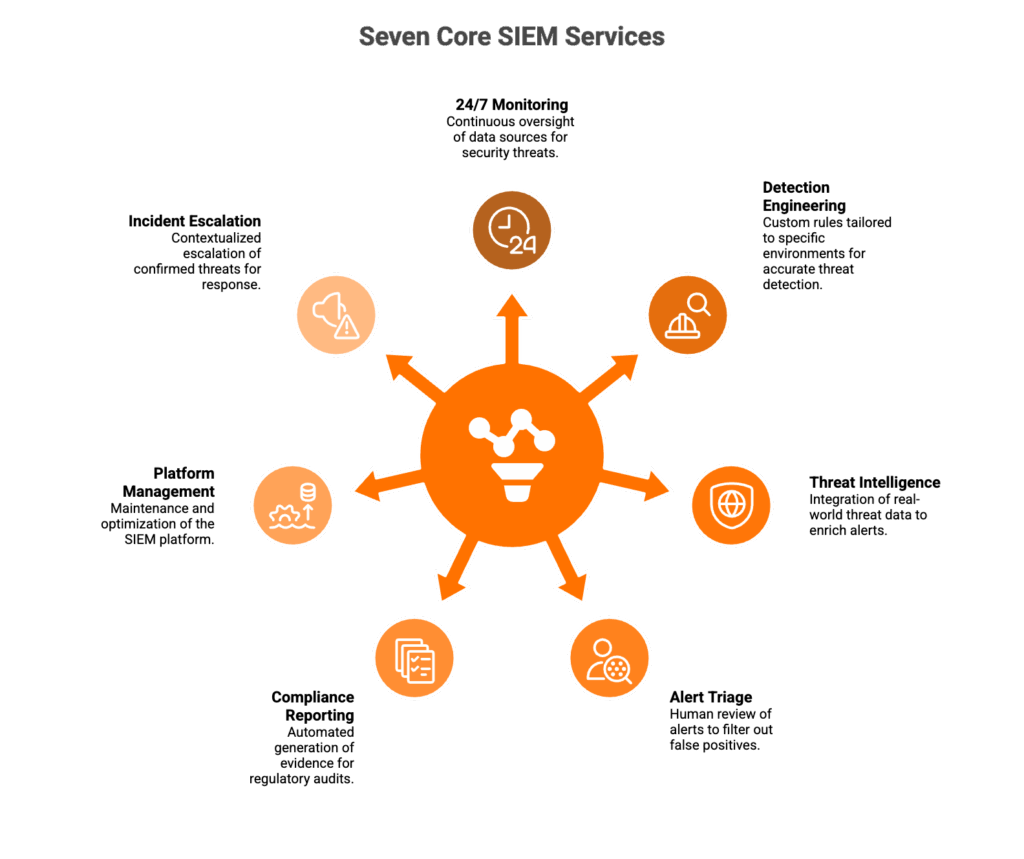
A fully managed SIEM engagement should cover seven core service areas. Anything less means you’re buying partial coverage and staffing the gaps internally, often without realizing it until an incident exposes the holes. Here’s what to expect and what to verify before signing.
The Seven Core Services
Check each of these against the provider’s contract:
- 24/7 log monitoring and event correlation gives continuous oversight across all ingested data sources, nights and weekends included.
- Detection engineering and custom rule tuning maps rules to your specific environment, where generic out-of-the-box signatures decay within weeks.
- Threat intelligence integration enriches alerts with commercial and open-source feeds on active threat campaigns.
- Human-led alert triage and investigation means analysts review alerts for organizational relevance before anything reaches your inbox.
- Compliance reporting and audit evidence generation produces the artifacts auditors actually request for SOC 2, HIPAA, ISO 27001, and PCI DSS.
- SIEM platform management covers health monitoring, performance tuning, storage optimization, and index management, so your platform doesn’t degrade over time.
- Incident escalation with context and response guidance hands confirmed threats over with the full investigation, or contains them directly in advanced tiers through endpoint isolation, credential revocation, or network segmentation.
What’s Often Missing (And Shouldn’t Be)
Many providers bundle items 1 and 6, then charge separately for detection engineering, threat hunting, and compliance reporting. That’s the equivalent of buying a car without an engine and paying extra for it later. If your provider’s “managed SIEM” stops at log storage and basic alerting, you’re paying for a monitoring dashboard and going without the managed security operations you budgeted for.
How UnderDefense Delivers All Seven, Plus More
If your provider stops at alerting, your team still does the investigation. UnderDefense covers all seven areas, plus threat hunting and ChatOps user verification. You keep full ownership of your Elastic or Splunk instance while UnderDefense runs it day to day: detection engineering, rule tuning, compliance automation, and 24/7 analyst response.
The result is about 99% noise reduction, which UnderDefense reports from custom detection tuning on each customer’s own data, so your team reviews confirmed incidents and stops triaging thousands of maybes. Reviewers report that this tuning takes from a few weeks to a few months.
“Their team cleaned up our configurations and got the noise under control within the first week. Now when we get an alert, we know it’s something worth looking into.”
Verified User, Marketing and Advertising, UnderDefense G2 Verified Review
“At first, we hired them for managed SIEM service, but after they demonstrated the value of MDR, our management was motivated to act on it. Now, with their security monitoring and incident response we know our endpoints are well-protected.”
Yaroslava K., IT Project Manager, UnderDefense G2 Verified Review
“UnderDefense MAXI integrates well with our systems, specifically with our SIEM, Splunk. Their team is proactive in identifying and addressing threats, providing 24/7 oversight.”
Oleg K., Director Information Security, UnderDefense G2 Verified Review
All three reviewers describe the same shift: the SIEM they already owned started producing alerts worth an analyst’s time.
Q4: Self-Managed vs. Co-Managed vs. Fully Managed SIEM: Which Model Fits Your Organization?
Most articles frame managed SIEM as a binary: build it yourself or outsource everything. Reality is a spectrum with three distinct models, and the right choice depends on your team size, budget, compliance timeline, and whether you have the 24/7 coverage to monitor and tune a SIEM continuously.
Self-Managed SIEM
Full internal ownership. You deploy, configure, tune, and monitor the SIEM with your own staff.
Strengths: Maximum control, data sovereignty, and deep customization for unique business logic.
Limitations: Requires 3 to 5 dedicated FTEs at SOC analyst salaries, a 6 to 12 month deployment, and an annual budget that covers platform licensing, staffing, training, and continuous rule tuning. Detection quality decays fast if nobody’s maintaining correlation rules, and turnover at Tier 1 is constant.
Co-Managed SIEM
You own the SIEM; the provider supplements with detection engineering, tuning, and overflow monitoring.
Strengths: Retains tool ownership, augments gaps in expertise, and keeps business logic in-house.
Limitations: Shared responsibility creates accountability gray zones during incidents. Who responds at 3 AM? Unclear SLAs on triage ownership mean your team still carries the on-call burden. As one CISO described it, a level two or level three team stays in-house for business context, and the handoff points are where things break.
Fully Managed SIEM
The provider owns the entire operational lifecycle: deployment, tuning, detection engineering, 24/7 monitoring, triage, and response, while the customer retains platform and data ownership.
Strengths: Fastest time to value (30 days vs. 6 to 12 months), predictable costs, 24/7 coverage included, and no hiring or training overhead.
Limitations: Requires trust in the provider’s detection quality and response capability, which is why you should demand observable workflows and refuse black-box dashboards.
Side-by-Side Comparison
The table puts the three models next to each other on the dimensions that decide most buying conversations.
| Dimension | Self-Managed | Co-Managed | Fully Managed |
|---|---|---|---|
| Staffing Requirement | 3 to 5 dedicated FTEs | 1 to 2 internal plus provider | None required |
| Annual Cost Drivers | Licenses, infrastructure, 3 to 5 salaries | Licenses, 1 to 2 salaries, provider fee | Provider fee, often per device |
| Time to Value | 6 to 12 months | 2 to 4 months | 30 days |
| Detection Rule Ownership | Fully internal | Shared | Provider-managed, customer-owned |
| 24/7 Coverage | Must staff 3 shifts | Partial or overflow only | Included |
| Compliance Reporting | Manual or internal | Partial automation | Automated |
| Customization Level | Unlimited | Moderate | High (vendor-agnostic) |
| Best For | Mature SOC with 5+ analysts | Partial internal capability | Teams under 5 security FTEs |
Prescriptive Guidance
Choose self-managed if you have a mature SOC with 5+ analysts, strict data sovereignty requirements, and the budget to absorb the full annual cost of a 24/7 operation.
Choose co-managed if you have partial internal capability and need detection engineering overflow, but be crystal clear on SLAs for who owns triage during off-hours.
Choose fully managed if your team is under 5 security FTEs, you’re scaling through compliance milestones like SOC 2 or ISO 27001, or you simply can’t afford to lose 6 to 12 months building a SOC from scratch while threats don’t wait.
UnderDefense’s model lets you keep your SIEM while getting 24/7 SIEM operations, with no vendor lock-in, no platform migration, and no lost detection tuning when the contract comes up for renewal.
Provider quotes for managed SIEM pricing follow EPS, per-GB, or per-device models, and the model you pick decides how the cost fits your budget.
Q5: What Are the Real Benefits and Limitations of Managed SIEM?
The Operational Reality No One Talks About
Picture this: a security team of two or three people sitting behind a SIEM that produces thousands of events per second. They’re tuning detection rules against evolving threats, maintaining compliance evidence, covering nights and weekends, and still expected to run vulnerability scans and answer audit questionnaires. The result is a queue nobody can clear, detection decay, and a SIEM that becomes expensive shelfware.
When your most experienced analyst leaves, they take institutional knowledge about your environment with them, creating blind spots that adversaries are quick to exploit. Every rehire restarts the learning curve from scratch. Running a 24/7 in-house SOC means paying for tools, personnel, and operations around every shift.
The Benefits
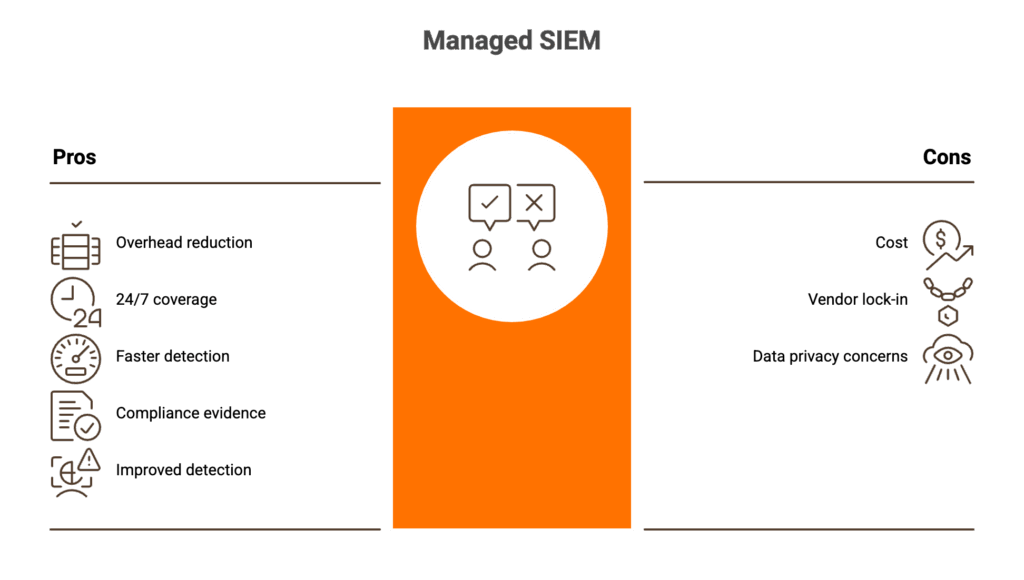
Managed SIEM directly addresses the operational math that breaks most internal teams:
- Operational overhead drops, because log management, rule tuning, parser maintenance, and platform upgrades move to dedicated engineers who do this full-time and never as a side task between firewall changes.
- You get 24/7 coverage without night-shift hiring. A self-managed SIEM with true 24/7 coverage requires at least 5 FTEs across shifts, and fully managed SIEM replaces that payroll with a provider fee.
- Detection gets faster, which matters when IBM’s 2026 Cost of a Data Breach Report puts the global average breach at $4.99 million. With active managed SIEM, detection takes minutes and containment takes hours.
- Compliance evidence becomes continuous. SOC 2, HIPAA, and ISO 27001 all require continuous log monitoring, and managed SIEM auto-generates the audit artifacts your compliance team would otherwise spend weeks assembling manually.
- Detection quality improves, because dedicated detection engineers writing rules full-time produce higher-fidelity alerts than a generalist IT admin writing Splunk queries as a side task.
The Honest Challenges
No approach is without tradeoffs. Here’s what you should evaluate honestly:
- Data privacy comes first: your logs leave your environment unless the provider supports on-prem or customer-cloud deployment. Ask specifically where your data lives.
- Integration complexity grows with legacy tools, which need connector support and API coverage. Not every managed SIEM provider handles legacy infrastructure well.
- Vendor dependency means switching providers forces you to re-tune all detection logic from scratch. If your detections live in the provider’s proprietary platform, you lose them when you leave.
- Shared responsibility leaves gray zones. Who owns escalation decisions? Who contains? If the SLA doesn’t spell it out, you’ll find out the hard way during an incident.
- Control is reduced for custom SOAR playbooks and sub-second automated workflows, which are harder to maintain through a third party. Teams with mature automation may feel friction.
When Managed SIEM Is the Wrong Choice
There are scenarios where managed SIEM genuinely doesn’t fit:
- Mature SOC with 5+ dedicated SIEM analysts and established detection engineering pipelines.
- Strict data sovereignty requirements in government, defense, or certain financial sectors where logs cannot leave specific boundaries.
- SIEM deeply customized with proprietary detection IP that represents years of institutional knowledge.
- Fully staffed 24/7 internal SOC where the marginal cost of adding SIEM operations is lower than outsourcing.
If none of these apply, and for most organizations under 5,000 employees they don’t, managed SIEM is the more cost-effective path.
How UnderDefense Addresses These Challenges
UnderDefense built its model around the top three challenges. Your logs stay in your data lake: Elastic, Splunk, wherever you own them. UnderDefense integrates with the tools you run, legacy infrastructure included. Its SLAs define who does what during incidents, with no gray zones and no “please investigate” escalations back to your team, and the 20-minute SLA response time for critical alerts is written down before the first alert fires.
Q6: Managed SIEM vs. MDR vs. XDR vs. SOC vs. MSSP: How Do These Models Differ?
Managed SIEM, MDR, XDR, SOC-as-a-Service, and MSSP are the five most conflated terms in security operations. They overlap, but serve different purposes. Choosing wrong means paying for capabilities you don’t need or missing the ones you do.
Defining Each Model
Managed SIEM is the outsourced operation of your SIEM platform: log management, detection rule tuning, monitoring, and maintenance. You own the SIEM; someone else runs it. The provider handles ingestion, parsing, correlation, and alert generation, but response capability varies widely.
MDR (Managed Detection and Response) spans broader detection and response across endpoints, cloud, identity, and network. It may or may not include SIEM management. The critical distinction: MDR providers are expected to respond to threats as well as detect them.
XDR (Extended Detection and Response) is a vendor-native platform unifying telemetry across multiple security layers into a single detection engine. It typically ties to a single vendor ecosystem: CrowdStrike Falcon Insight XDR, Palo Alto Networks Cortex XDR, or Microsoft Defender XDR. The tradeoff is integration depth versus vendor lock-in.
SOC-as-a-Service outsources the security operations center function: human analysts for monitoring, triage, and escalation. Think of it as renting a SOC team without building one internally. Coverage quality depends entirely on the analysts’ expertise and their familiarity with your environment.
MSSP (Managed Security Services Provider) is the legacy model: outsourced monitoring focused on alert forwarding from perimeter devices, typically without deep investigation or response. An MSSP watches your firewall logs and sends you an email when something triggers a signature.
Comparison of the Five Models
The table compares the five models on scope, response, and who they suit.
| Dimension | Managed SIEM | MDR | XDR | SOC-as-a-Service | MSSP |
|---|---|---|---|---|---|
| Core Focus | SIEM operation, log management, detection tuning | Detection and active response across the stack | Unified detection across vendor-native layers | Analyst monitoring, triage, and escalation | Alert forwarding from perimeter devices |
| Technology Scope | SIEM-specific (Splunk, Elastic, QRadar) | Endpoints, cloud, identity, network, SIEM | Vendor-native multi-layer (single ecosystem) | Varies by provider | Firewalls, IDS/IPS, basic log review |
| Vendor Flexibility | Works with customer-owned SIEM | Varies: some vendor-agnostic, some proprietary | Locked to vendor ecosystem | Moderate, depends on tools supported | Limited to supported devices |
| Response Capability | Detection and alerting; response varies | Full detection, investigation, containment | Automated response within vendor platform | Escalation-focused; limited direct response | Alert notification only |
| Alert Handling | Tuned correlation rules, enriched alerts | Triage, investigate, verify, and contain | Automated cross-layer correlation | Human triage and escalation | Forward raw alerts to customer |
| Compliance Support | Strong: log retention, audit trails, reporting | Varies by provider | Limited: platform-specific reporting | Minimal | Basic log retention |
| Typical Buyer | Orgs with a SIEM needing operational support | Teams needing 24/7 detection and response | Enterprises committed to one vendor stack | Teams needing analyst coverage without MDR | Budget-conscious orgs needing basic monitoring |
Where the Lines Blur
The confusion exists because these categories are converging. A strong MDR provider often manages your SIEM as part of the engagement. An XDR platform with a managed wrapper starts to resemble MDR. The practical question is whether a provider can detect threats across your entire stack, respond with context, and operate your existing tools without forcing replacement. The category label matters less.
How UnderDefense Fits
If your team owns a SIEM and needs 24/7 response on top of it, coverage matters more than the label. UnderDefense runs managed SIEM operations inside the Agentic AI SOC: you own your SIEM, and UnderDefense provides 24/7 detection, investigation, and response across the entire stack, covering what XDR platforms promise without the vendor lock-in.
UnderDefense integrates with the tools you already run, so you keep your current stack and still get investigation and response across all of it.
Q7: How Does Managed SIEM Support Compliance Frameworks Like SOC 2, HIPAA, and ISO 27001?
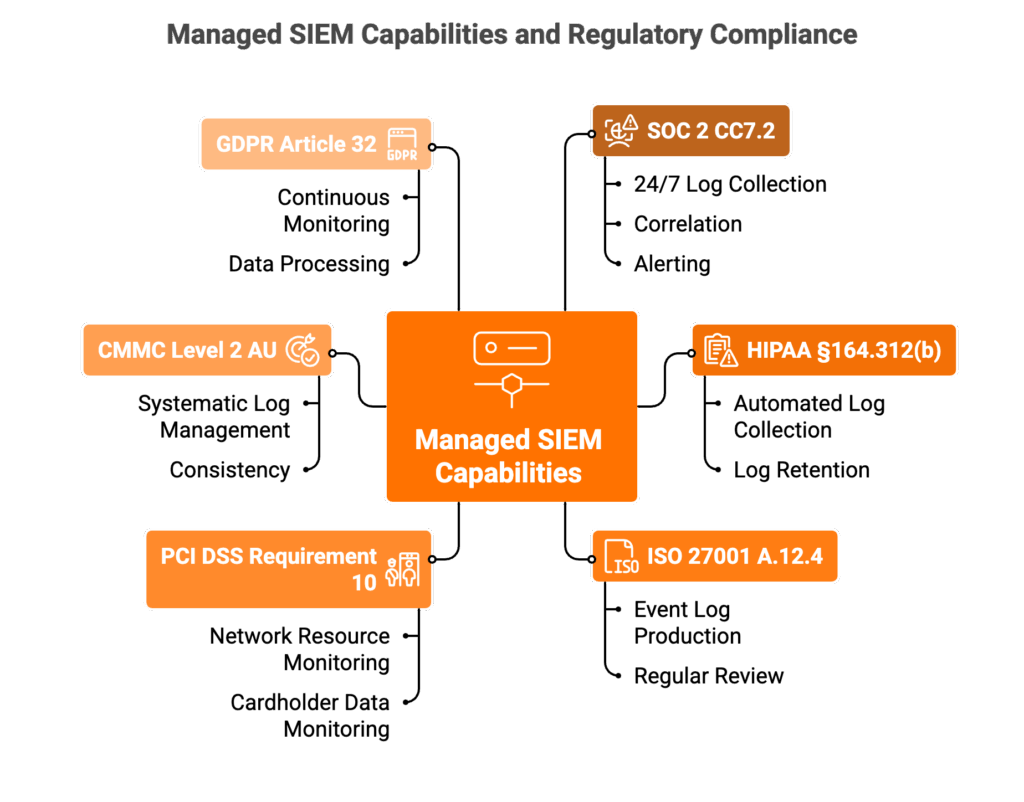
Managed SIEM directly satisfies the continuous monitoring, log retention, and incident detection controls required by SOC 2, HIPAA, ISO 27001, PCI DSS, and CMMC. For most organizations without a 24/7 security team, managed SIEM is the fastest path to audit-ready security operations.
Mapping Capabilities to Specific Controls
Here’s how managed SIEM capabilities map directly to the regulatory controls your auditors are asking about:
- SOC 2 CC7.2 requires continuous monitoring of security events. Managed SIEM provides 24/7 log collection, correlation, and alerting, which is exactly what auditors verify when checking CC7.2 compliance.
- HIPAA §164.312(b) requires audit controls that record and examine activity in systems containing electronic protected health information. Managed SIEM automates log collection from every relevant system and retains it for the period your policies require.
- ISO 27001 covers logging and monitoring in Annex A controls 8.15 and 8.16 of the 2022 edition. ISO auditors verify that event logs are produced, retained, and regularly reviewed, and managed SIEM handles all three continuously, all year.
- PCI DSS Requirement 10 requires you to log and monitor all access to system components and cardholder data. This is one of the most audit-intensive PCI requirements, and managed SIEM is purpose-built to satisfy it.
- CMMC Level 2 Audit and Accountability (AU) practices require systematic log management from defense contractors, which most internal teams struggle to maintain consistently.
- GDPR Article 32 requires appropriate technical measures, including monitoring. GDPR prescribes no specific tools, and demonstrating continuous monitoring of personal data processing is a practical requirement.
Why Compliance Teams Love Managed SIEM
The real value is operational efficiency. Your security team stops spending weeks before each audit manually assembling evidence from scattered tools, because managed SIEM generates compliance artifacts from the same telemetry used for daily threat detection. Same data, two outputs: security monitoring and audit evidence.
How UnderDefense Simplifies Compliance
When an audit is coming and the evidence lives in spreadsheets, your team needs it collected before the auditor asks. UnderDefense MAXI Compliance AI continuously maps the same live security data your SIEM collects to frameworks such as SOC 2, ISO 27001, and HIPAA, and your team shares posture with auditors through a Trust Center link.
The evidence comes from the unified telemetry that powers threat detection, so your audit documentation reflects what’s actually happening in your environment, which is what an auditor tests. MAXI Compliance AI has a Free package at $0, and paid packages start with Starter from $499 per month.
“Really like using UnderDefense MAXI platform, as it has everything from early risk detection and compliance to incident response automation and 24/7 protection with MDR.”
Serhii I., CEO, UnderDefense G2 Verified Review
The reviewer’s point is the one that matters for an audit: detection and compliance evidence come from one place.
Q8: What Should Security Leaders Evaluate Before Choosing a Managed SIEM Provider?
The Decision Dilemma
Choosing a managed SIEM provider means trusting an external team with your security telemetry, detection logic, and incident response. Choose wrong and you’re locked into a proprietary platform, dealing with opaque alert forwarding, or spending more time managing the provider than you would managing the SIEM.
The Wrong Way to Decide
Most security leaders evaluate based on brand recognition or integration count. This ignores the critical question: does the provider operate your SIEM, or just monitor the alerts it produces? When a threat is detected, can they respond, or do they escalate an email back to your team?
The Right Evaluation Framework: 7 Scored Criteria
Rate each provider 0 to 2 on these criteria. A score of 11+ means a genuine operational partnership. Below 8, you’re buying an alert feed and calling it managed SIEM.
- Do you retain ownership of the SIEM platform, or get locked into the provider’s?
- Are detection rules custom-tuned for your environment, or generic out-of-the-box?
- Can the provider contain threats by isolating endpoints and revoking credentials, or only notify you?
- Does the provider verify suspicious activity with users directly, or escalate raw alerts back?
- Is pricing published and predictable, or available only through “contact sales”?
- Is audit-ready evidence auto-generated, or run as a separate project?
- Does onboarding take weeks, or a 6-month professional services engagement?
Where UnderDefense Stands
UnderDefense, the publisher of this article, scores its own offer against the seven criteria below. Treat it as a vendor’s self-assessment, and run the same scoring on every provider you shortlist.
| Criterion | Score | Why |
|---|---|---|
| SIEM Ownership | 2/2 | Your SIEM stays yours: Elastic, Splunk, or others |
| Detection Engineering | 2/2 | Custom rules tuned to your environment |
| Response Capability | 2/2 | About 2 minutes from alert to triage |
| Alert Verification | 2/2 | Analysts verify with users via Slack, Teams, email, SMS |
| Pricing Transparency | 2/2 | Published price from $11 per device per month |
| Compliance Integration | 2/2 | MAXI Compliance AI maps live data to frameworks |
| Onboarding Speed | 2/2 | Live in days; tuning takes weeks to months |
| Total | 14/14 | 7 of 7 criteria at full score |
The onboarding row carries the honest caveat: G2 reviewers report that detection tuning took from a few weeks to a few months, so plan for full detection quality after the first quarter.
The Meta-Insight
The question that decides the choice is which provider can respond to threats the way a dedicated security team would. Integration counts matter less. That’s the shift from buying an alert feed to hiring an operational partner.
“Their team provided us with clear and detailed insights into security vulnerabilities, along with practical recommendations on how to fix them. This level of transparency made it easy for our team to take action and strengthen our security.”
Arman N., CTO, UnderDefense G2 Verified Review
UnderDefense reports that across six years, no ransomware incident reached impact. Detection without human-driven response is just expensive alerting.
Q9: What Does Day 1 to Day 90 With a Managed SIEM Provider Actually Look Like?
One of the biggest unknowns is what happens after you sign. Most providers are deliberately vague on onboarding timelines, and security leaders end up waiting months for value, frustrated, exposed, and unable to hold anyone accountable. SIEM deployments stall when requirements and use cases aren’t agreed upfront. Here’s what a well-executed managed SIEM onboarding should look like, and the milestones you should use to keep your provider honest.
Phase 1: Days 1 to 14, Discovery and Integration
This is where the real work starts, and where most providers already fall behind. A good managed SIEM partner spends the first two weeks learning your organization before plugging in connectors.
- A toolset audit takes a full inventory of your existing security stack, covering EDR, firewalls, cloud platforms, and identity providers.
- Log source identification and prioritization puts critical assets and high-risk users first, because not every source matters equally.
- API, agent, and syslog connectors are deployed across your environment, with data flow validation at each integration step.
- Environment baseline profiling establishes what “normal” looks like for your org, including who your VIPs are, what legitimate admin activity looks like, and when developers run scripts on weekends.
- Dedicated Slack or Teams channels are set up for real-time escalation, so nothing disappears into email threads.
A good provider invests these first two weeks learning your org because detection rules are useless without organizational context. If your provider skips this step, everything downstream suffers.
Phase 2: Days 15 to 30, Detection Tuning and Noise Reduction
This is where managed SIEM starts proving its value, or exposing its weaknesses.
- Custom detection rules are deployed and mapped to your specific threat profile.
- False positive suppression cuts noise, so analysts work the incidents that matter.
- A MITRE ATT&CK coverage gap analysis identifies blind spots in your detection logic.
- An initial threat hunting sweep covers your environment.
- Compliance reporting is configured for SOC 2, HIPAA, and ISO 27001, with automated evidence.
Validation Milestone
By Day 30, run simulated attacks (Atomic Red Team, MITRE Caldera, or Ransomware Monkey) to confirm detection coverage. If your provider can’t demonstrate that detections actually fire against real attack techniques, you have a dashboard and no security program. UnderDefense works to the same milestones, and reviewers report that its detection tuning takes from a few weeks to a few months, so treat Day 30 as validated coverage and Day 90 as full tuning.
Phase 3: Days 31 to 90, Operational Maturity
This is where good providers separate from great ones. The tuning doesn’t stop at Day 30. It accelerates.
- Detection refinement continues from real-world alert data and threat intelligence.
- Monthly security posture reviews with your team are structured conversations about risk reduction, with dashboards as supporting material.
- A tabletop exercise with your internal team validates incident response workflows from start to finish.
- A continuous tuning feedback loop turns every false positive into a better detection rule.
- The environment reaches a full 24/7 monitored state with documented SLAs that are active and measurable.
Hold Your Provider Accountable
Some managed SIEM buyers describe their provider’s platform as a black box: they trust that logs are being ingested, but they cannot query the data or judge the reporting themselves. Ask to see the platform before you sign.
If your managed SIEM provider can’t show you documented MITRE ATT&CK coverage, published SLA metrics, and a clear audit trail by Day 90, they’re selling monitoring and calling it managed security. The goal is operational maturity: your team reviews confirmed incidents, and the raw alerts stay with the provider.
Q10: How Do the Leading Managed SIEM and SOC Providers Compare?
Managed SIEM and SOC-as-a-Service providers in 2026 differ in four ways: architecture, pricing model, response depth, and whether you keep ownership of your SIEM.
What Separates Providers in 2026
Managed SIEM has evolved well beyond log monitoring. The real differentiators now are integration flexibility (vendor-agnostic vs. proprietary lock-in), response depth (detection-only vs. full containment), pricing transparency (published vs. contact-sales), and whether you retain ownership of your SIEM platform and the business logic you’ve built inside it.
As I’ve seen across hundreds of engagements, and as JR, former CISO of Micron and Darktrace, put it in a recent conversation: if you build custom correlation rules and automation inside a vendor’s proprietary system, that logic doesn’t come with you when you switch providers. You start the tuning process all over again.
Selection Criteria That Actually Matter
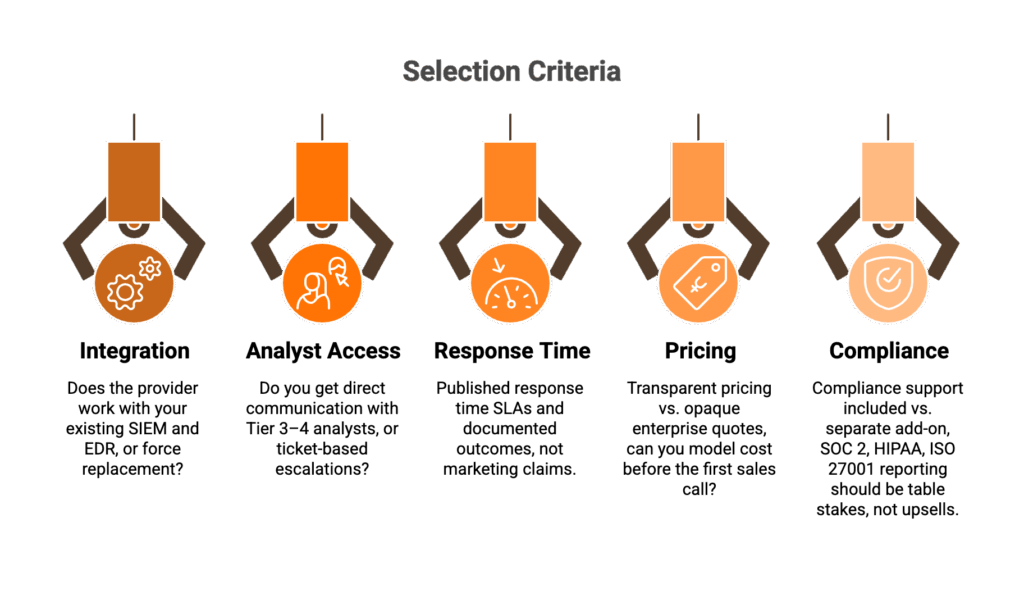
Ask every provider on your list these five questions:
- Does the provider work with your existing SIEM and EDR, or force a proprietary stack on you?
- Do you get direct communication with Tier 3 to 4 analysts, or ticket-based escalations?
- Does the provider publish response-time SLAs and documented outcomes you can check?
- Can you model the cost before the first sales call, or only through an opaque enterprise quote?
- Is compliance reporting for SOC 2, HIPAA, and ISO 27001 included, or sold as an upsell?
Where Each Provider Type Fits
Each provider type excels in a different scenario. Single-vendor platforms work well for organizations that want one vendor and will adopt its proprietary stack. Endpoint-native managed services are strongest where the EDR is the primary telemetry source. Providers that converge SIEM and MDR suit teams that want full technology access and vulnerability management in the same place.
UnderDefense fits organizations that want to protect their existing security investments with detection-to-response coverage, vendor-agnostic, and analysts who verify alerts directly with users before anything lands back on your team.
The right choice depends on your current security investments, team maturity, and operational model.
What This Analysis Is Based On
This analysis draws on UnderDefense’s published response times and pricing, its rating of 4.9 out of 5 from 57 reviews on G2 as of October 2026, and its work with 500+ enterprises.
Own a SIEM that nobody watches at 3 AM? Book a managed SIEM demo
Frequently Asked Questions
What is managed SIEM and how does it differ from running SIEM in-house?
Managed SIEM is a model where a provider deploys, tunes, monitors, and manages your SIEM, from log collection and correlation to detection engineering and incident escalation. In-house, your team carries all of that work and the 24/7 staffing behind it. With managed SIEM, you can keep ownership of your SIEM and data while the provider supplies the expertise.
What services should be included in a fully managed SIEM engagement?
A full engagement covers seven areas: 24/7 log monitoring and correlation, detection engineering, threat intelligence, human-led triage, compliance reporting, SIEM platform management, and incident escalation with context. Many providers bundle only monitoring and platform maintenance and charge extra for the rest, so check each item in the contract.
How much does managed SIEM cost compared to building an in-house SOC?
A self-managed SIEM with true 24/7 coverage needs at least five FTEs across shifts, plus licensing, training, and rule tuning. Managed SIEM replaces most of that payroll with a provider fee that depends on log volume, environment complexity, and service tier. UnderDefense publishes a starting price from $11 per device per month, and its paid tiers are quoted.
What is the difference between managed SIEM, MDR, XDR, and MSSP?
Managed SIEM is the outsourced operation of your SIEM. MDR covers detection and active response across endpoints, cloud, identity, and network. XDR is a vendor-native platform tied to one ecosystem. SOC-as-a-Service rents analyst coverage, and an MSSP forwards alerts from perimeter devices. The practical test is whether a provider can detect across your stack and respond with context.
How does managed SIEM help with SOC 2, HIPAA, and ISO 27001 compliance?
Managed SIEM covers the continuous monitoring, log retention, and incident detection controls in SOC 2 (CC7.2), HIPAA (§164.312(b)), ISO 27001 (Annex A 8.15 and 8.16), and PCI DSS (Requirement 10). It also produces audit evidence from the same telemetry your team uses for threat detection, so nobody rebuilds it before each audit.
What does the onboarding process look like with a managed SIEM provider?
A well-run onboarding has three phases. Days 1 to 14 cover discovery and integration, Days 15 to 30 cover detection tuning and noise reduction, and Days 31 to 90 build operational maturity through refinement, posture reviews, and tabletop exercises. By Day 90, ask for documented MITRE ATT&CK coverage and published SLA metrics.
What should security leaders evaluate before choosing a managed SIEM provider?
Score each provider from 0 to 2 on seven criteria: SIEM ownership, detection engineering, response capability, alert verification, pricing transparency, compliance integration, and onboarding speed. A total of 11 or more points to a genuine operational partnership; below 8, you’re buying an alert feed. The deciding question is whether the provider can respond the way your own team would.
Can we keep our existing SIEM platform with a managed SIEM provider?
Yes, with providers that operate the SIEM you own. Others require migration to their platform, and you lose custom detection tuning, correlation rules, and business logic when you switch.
UnderDefense operates your existing Splunk, Elastic, or other SIEM through 250+ integrations, so your detection engineering stays with you at renewal.