Manual Penetration Testing Services with a Free Retest

Pen testing services run by certified ethical hackers. We exploit vulnerabilities the way attackers would, report every finding with evidence and fixes, and retest for free once you've patched.
top clutch.co penetration testing 2025 SystemSecurity BestSupport QualityOfSupport gartner peer insight rating image 123412340 (1) scawards
Penetration Testing
Market leaders trust us
yayPay
betssongroup
RemotePass
helpware
enersponse
enersponse
enersponse
enersponse
Bill_Melisa_Gates_Foundation
matrix42
matrix42
Volkswagen
accedian
CohnReznick
avenga
invicti
onit
Blackberry
shelf
materialise
rydoo
skelar
yayPay
betssongroup
RemotePass
helpware
enersponse
matrix42
Volkswagen
accedian
CohnReznick
avenga
invicti
shelf
materialise
rydoo
skelar

Pen testing services done better by UnderDefense

Pentest services run by people
We perform every test manually. Our ethical hackers follow a penetration testing methodology built on PTES, OSSTMM, and the OWASP Web Security Testing Guide, then document each finding with proof and clear remediation steps.
Direct access to domain experts
You talk directly to the pentesters working on your scope. Ask why a finding matters, how to fix it, and which attack paths deserve a deeper test next time.
Testers backed by IR and vCISO teams
Ethical hackers work alongside our incident response and vCISO teams, so the findings come with business context and a hardening roadmap. If you also run UnderDefense Agentic AI SOC, our analysts turn those findings into detections.
Free post-remediation testing
After your team fixes the findings, we retest the same assets at no extra cost and confirm every gap is closed. You then receive an attestation letter to share with auditors, partners, and customers.

One partner for every type of penetration testing service

Cloud security assessment

Examine your cloud-based systems to eliminate configuration errors, irrelevant services, or missing security patches, and 100% comply with the OWASP Cloud Security Project guidelines.

Details

Web app pen test

Discover gaps and weaknesses in your web apps. Test architecture and design, see if your APIs and source code follow software engineering best practices, and ensure your users’ data is safe.

Details

Mob app pen test

Protect your data centers, networks, servers, and other assets used by mobile devices. Test app architecture, design, APIs, and services to detect vulnerabilities and address them immediately.

IoT pen test

Test all the devices and sensors within your IoT ecosystem to unleash architectural gaps and vulnerabilities, allowing hackers to gain access to other devices or your system.

Penetration testing for compliance

Prepare for a compliance audit? Ensure your policies meet the requirements. Get a detailed report, expert remediation support, and free post-remediation analysis to achieve your growth goals.

Details

Internal pen test

Investigate the impact hackers may have on your systems, operations, and entire business being directly inside your environment. Analyze what data is at risk and take proactive measures.

External pen test

Check if criminals can use email services, APIs, sites, and apps to enter your infrastructure. See how far they may move within your network and prevent any possible malicious actions immediately.

Network penetration testing

Prepare your business for the future of work. Keep your networking devices, clouds, email services, and all remote devices under control regardless of global situations and external conditions.

Data security

Check the encryption quality at every stage of your data life cycle. Prevent compliance violations and unauthorized access to personal information of your customers and employees.

Social engineering

See how your team reacts to hackers’ manipulative techniques. Evaluate the security awareness level among your staff & c-suite and conduct security awareness training to help them maintain good cyber hygiene.

Red teaming

Assess your readiness for real-world attacks. Perform holistic tests focusing on all areas of your organization, including people, technology, and processes. Identify how they may be abused and exploited.

Details

Wireless

Explore your Wi-Fi, WLAN, and Bluetooth connections to prevent piggybacking, evil twin attacks, wireless sniffing, and unauthorized access to corporate devices.

Cloud security assessment

Examine your cloud-based systems to eliminate configuration errors, irrelevant services, or missing security patches, and 100% comply with the OWASP Cloud Security Project guidelines. Details

Web app pen test

Discover gaps and weaknesses in your web apps. Test architecture and design, see if your APIs and source code follow software engineering best practices, and ensure your users’ data is safe. Details

Mob app pen test

Protect your data centers, networks, servers, and other assets used by mobile devices. Test app architecture, design, APIs, and services to detect vulnerabilities and address them immediately.

IoT pen test

Test all the devices and sensors within your IoT ecosystem to unleash architectural gaps and vulnerabilities, allowing hackers to gain access to other devices or your system.

Penetration testing for compliance

Prepare for a compliance audit? Ensure your policies meet the requirements. Get a detailed report, expert remediation support, and free post-remediation analysis to achieve your growth goals. Details

Internal pen test

Investigate the impact hackers may have on your systems, operations, and entire business being directly inside your environment. Analyze what data is at risk and take proactive measures.

External pen test

Check if criminals can use email services, APIs, sites, and apps to enter your infrastructure. See how far they may move within your network and prevent any possible malicious actions immediately.

Network penetration testing

Prepare your business for the future of work. Keep your networking devices, clouds, email services, and all remote devices under control regardless of global situations and external conditions.

Data security

Check the encryption quality at every stage of your data life cycle. Prevent compliance violations and unauthorized access to personal information of your customers and employees.

Social engineering

See how your team reacts to hackers’ manipulative techniques. Evaluate the security awareness level among your staff & c-suite and conduct security awareness training to help them maintain good cyber hygiene.

Red teaming

Assess your readiness for real-world attacks. Perform holistic tests focusing on all areas of your organization, including people, technology, and processes. Identify how they may be abused and exploited. Details

Wireless

Explore your Wi-Fi, WLAN, and Bluetooth connections to prevent piggybacking, evil twin attacks, wireless sniffing, and unauthorized access to corporate devices.
160+

Tests annually

1440+

Vulnerabilities detected per year

2-4

Weeks an average pentest lasts

Expect personalized cyber security penetration testing services

Black box
Conditions: We try to penetrate the system and identify other ways to harm your business by having minimum information about your company
Value: Black box pentesting service simulates a real-world attack and helps identify technical vulnerabilities and human-related security issues
Gray box
Conditions: We attack your business having general information about your infrastructure and system, including logins and passwords
Value: Gray box pen testing service is the golden mean between quality and price. It’s cheaper and faster compared to the black box approach
White box
Conditions: We try to hack your organization knowing logins and passwords, and having full access to an application or system architecture and code
Value: White box penetration test service allows you to detect hidden vulnerabilities that may go unnoticed during other types of pentests

Not sure what type of security testing service you need?

Discuss your priorities with our expert

Go beyond traditional pen testing services with UnderDefense

Detailed report with clear remediation guidelines
Benefit from the most comprehensive report on the market. Use the document to explain to the c-level and stakeholders how vulnerabilities may harm your business. Share it with your IT team to help them quickly solve the issues using tactical recommendations and provided artifacts.
Download report sample
Professional attestation letter
Proof to your partners, auditors, prospects, and customers that your business is security-conscious and forward-looking with the attestation letter from UnderDefense. Gain a written confirmation of your security level describing the scope of work, cybersecurity assessment results, and overall security rating.
Download letter sample
Additional free services for better outcomes
Get expert penetration testing consulting services throughout the entire remediation process. Don't overpay for the same service: post-remediation assessment is free, and our pentest pricing tiers show what each engagement includes.
Contact sales

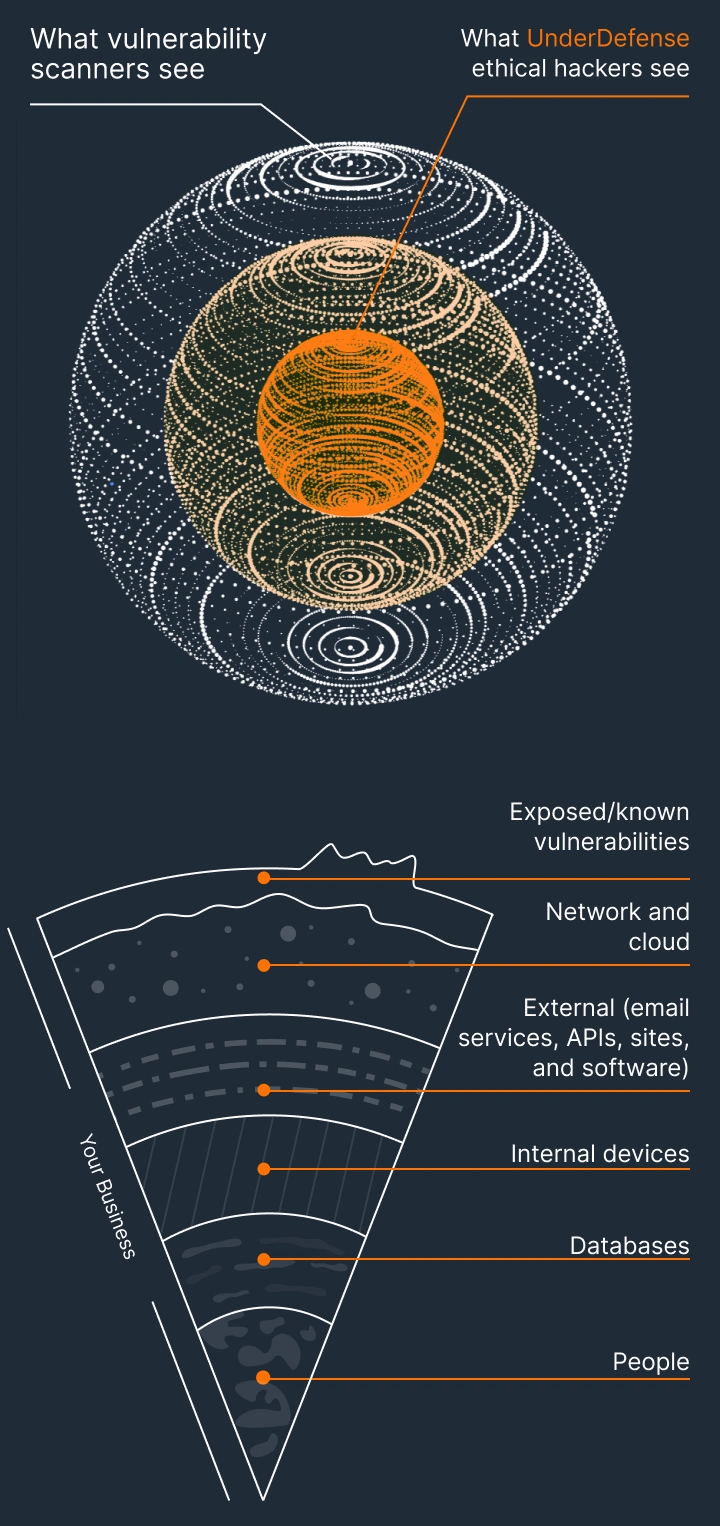
With UnderDefense you see more than scanners do

Access the all-in-one UnderDefense MAXI platform

Create a free UnderDefense MAXI account and improve your business security immediately by:

  • Conducting a comprehensive analysis of your external risks
  • Staying compliant with strict industry regulations and standards
  • Collecting all your penetration testing reports in one place
  • Monitoring and adjusting your security perimeter 24/7
Try Now Free

Our customers say it best

Named as a high Perfomer Incident Response System Security by G2 Crowd
4.8
“Not having to worry about ransomware, alert overload and reporting. Getting a clear view of my security posture, where the threats are coming from and how they are handled. They literally took care of all our problems.”
Read Reviews
Managed Detection and Response (MDR)
4.9
“Holistic approach, exceeding requirements with added value and cost savings; smooth transition to Crowdstrike EDR and Elastic SIEM implementation; flexibility with a 120-hour incident response retainer, surpassing the standard 40 hours.”
Read Reviews
Named as a Top Cybersecurity Company 2025 by Clutch
5.0
“UnderDefense impressed us with their ability to tailor their services to our unique needs and challenges. They didn't simply provide a one-size-fits-all solution, but instead took the time to understand our specific environment and requirements.”
Read Reviews

Our awards and certifications

top clutch.co penetration testing 2025
SystemSecurity BestSupport QualityOfSupport

Get tested. Verified. Trusted.

Discover security gaps and manage them on time
Gain a comprehensive overview of your blind spots throughout your IT environment, processes, and people. Remediate existing vulnerabilities and reduce your attack surface for current and future threats.
Evaluate your security investments and prioritize budgets
Review the effectiveness of your current investments. Find out what's working or not, prevent wasteful expenditures, and identify priority investment directions considering the evolving threatscape.
Ensure business continuity and data safety
Approach your business security proactively and eliminate any possibility of downtime caused by ransomware or breach. Ensure business stability, protect customer data, and maintain good relationships with partners and investors.
Discover security gaps and manage them on time
Gain a comprehensive overview of your blind spots throughout your IT environment, processes, and people. Remediate existing vulnerabilities and reduce your attack surface for current and future threats.
Evaluate your security investments and prioritize budgets
Review the effectiveness of your current investments. Find out what's working or not, prevent wasteful expenditures, and identify priority investment directions considering the evolving threatscape.
Ensure business continuity and data safety
Approach your business security proactively and eliminate any possibility of downtime caused by ransomware or breach. Ensure business stability, protect customer data, and maintain good relationships with partners and investors.

Frequently asked questions

What is penetration testing?

A penetration test, also known as pen test services or ethical hacking, is a simulated cyberattack that helps organizations detect and highlight weaknesses and vulnerabilities in their security postures. This proactive cybersecurity technique allows business owners to assess the hackability of their networks, systems, processes, and people and take the necessary actions to prevent that.

What's the difference between penetration testing services and vulnerability assessment?

Vulnerability assessment is the technique used to identify, classify, and prioritize issues in infrastructures, apps, and systems. It is usually conducted using automated testing tools, including network vulnerability scanners.

Penetration testing goes a step further. Ethical hackers manually exploit what the scan finds, chain weaknesses together, and show how far an attacker could get. Many teams scan continuously and run a penetration test at least once a year or after major changes.

Is penetration testing performed manually or with automated tools?

Both, with the weight on manual work. Our pentesters run automated scanners at the start for coverage, then do the core work by hand: they verify each finding, rule out false positives, exploit what's real, and chain weaknesses the way an attacker would. Access-control gaps and business-logic flaws rarely show up in a scan, which is why every UnderDefense engagement includes manual testing by certified ethical hackers (CEH, OSCP, OSCE).

What's included in a penetration testing report?

Every UnderDefense report has an executive summary for leadership and a technical section for your IT team. Each finding comes with its risk level, proof of exploitation with screenshots or video, steps to reproduce it, and remediation guidance. After the free retest, you also get a letter of attestation that confirms the scope, the results, and your overall security rating.

Why is penetration testing important for compliance?

PCI DSS v4.0.1 (Requirement 11.4) requires internal and external penetration testing at least once every 12 months and after any significant change. SOC 2 and ISO 27001 don't prescribe a pentest, but auditors often ask for one as evidence that your controls work. Under DORA, financial entities named by their regulator run threat-led penetration testing every three years. Every UnderDefense engagement ends with a report and a letter of attestation you can hand to your auditor for ISO 27001, SOC 2, PCI DSS, or HIPAA.

What types of penetration testing do you offer?

We test external and internal networks, web and mobile applications, APIs, cloud environments, IoT devices, and wireless networks, and we test people through social engineering. For a full attack simulation across people, processes, and technology, we run red team engagements. Each test can run as a black box, gray box, or white box engagement, and cloud penetration testing has its own dedicated page.

How much does a penetration testing service cost?

Cost depends on the type of test, the scope (the number of IPs, applications, and cloud accounts), and the testing approach (black, gray, or white box). Engagements start at $5,000 for an external perimeter test, and our pentest pricing page shows what each tier includes. For an exact figure, share your scope and we'll send a free quote.

How long does a penetration test take?

On average, cyber security testing services take around 3 working weeks, depending on the size and complexity of an organization. A typical timeline for a pentest includes the following stages:

  1. Planning. Together with you, we define and document test objectives, scope of work, start date, and engagement model for the pen test as a service team.

  2. Reconnaissance. Depending on the selected pen testing as a service methodology, we collect the necessary information regarding targeted apps and infrastructure, roles, credentials, business logic, and more.

  3. Vulnerability discovery and exploitation. Our ethical hackers manually test the defined assets to identify security weaknesses, gaps in design and architecture, and process loopholes. They exploit all the discovered vulnerabilities to evaluate the risk level of each issue and potential harm to the business.

  4. Reporting. The UnderDefense pen testing team creates a detailed report on all the findings, including all the evidence and artifacts like videos and screenshots. Additionally, our experts prepare a list of tactical recommendations on how to solve each vulnerability quickly and effectively. The working results are presented to the client.

  5. Free post-remediation testing. When all the improvements and changes are made, our ethical hackers are ready to check fixed vulnerabilities and retest the targeted assets. Upon completing the assessment, you get a professional attestation letter confirming your security rating.

How often should penetration tests be conducted?

We recommend performing pen tests at least once a year. However, you should also take into account the following factors:
  • Regulatory Requirements – Compliance standards like PCI DSS, ISO 27001, and SOC 2 may require more frequent testing.
  • Significant Changes – Conduct a test after major infrastructure, application, or system updates.
  • Incident Response – If a security breach occurs, a pen test can help identify vulnerabilities that were exploited.
  • Business Risk – High-risk industries or businesses handling sensitive data may need more frequent testing.
  • Threat Landscape – Emerging threats may necessitate additional assessments to stay ahead of attackers.

When can you start pen testing?

UnderDefense offers a flexible business approach that depends on the specific situation. We encourage you to contact our sales representatives and discuss how quickly you need us to get started.

What methodologies for a pentest as a service do you use?

We follow proven and globally recognized methodologies like the Penetration Testing Execution Standard (PTES), OWASP Top 10 Web Application Security Risks, OWASP Web Security Testing Guide, and the Open Source Security Testing Methodology Manual (OSSTMM).

Do you store the results of penetration services?

We send you the testing results via an encrypted channel and do not collect or store the results after that.