





MDR Services That Detect, Investigate and Respond in 15 Minutes, Without Replacing Your Stack
24/7 human-led detection and response on the tools you already own, with compliance evidence built in.
Cut costs by 30%
The problems most security teams are stuck with
If any of these sound familiar, you don't have a tools problem. You have a response problem, and that is exactly what MDR is built to fix.
Alert overload with no one to action it
A deluge from every tool, no context, and a ticket that lands in your queue Monday morning while the real signal stays buried.
You can't staff a 24/7 SOC
Hiring and retaining analysts around the clock isn't realistic on your budget, and nights and weekends are when attackers move.
A compliance deadline with no evidence
SOC 2 or ISO 27001 is due and you have nothing to hand an auditor: no monitoring, no logs, no reporting trail.
"24/7" that only notifies, never acts
A bot leaves you a ticket instead of containing the threat, so dwell time keeps running while you sleep.
Tool sprawl with no single picture
You already own the EDR, the SIEM, the cloud logs. No one is correlating them into one clear, prioritized view.
Rip-and-replace vendor lock-in
Providers that force you onto their agents and their SIEM, writing off the stack you already invested in and making it painful to ever leave.
Why UnderDefense is among the best MDR services in 2026
Six things you can verify before you sign, not after.
All-encompassing protection, 24/7
Ensure round-the-clock protection across all environments, from clouds and networks to critical data. Focus on driving your innovations forward while your security is in expert hands.
Risk mitigation via automated remediation
Experience lightning-fast incident resolution through automation. Gain full visibility into your security posture, direct access to our SOC, and dynamic vulnerability reporting.
Your existing tools work effectively as an orchestra
We seamlessly integrate with the tools you already have. No disruptive transitions, we'll automatically take care of data synchronization, ensuring a smooth and efficient process.
Threat detection crafted for your business and use cases
From custom Splunk applications to unique SIEM correlation rules and best practices for fortifying cloud identity platforms, UnderDefense MDR is accessible and affordable.
Threat hunters as an extension or fully remote team
Our seasoned threat hunters tackle existing threats and provide personalized guidance on prevention strategies, amplifying your team with security experts and scaling to fit your needs.
360° threat visibility
Control every corner of your environment. Our MDR service gives you complete visibility across your network, endpoints, cloud, Kubernetes, and everything in between. No blind spots.
Trusted by Security Leaders
What our customers say

"We fully automated T1-T2 manual triage with UnderDefense. AI SOC filters the noise so my team can focus on complex hunt missions and strategic security. We scaled our capacity 10x overnight, not by hiring, but by making our analysts investigators again."

"Zero ransomware cases and a 2-minute triage SLA. Agentic AI mapped our VIPs and high-value assets with surgical precision. It transformed how our board views security, shifting from a cost center to a strategic enabler of business resilience."
Excellence.
Our minimum bar for client delivery.

UnderDefense vs. the field
Tap any row for the detail. The points that decide the deal, at a glance.


One partner for your whole security program
MDR is the core. These services plug into the same 24/7 team and platform.
Managed Extended Detection & Response (MXDR)
Extended detection and response across endpoints, network, cloud, email, and identity, run 24/7 by our SOC.
Learn more →Managed EDR
Your CrowdStrike, SentinelOne, or Microsoft Defender, expertly tuned and managed with 24/7 triage and response.
Learn more →MDR for SaaS
Cloud-native detection and response for SaaS companies, with the security evidence enterprise buyers expect.
Learn more →MDR for Healthcare
HIPAA-aligned detection and response protecting PHI, EHR systems, and clinical operations around the clock.
MDR for FinTech
Detection and response built for financial platforms, with the compliance evidence regulators and partners require.
Learn more →MDR Integrations
250+ integrations across your EDR, SIEM, cloud, and identity stack. See everything we connect to.
Your go-to MDR provider with a 100% ransomware-free record
Our MDR solution isn't one-size-fits-all. Unlike typical MDR providers, we fine-tune and optimize your existing tools to work smarter, not harder. With full tool ownership on your side, UnderDefense offers one of the most effective MDR solutions on the market.
Get your custom MDR quote
Tell us about your environment. We'll come back with a tailored proposal and a 30-day onboarding plan, scoped to your stack.
- A clear proposal, not a sales gauntlet
- Onboarding in 2 to 3 business days
- Start free with MAXI, no credit card
How MDR services work at UnderDefense
MDR services at UnderDefense: capabilities, workflow, coverage and telemetry
You already own the SIEM, the EDR and the cloud logs. What you need from managed detection and response services is a team that works those signals around the clock and hands you a finished investigation you can act on. This guide explains what UnderDefense MDR services do for you, how the work flows from alert to response, which environments they cover and which telemetry they read.
Core capabilities of MDR services
Each capability answers a gap security leaders describe in their own words: a 24/7 rota they cannot staff, alerts that arrive without context, and investigations a provider hands back unfinished.
- Every alert investigated, around the clock. UnderDefense analysts investigate every alert, nights and weekends included, with automation handling the repetitive triage.
- The user confirms before anyone escalates. Analysts check suspicious activity with the affected user over Slack, Microsoft Teams, email or SMS, so your team receives the incident together with the answer.
- Threat hunting and detection engineering. Analysts hunt across your telemetry and tune detection rules to your environment, so the alerts that reach you are specific to how your business runs.
- Response actions you agree in advance. Containment steps, such as isolating a host or disabling an account, follow the actions defined in your contract.
- Work you can audit. Every investigative step is visible, so you can check what was done and why.
- Compliance evidence as a by-product. Live security data maps to frameworks such as NIST, SOC 2, ISO 27001 and HIPAA, so audit evidence builds up while the service runs.
How does MDR work?
A managed detection and response service at UnderDefense runs in four stages, from the first connection to continuous improvement.
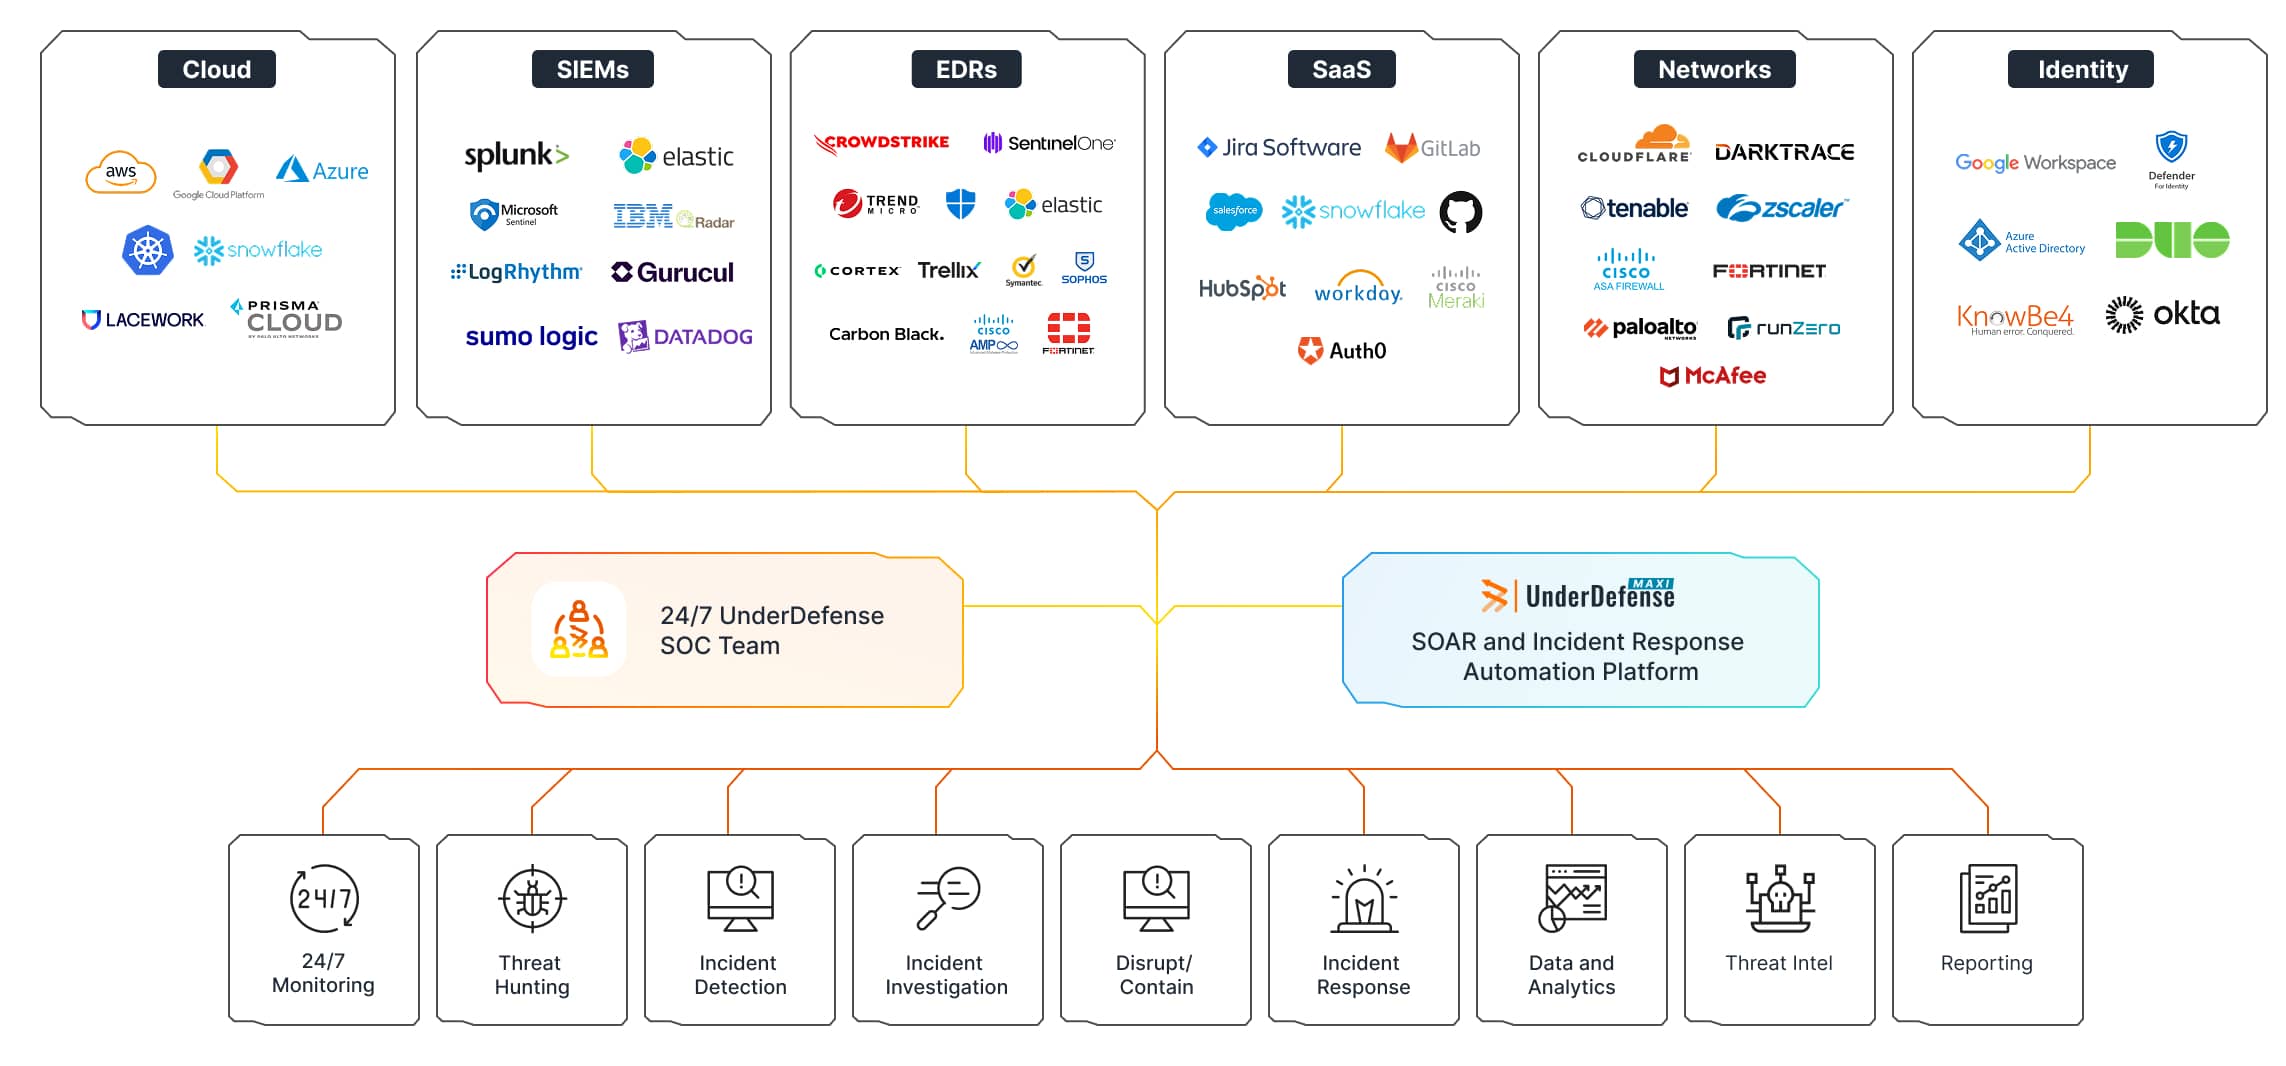
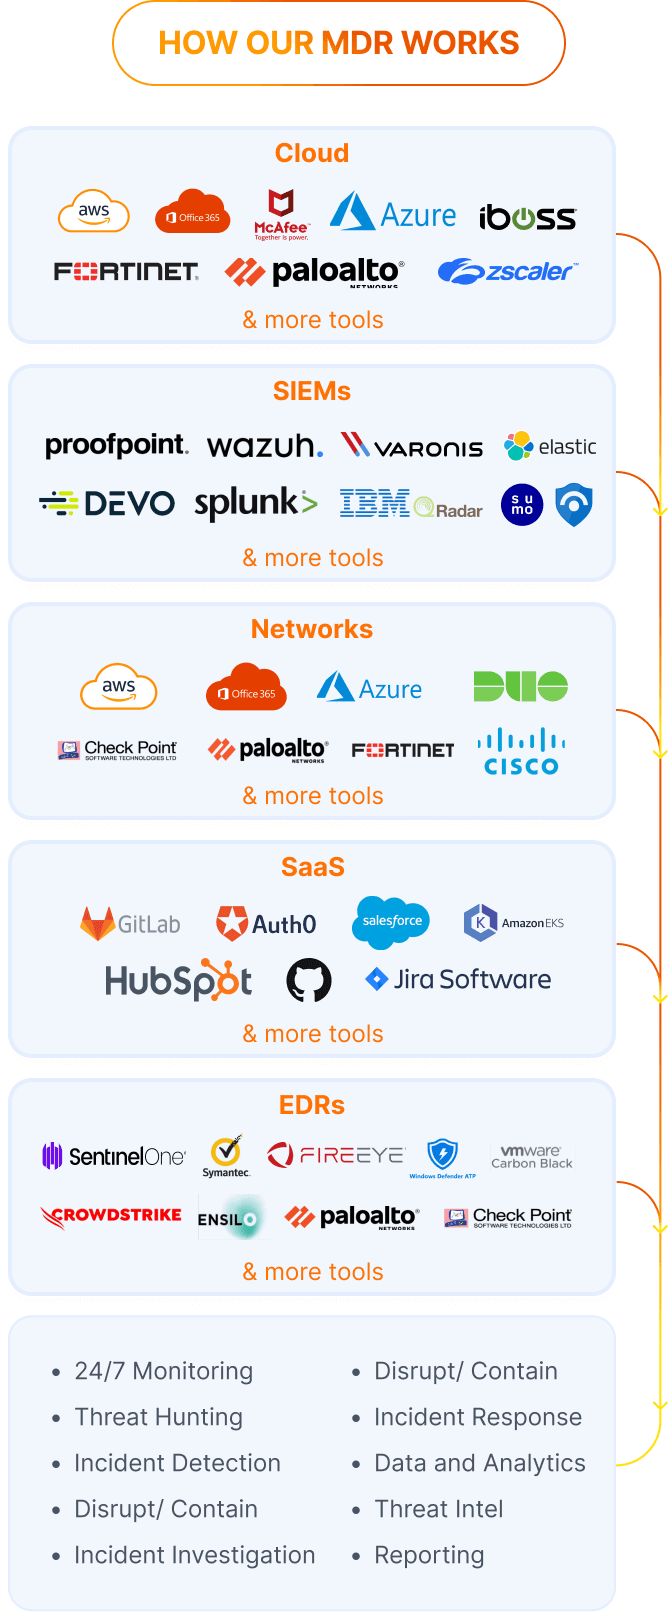
- Connect your stack. UnderDefense works on top of the SIEM, EDR, cloud and identity tools you already run, through 250+ integrations, and you keep ownership of every integration. Onboarding covers discovery, integration and security hardening, and detection rules are then tuned to your environment.
- Prioritize events. Automation triages each alert in about 2 minutes, and analysts confirm suspicious activity with the user before escalating, so the queue your team sees holds the incidents that matter.
- Respond within the actions you agreed. UnderDefense contains threats within 15 minutes. When a critical alert fires at 2 a.m., an analyst investigates and responds, and your team wakes up to the finished investigation.
- Report and improve. Monthly reporting shows what was detected and how it was handled, and detection engineering feeds every incident back into the rules.
What environments does UnderDefense cover?
Most stacks span cloud accounts and systems that never touch the internet. UnderDefense MDR services run in SaaS, hybrid, on-premises and air-gapped environments, so a closed network gets the same 24/7 coverage as your AWS, Azure or Google Cloud accounts. Telemetry from cloud, multi-cloud and on-premises systems comes together in one view, which means one investigation can follow an attacker from an office laptop to a cloud workload.
MDR telemetry: what the service reads
MDR services are only as good as the data they read. MDR telemetry at UnderDefense covers:
- endpoint detections and behavioral telemetry from the EDR you run, such as CrowdStrike or SentinelOne;
- SIEM logs and correlation data from Splunk, Microsoft Sentinel, Elastic, QRadar or Google SecOps;
- cloud activity from AWS, Azure and Google Cloud;
- identity signals from your identity provider;
- SaaS, email and network activity wherever you connect it.
Because UnderDefense works on top of these tools, nothing is ripped out, and you keep ownership of every integration if you ever leave.
Benefits of MDR for your business
For the business, the benefits of MDR come down to four outcomes:
- 24/7 coverage without funding a 24/7 team;
- your analysts' time back for the work only they can do;
- audit evidence ready when the auditor asks;
- no vendor lock-in, fewer tools and a lower cost of security.
For a fuller treatment, read the six key benefits of managed detection and response.
Questions to evaluate MDR providers
If you are still comparing MDR providers, start with four questions:
- When an alert fires at 3 a.m., does the provider investigate and act, or send you a notification?
- Which clock does the SLA measure: acknowledgement, triage or containment?
- Will the service run on the tools you already own, and do you keep them if you leave?
- Is compliance evidence part of the service or a separate purchase?
The full question set, with what a strong answer looks like, is in the free MDR Buyer's Guide.