





MAXI For MSSPs
Launch a 24/7 AI SOC service for every client — without building a platform of your own.
Humans augmented, not replaced.
Every alert from every client triaged around the clock — with evidence and a recommended response.
Your team escalates, closes and owns the client. A human makes every call that matters.
Turnkey compliance per client — only the frameworks each client needs.
Every alert from every client triaged around the clock — with evidence and a recommended response.
Your team escalates, closes and owns the client. A human makes every call that matters.
Turnkey compliance per client — only the frameworks each client needs.
Built and battle-tested inside a working MDR
Not a lab product — the platform the UnderDefense SOC works in every single day.
companies protected by the SOC that runs on MAXI — the same platform you get
of 24/7 security operations for regulated business
your clients' data needs to live — deployed in the region their regulator expects
of 92 teams at Splunk Boss of the SOC — the same team that runs on MAXI every day
Strong margin and recurring revenue opportunity
If you’re an MSP, UnderDefense not only offers superior security operations solutions, it also integrates effectively with your existing solutions to deliver a joint service to your customers. We offers:
- 01Sales and marketing support, enablement and training
- 02Strong margin and recurring revenue opportunity
- 03Predictable pricing, which allows MSPs to quickly scope customer needs
- 04Rapid and low-cost MSP onboarding for accelerated sales
- 05Simple billing processes for back-office efficiency
- 06Trouble ticketing integration for seamless handoffs of cybersecurity alerts
- 07Customizable and repeatable customer onboarding processes
Every new client adds a console, a queue and a night shift
A console per client
Every new stack means new runbooks, new training — and a slower analyst.
Drowning in alerts
Most of the queue is noise — but every alert burns analyst hours you pay for.
SLA held up by heroics
24/7 means 4–5 FTE per seat — the night shift eats your margin.
Reports by hand
Hours of unpaid QBR prep per client — and nothing sets you apart.
to thoroughly investigate one alert by Human Tier 1 analyst
to onboard a single client
of MSPs lack the people to onboard new clients
to keep one seat staffed 24/7
The same day in your SOC — before and after MAXI
The stack your clients run — already supported
SentinelOne · CrowdStrike Falcon · Microsoft Defender XDR · Palo Alto Cortex XDR · Sophos Intercept X · Fortinet FortiEDR · Trend Micro Vision One · VMware Carbon Black · Symantec EDR · Trellix EDR · Cisco Secure Endpoint · Elastic Defend · Cisco XDR
Splunk · Microsoft Sentinel · Elastic SIEM · Google SecOps · IBM QRadar · Datadog · Sumo Logic · LogRhythm · Logz.io · Coralogix · Gurucul · AlertLogic
AWS · Azure · Google Cloud · AWS GuardDuty · Wiz Defend · Orca · Prisma Cloud · Okta · Entra ID · CrowdStrike Identity · Microsoft 365 · Google Workspace · QRadar SOAR · ServiceNow · PagerDuty · Jira · Slack · Teams
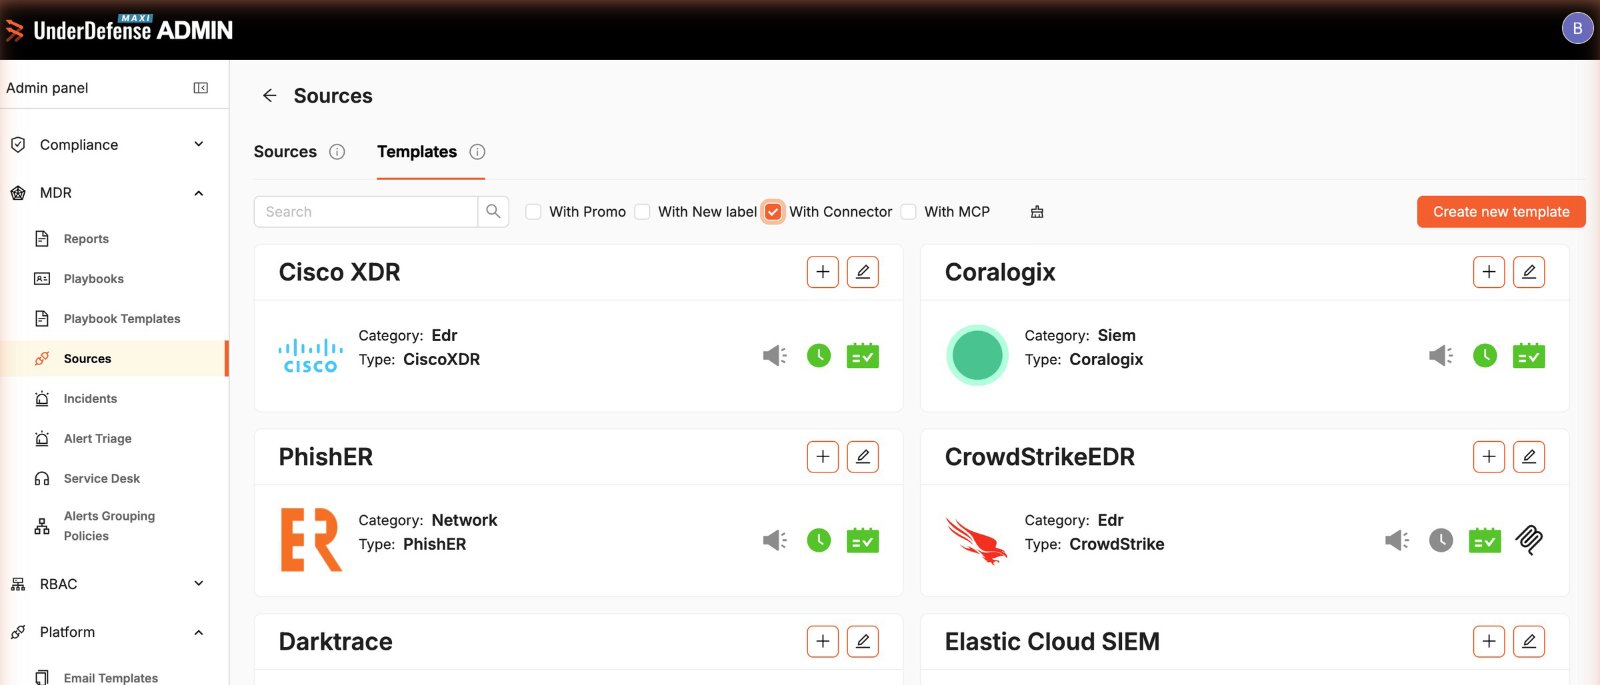
Understand your costs — down to every client and run
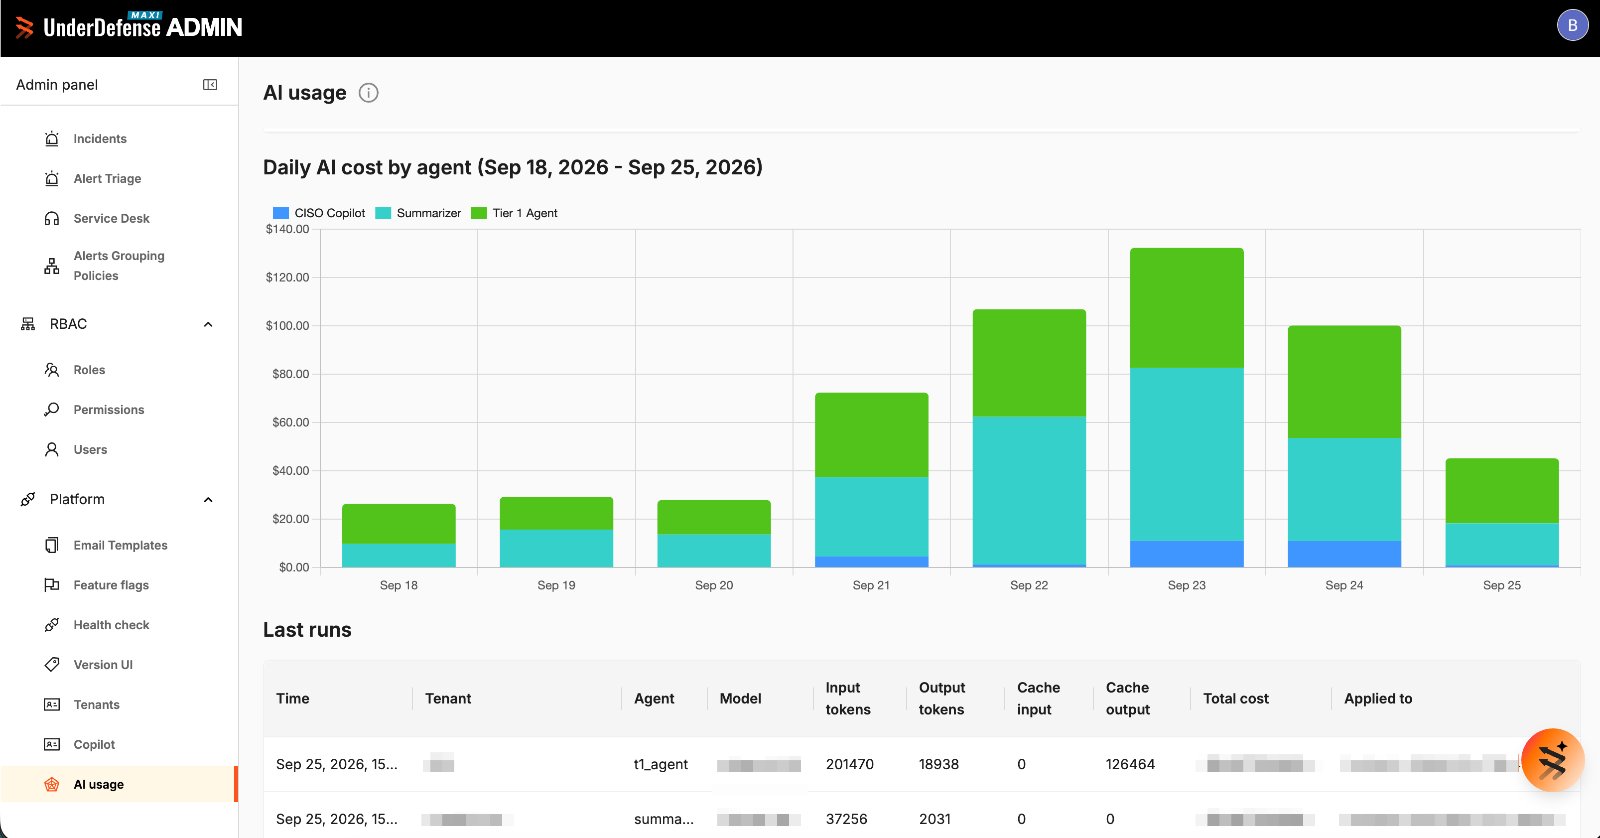
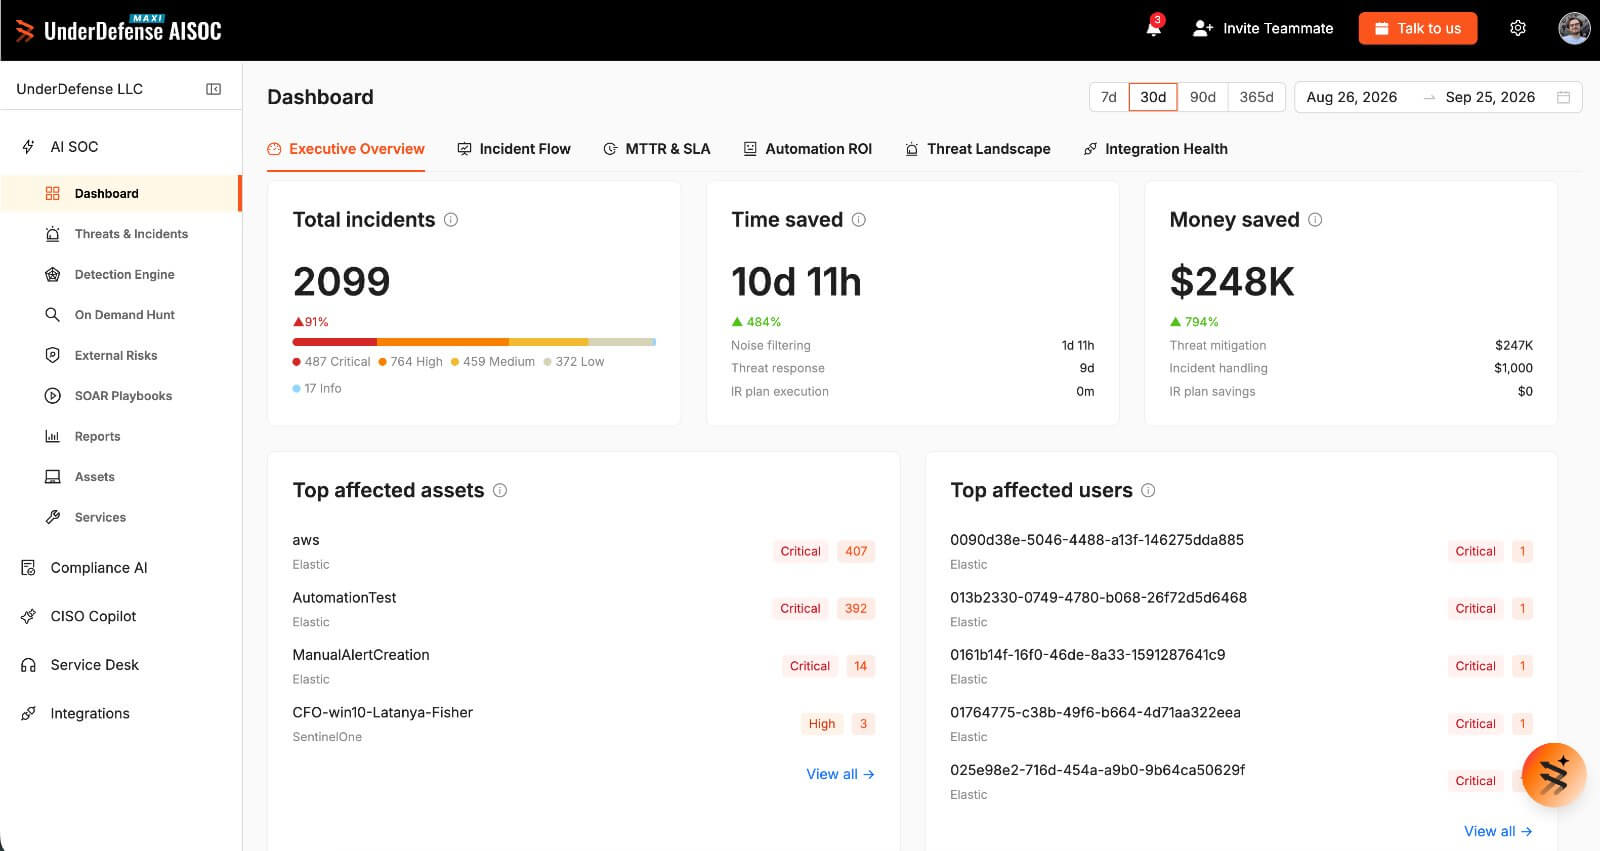
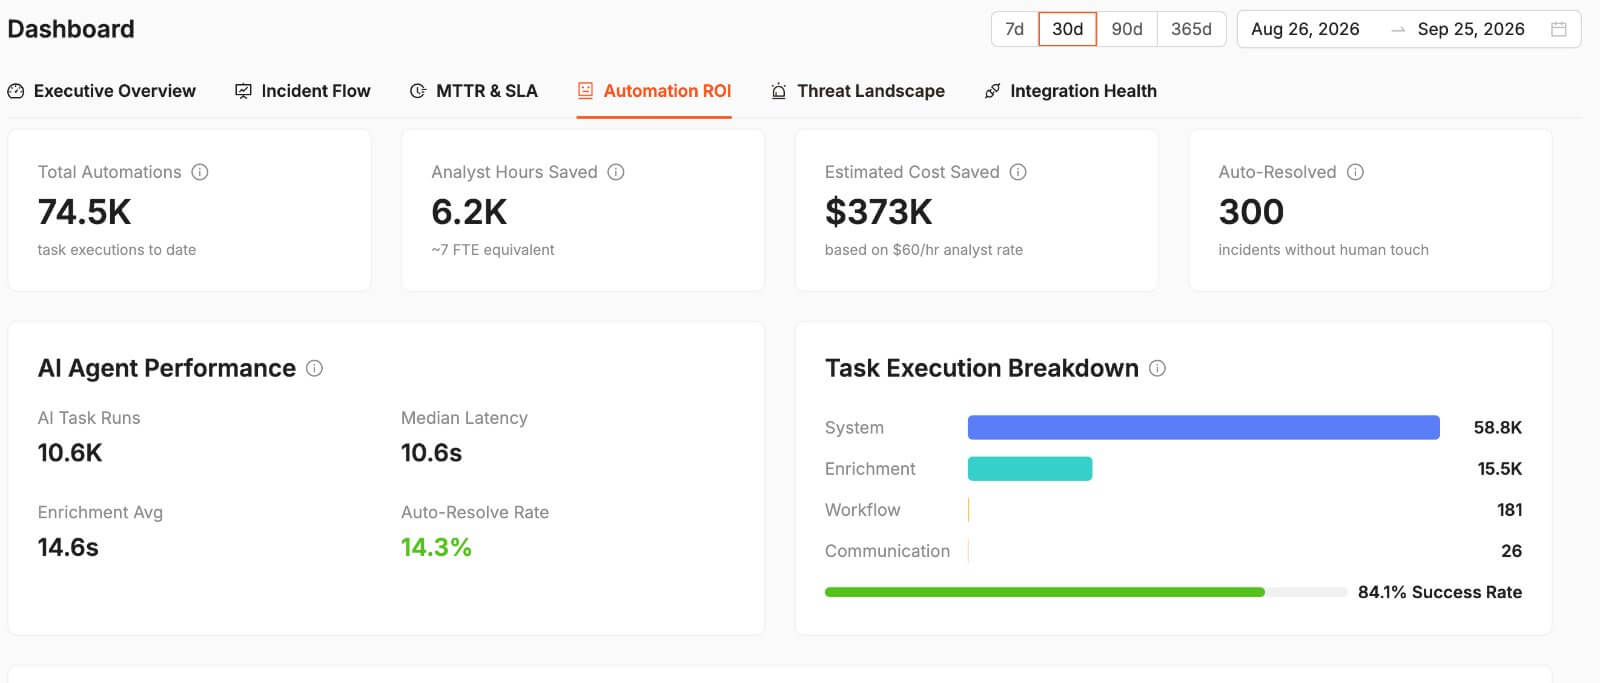
Your client sees your value — in hours and dollars
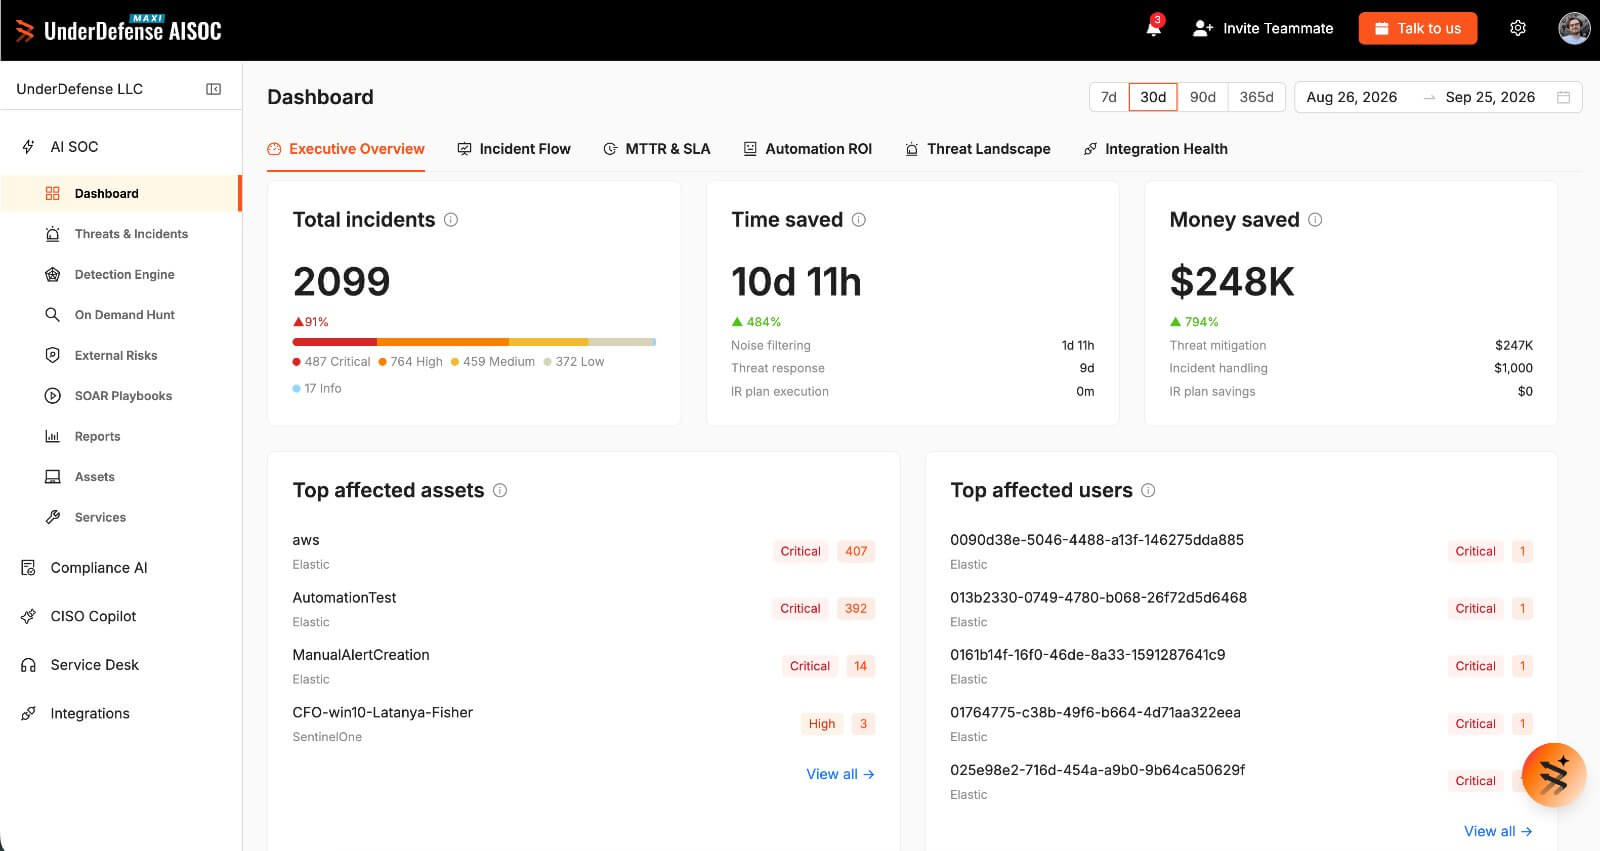
Their own dashboard shows every incident you handled, the time your team saved them and what it is worth — for any period.
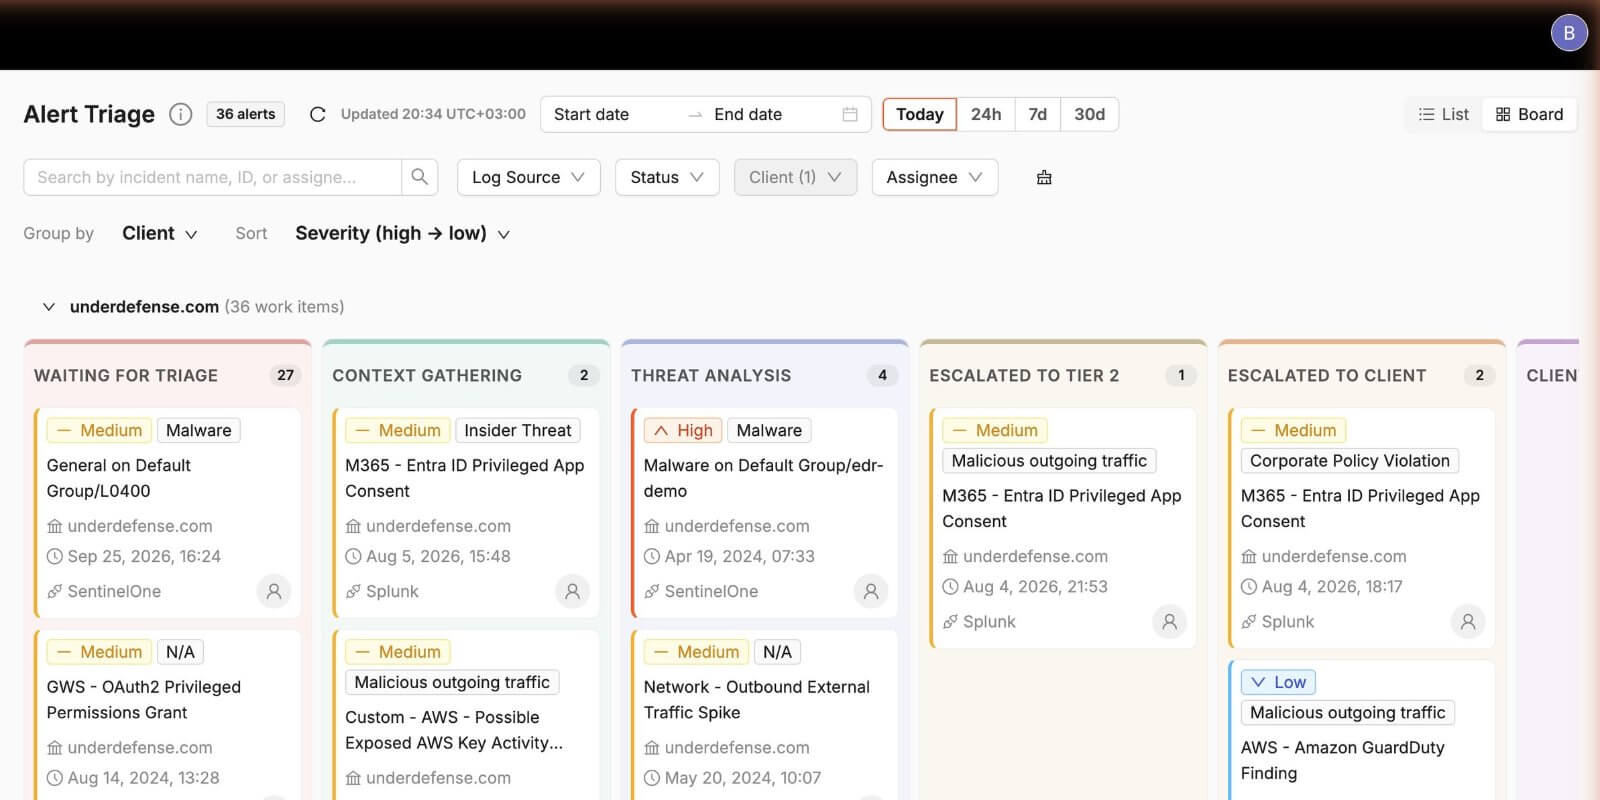
One queue for every client — the most critical alert first
Analysts hop between consoles while the critical alert at client #7 waits.
One Kanban across every tenant — sort by severity, group by client, drop into context.
Group the queue your way — by client, severity, source or analyst.
Waiting → Context → Analysis → Tier 2 → Client → Replied · T1 → T2 review & exclusions · Group by client · source · analyst
AI does Tier 1 — your analysts sign off
Your clients' data is never used to train AI modelsA thorough manual investigation takes ~75 minutes per Analyst — and most of the queue is noise.
Every alert from every client is enriched, investigated by the AI agent and handed to your analyst as a case with a verdict.
Minutes per case instead of an hour per alert — one analyst covers more clients.
with
evidence
Plug into the stack they already run
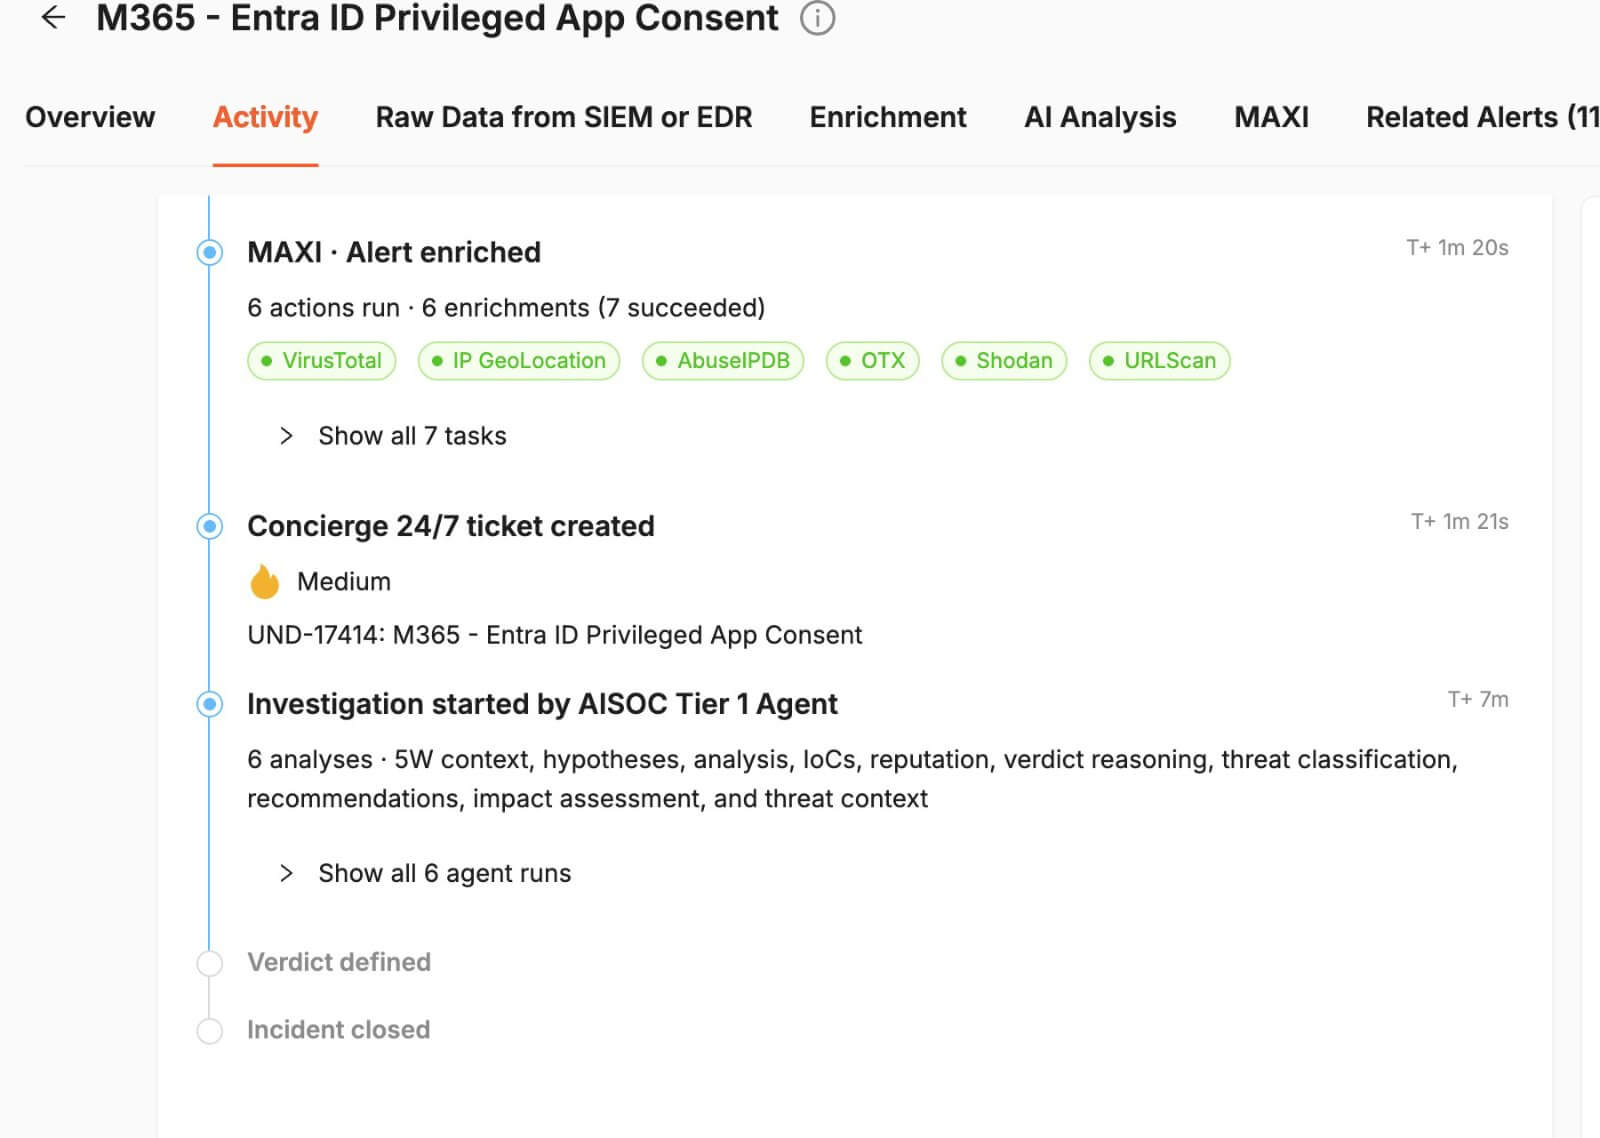
Every client runs a different stack — ripping it out kills the deal.
119 integrations, each with a step-by-step guide the client's IT can follow — read-only API keys, nothing to install.
No migration, no new agents — data flows on day one.
119 integrations in 24 categories · 8 with MCP — AI queries SIEM/EDR live · No vendor lock-in — works with the tools they own
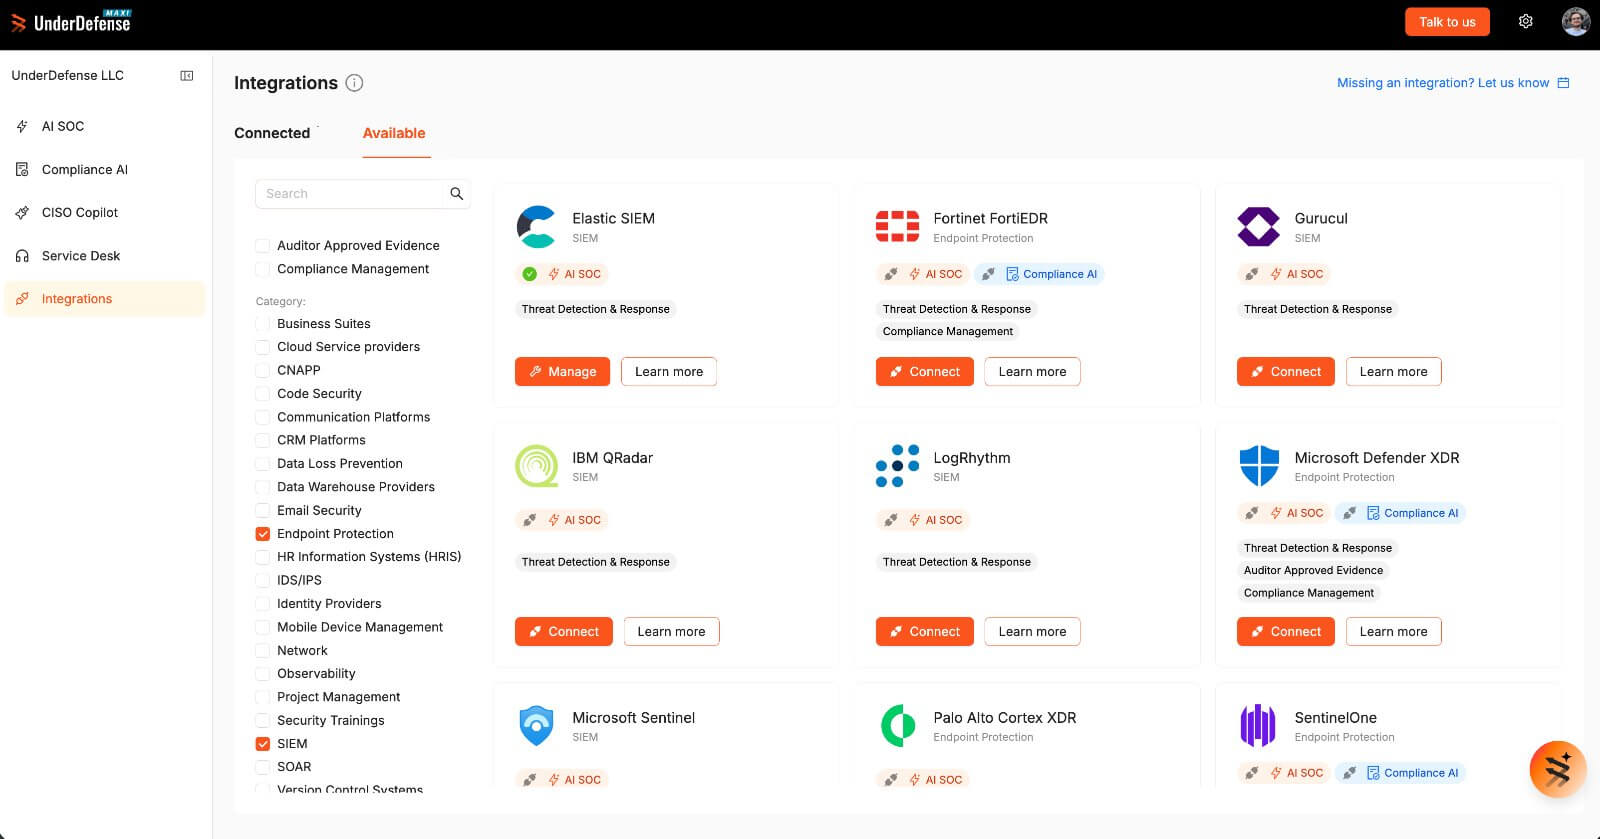
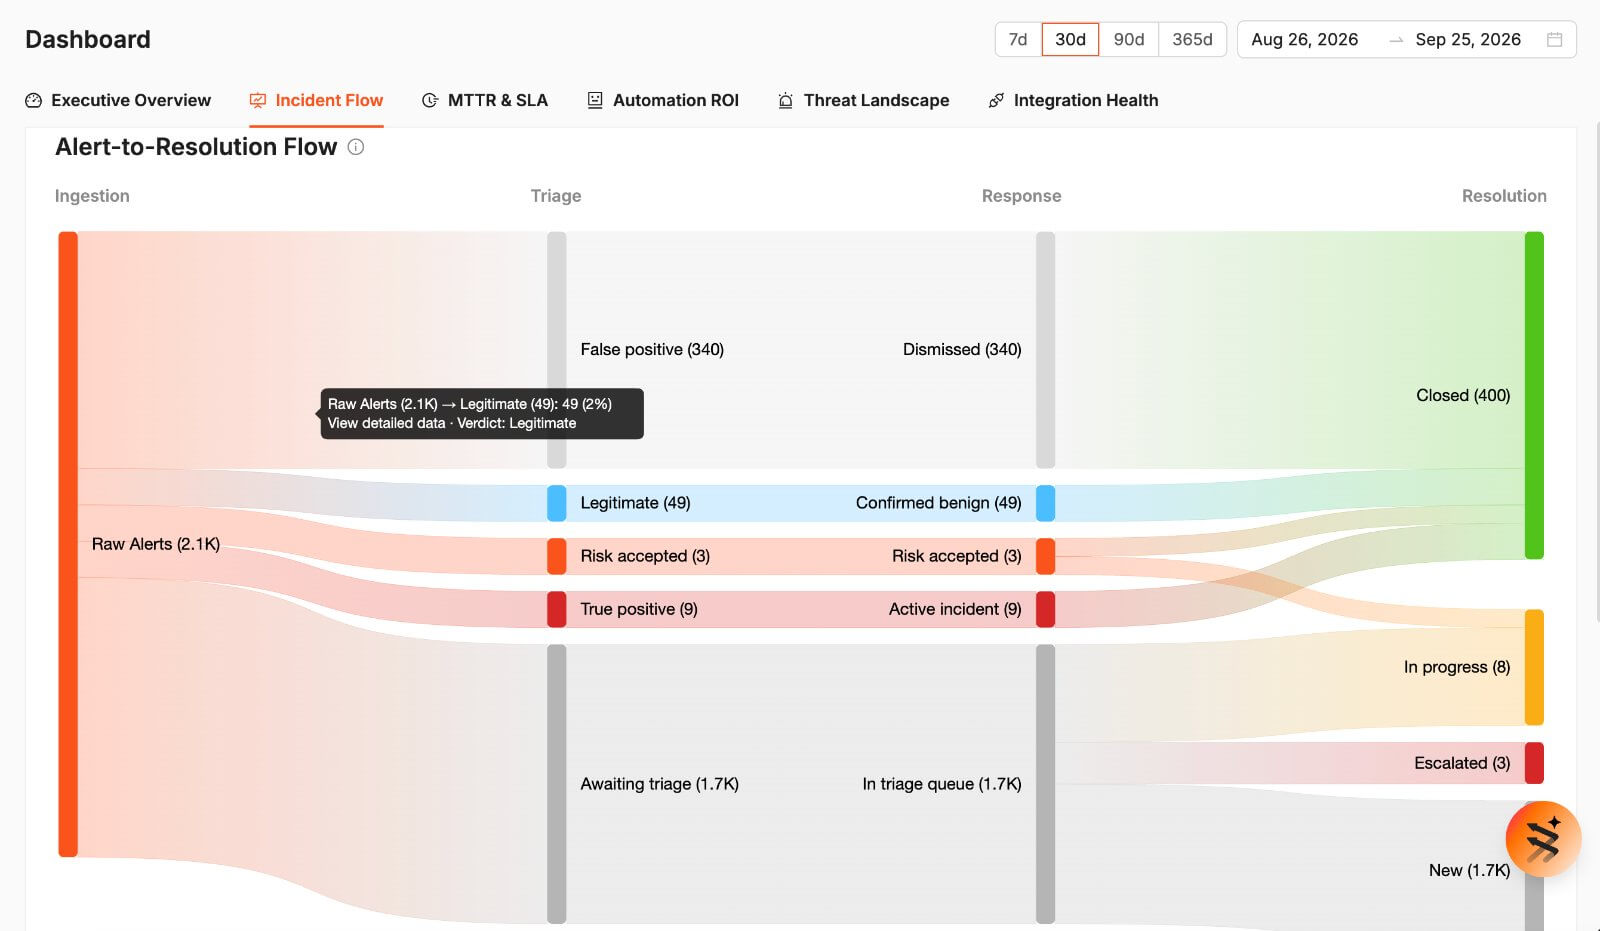
Every incident, every step of the investigation
The client sees the whole volume of your work: each incident, its timings, the verdict reasoning and every AI and analyst step behind it.
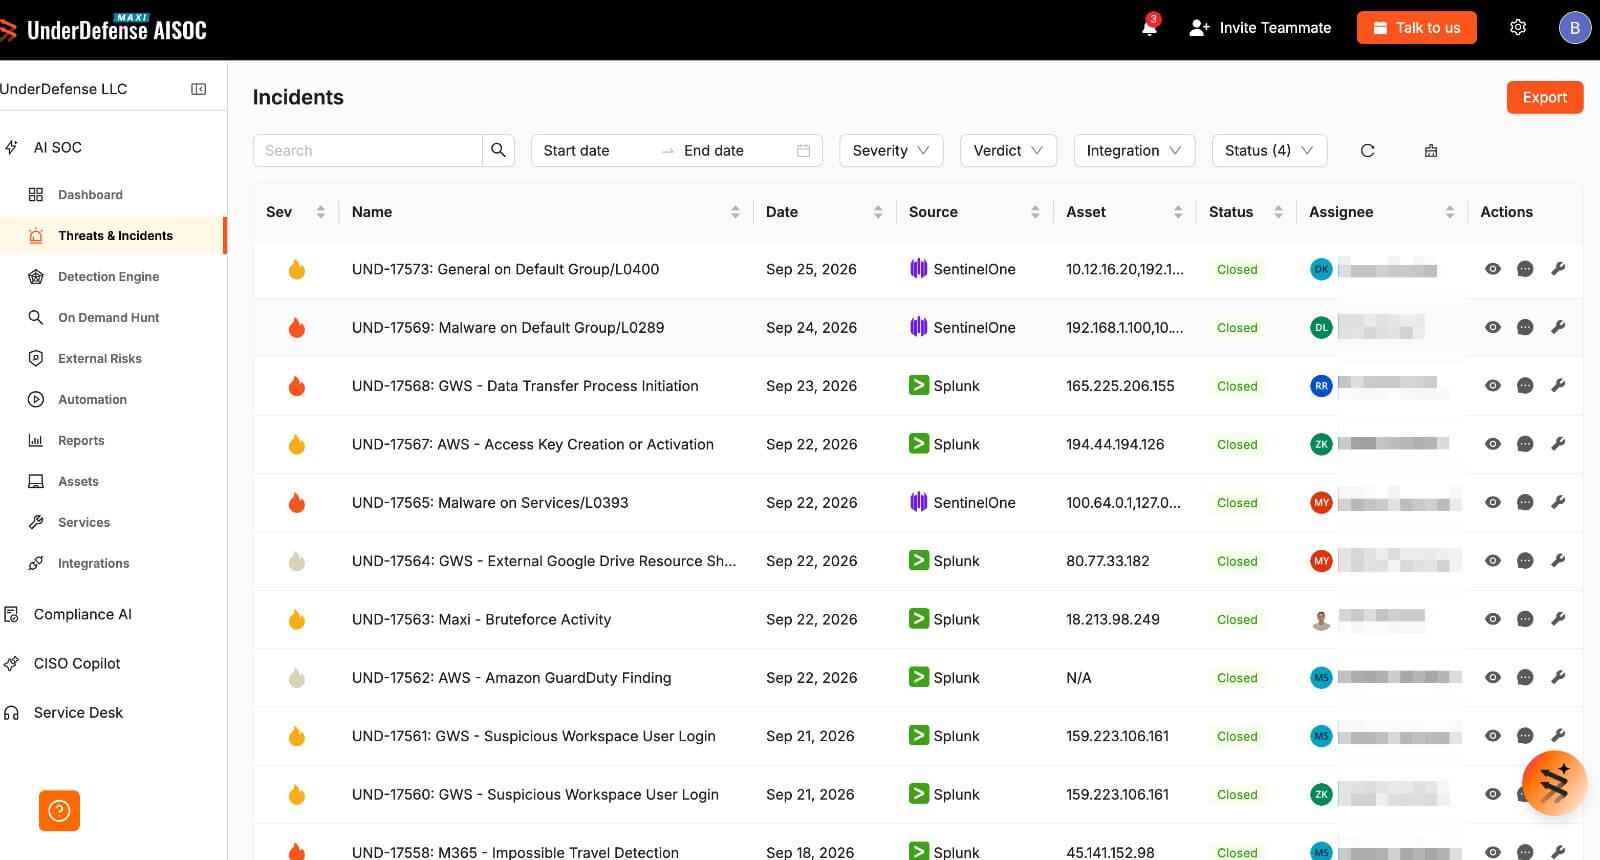
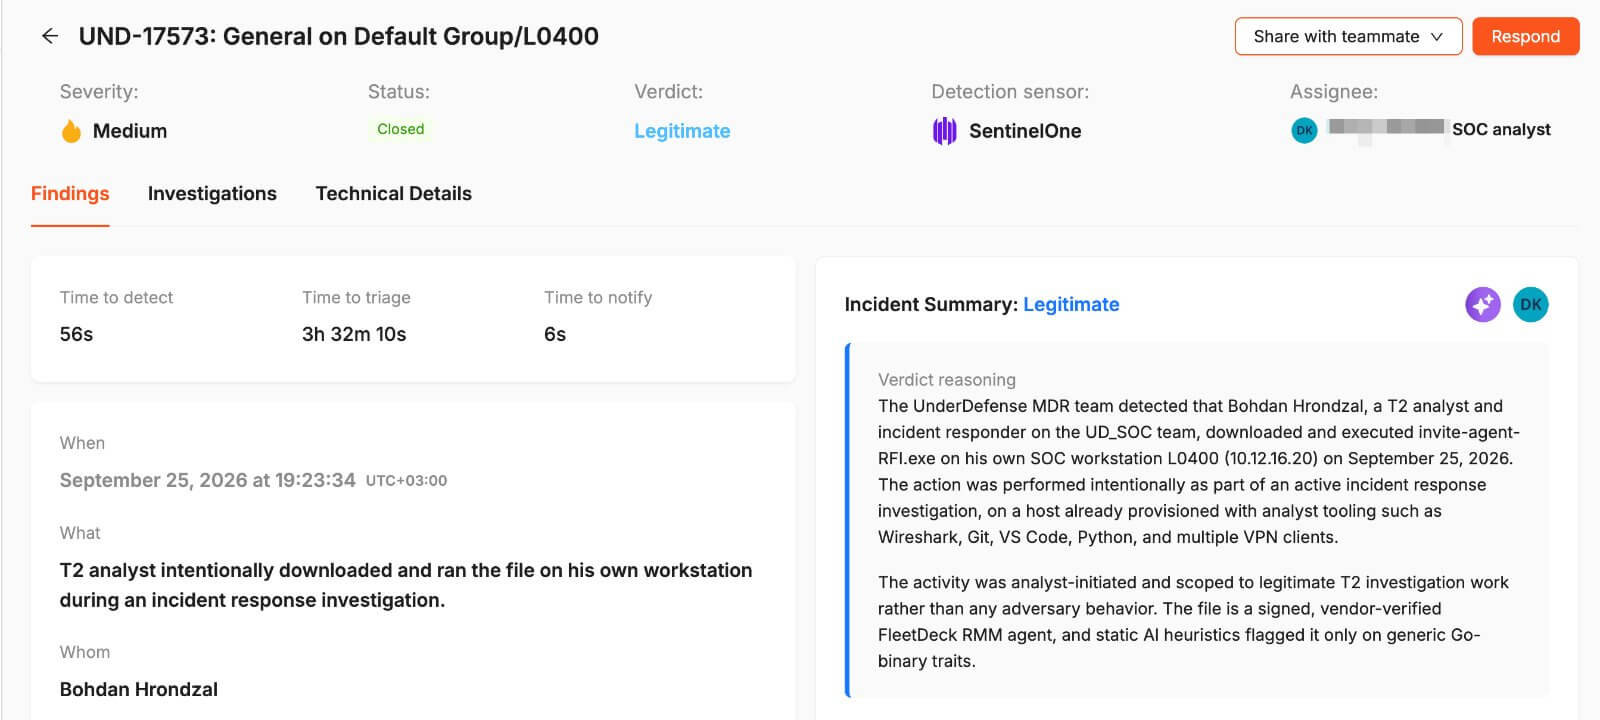
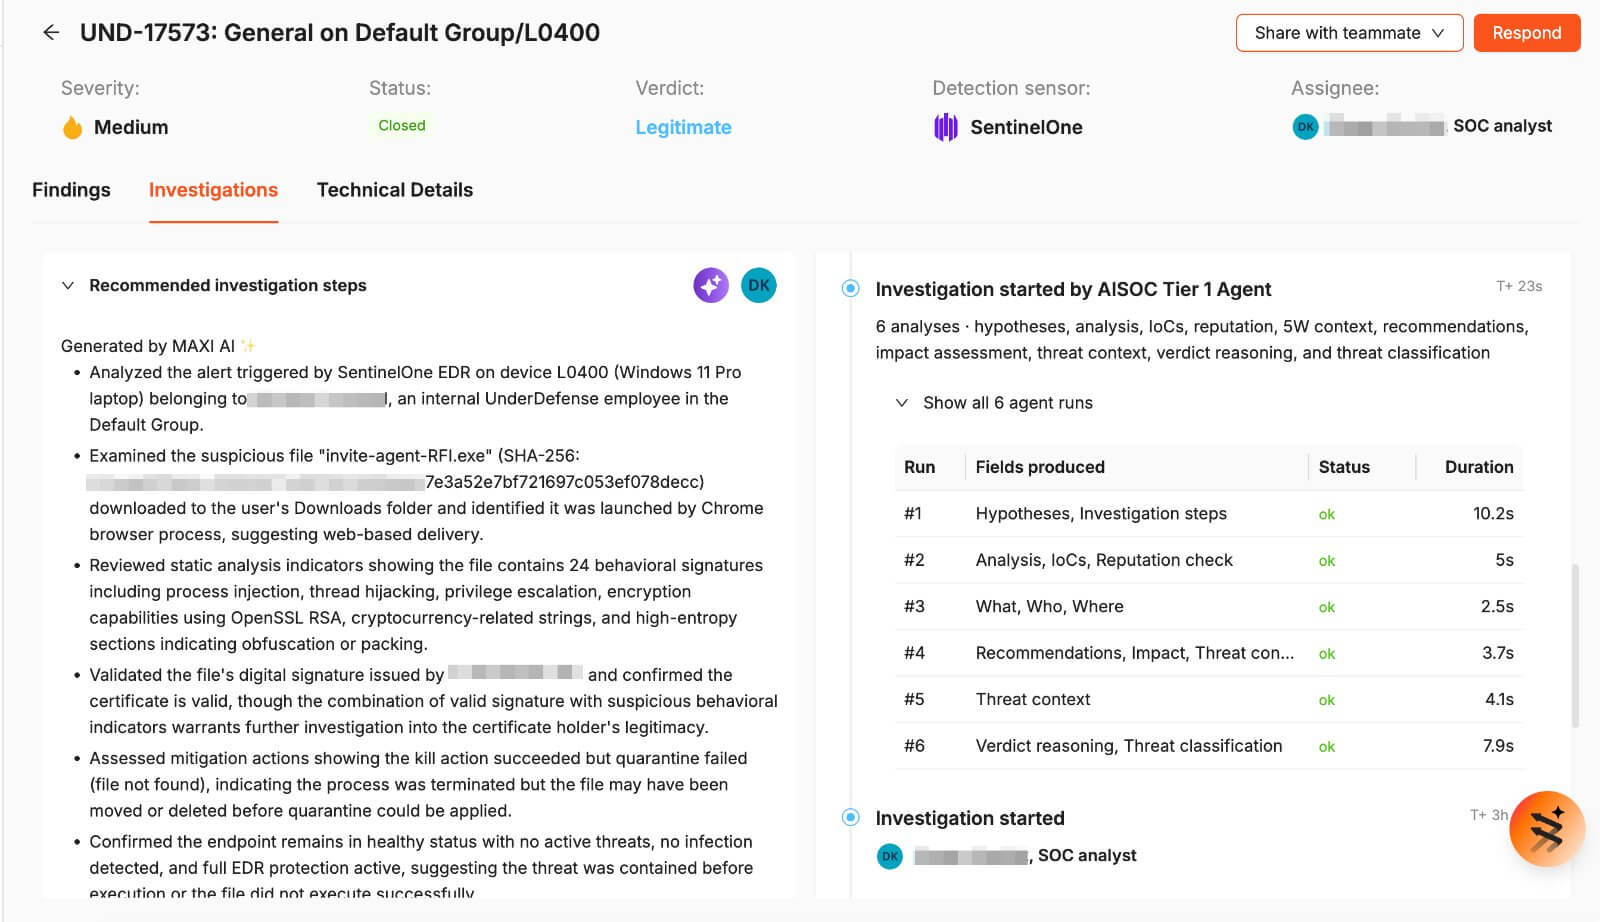
AI agents do the legwork — your analyst makes the call
Your clients' data is never used to train AI modelsEvery IoC checked against eight intel sources in parallel — reputation, geo, history
Weak signals across endpoint, identity and cloud assembled into one chain
Findings written up as 4Ws: who, what, when, where — with the evidence
Verdict hypotheses with reasoning, impact and a reversible containment plan
A billion events a week — only 10 incidents that matter
Real-time correlation against IoCs across the whole stack
AI and analysts research, correlate and build the blast radius
Confirmed, contained and handed over with next steps
alert noise reduction
alert triage · 10 min enrichment
to identify an intrusion — industry average is 206 days
MITRE ATT&CK coverage
A platform your SLA can stand on
Isolated tenant per client
Every client’s data, users and AI context stay in their own tenant
Hosted anywhere
Wherever your clients' data needs to live — deployed in the region their regulator expects
Certified ourselves
UnderDefense is SOC 2 and ISO 27001 certified — on our own platform
No training on client data
Your clients’ data is never used to train AI models
Every AI step on record
Each enrichment, query and verdict is logged — a full audit trail
We depend on it too
Our own 24/7 SOC runs on MAXI — its uptime is our SLA as well
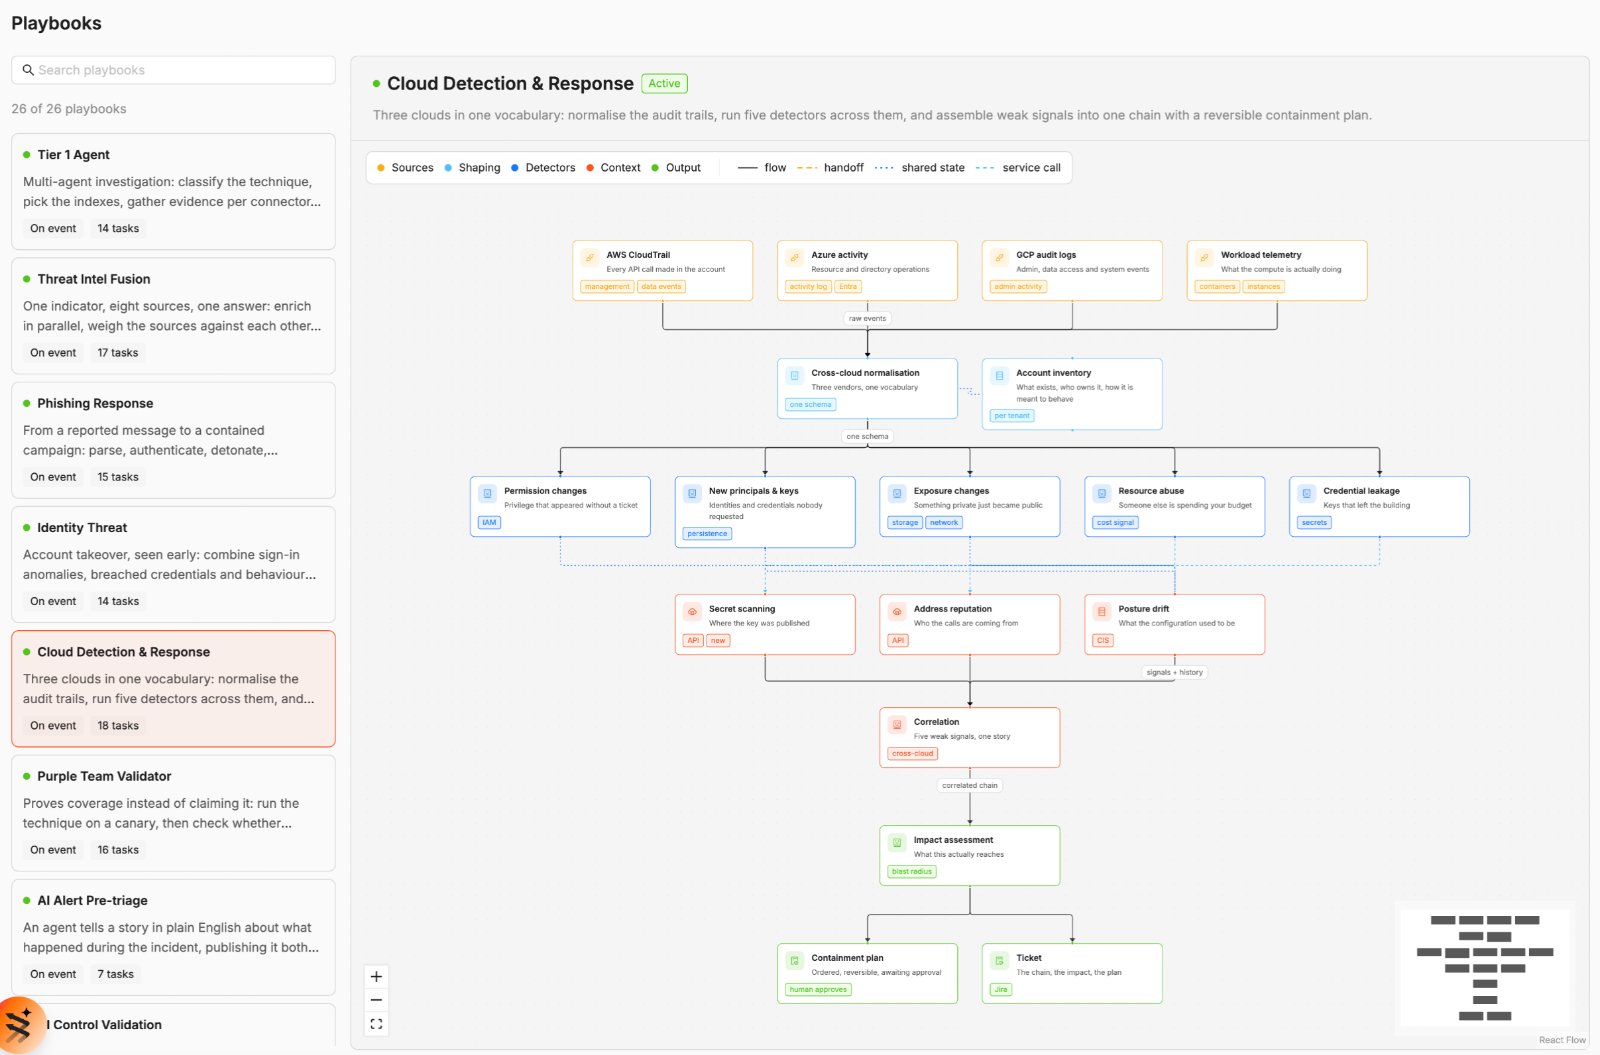
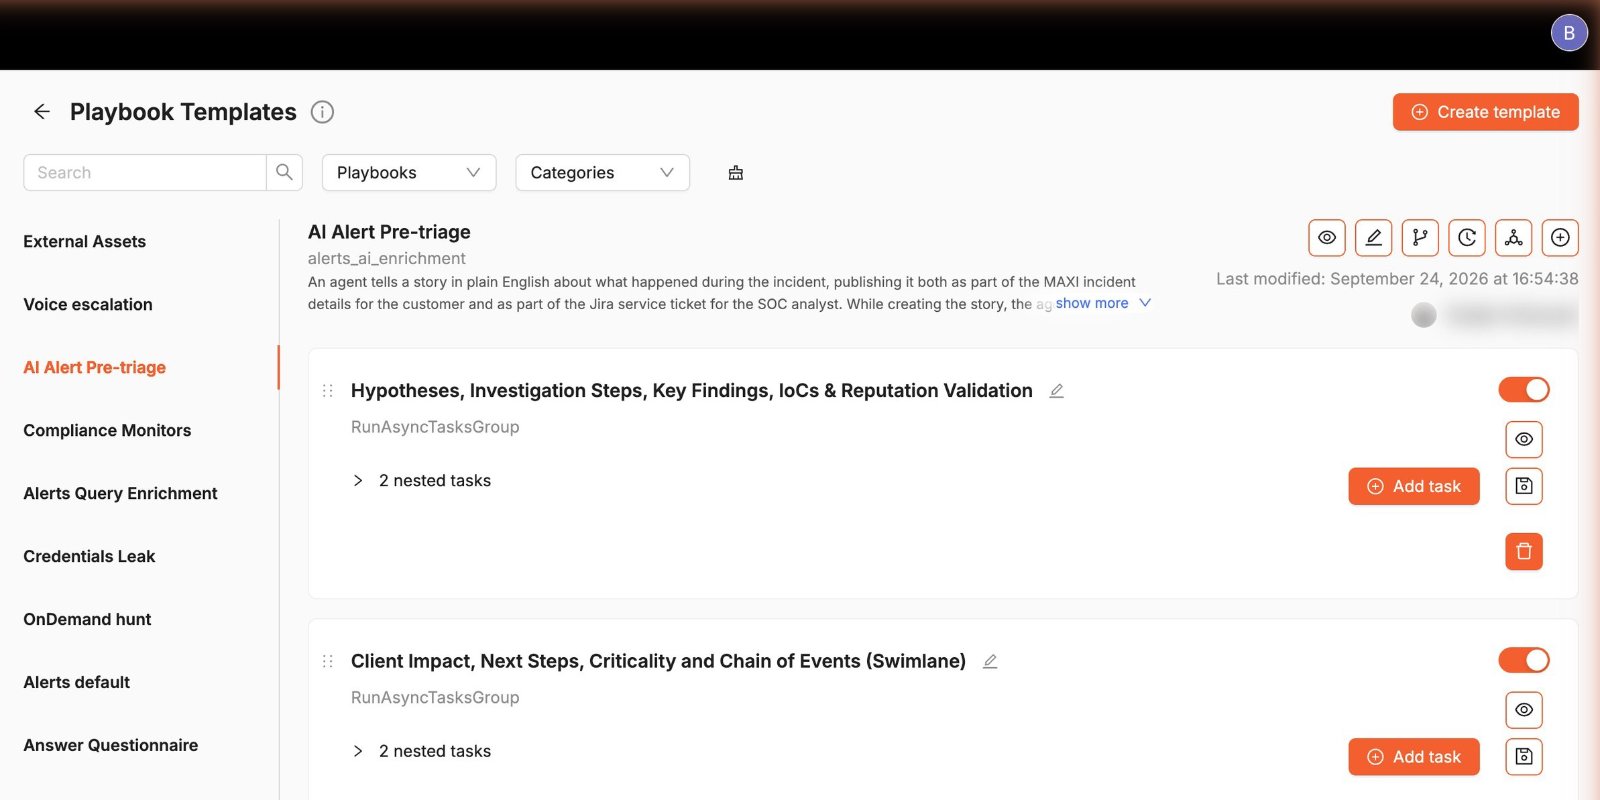
Your playbooks become your Intellectual Property
Every customer is unique. We give that flexibility to adjust Detections and Response with Playbooks
How things are processed to make it work for your customer - is defined by You with our AI. Unique 26 versioned templates, rolled out to many clients, tuned per client.
Bulk upgrade in safe mode · Sandbox on a real alert · AI prompts per client · Grouping policies
One click, and MAXI calls the client
At 3 a.m. an analyst dials contact after contact from a spreadsheet — and nobody logs who answered.
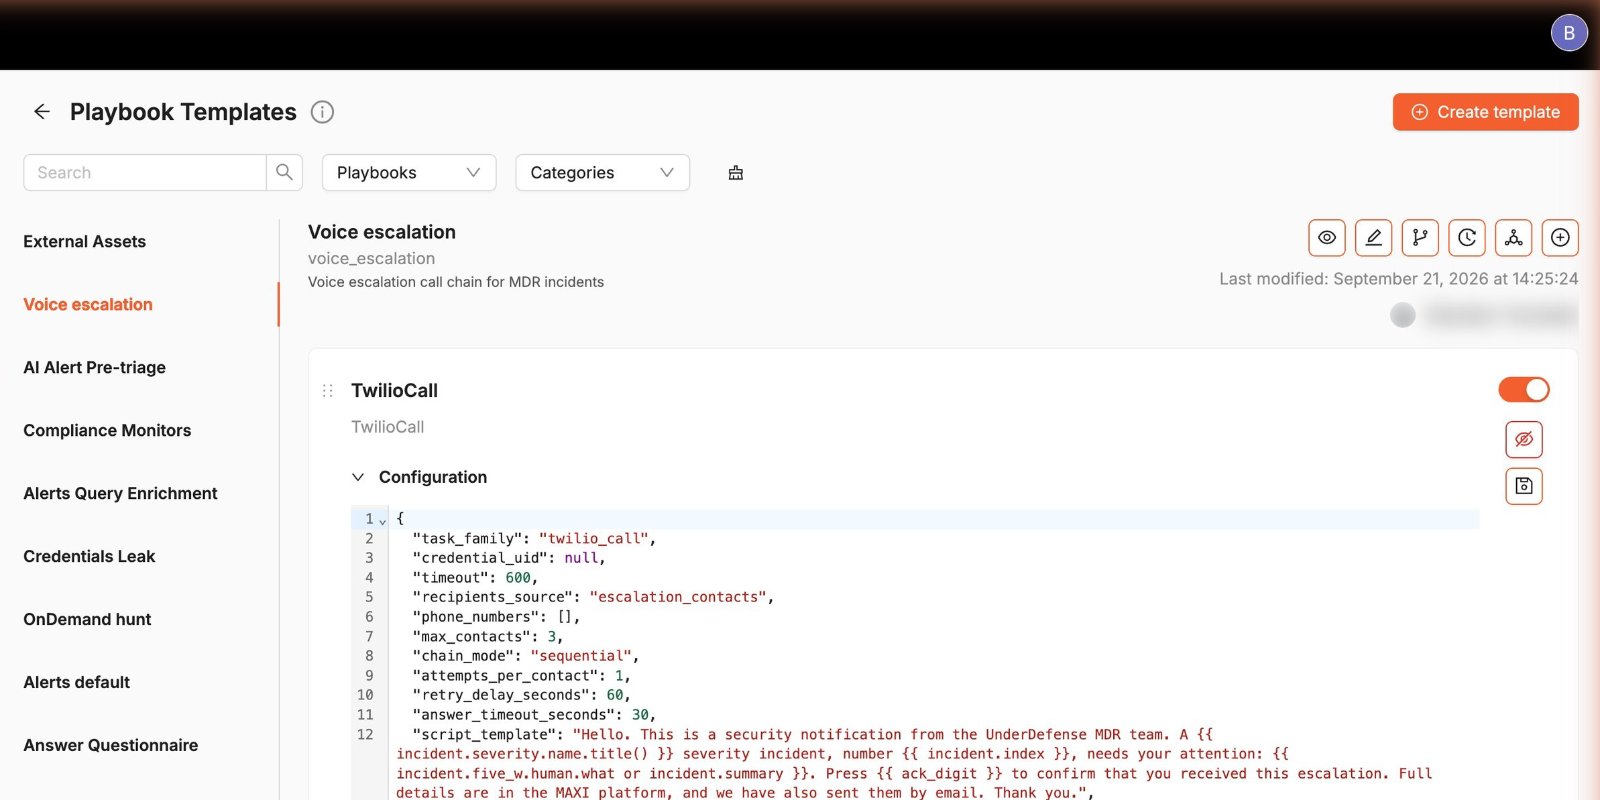
The right person hears it first — a human always makes the call
3 a.m., critical incident: the analyst hunts for a phone number.
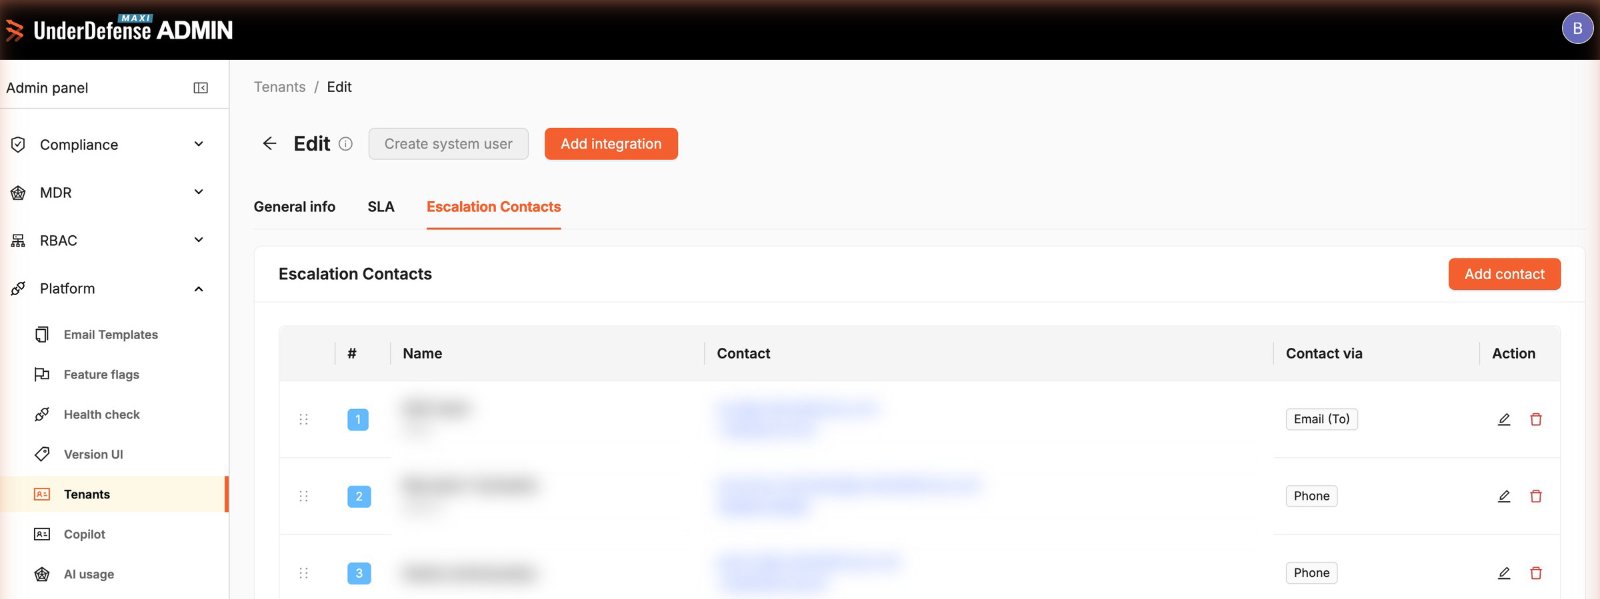
An ordered escalation chain per client: who is called first, over which channel, and what each contact opts out of.
Clients hear exactly what they need, when they need it.
30 notification types · Per-contact opt-out · Email · Jira · PagerDuty · Auto-close when the client stays silent · Great defaults — you override every one
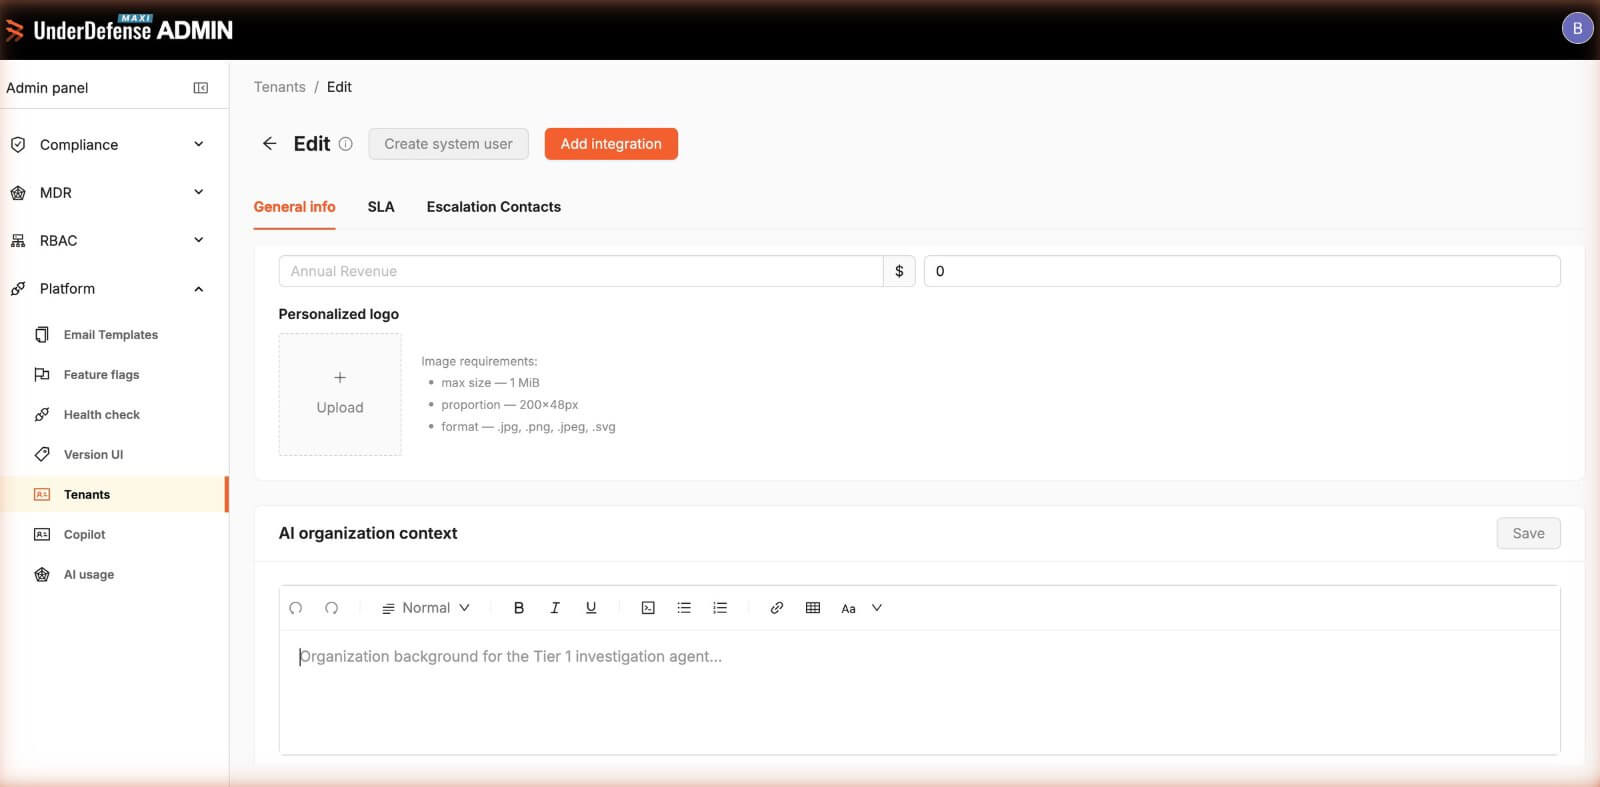
Tell the AI who your client is — once
Analysts investigate blind: they don't know the client's business or what normal looks like there.
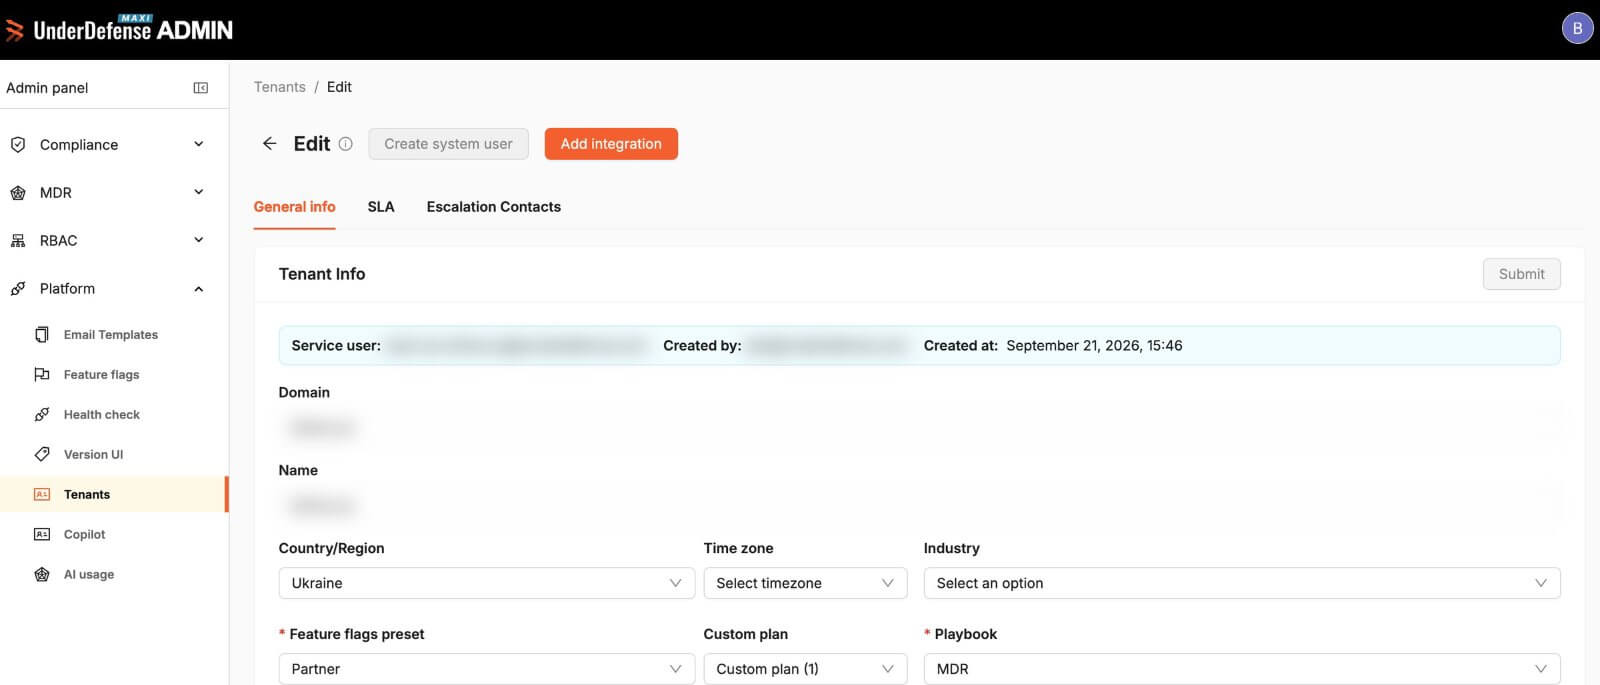
Launch a new client in one sitting
A new client means spreadsheets and shared logins
One tenant card — plus a login for the client
Your value is visible from day one
Every alert · case history · MTTD
Broken connectors surface before the client notices
A connector breaks silently — and the client finds the gap before you do.
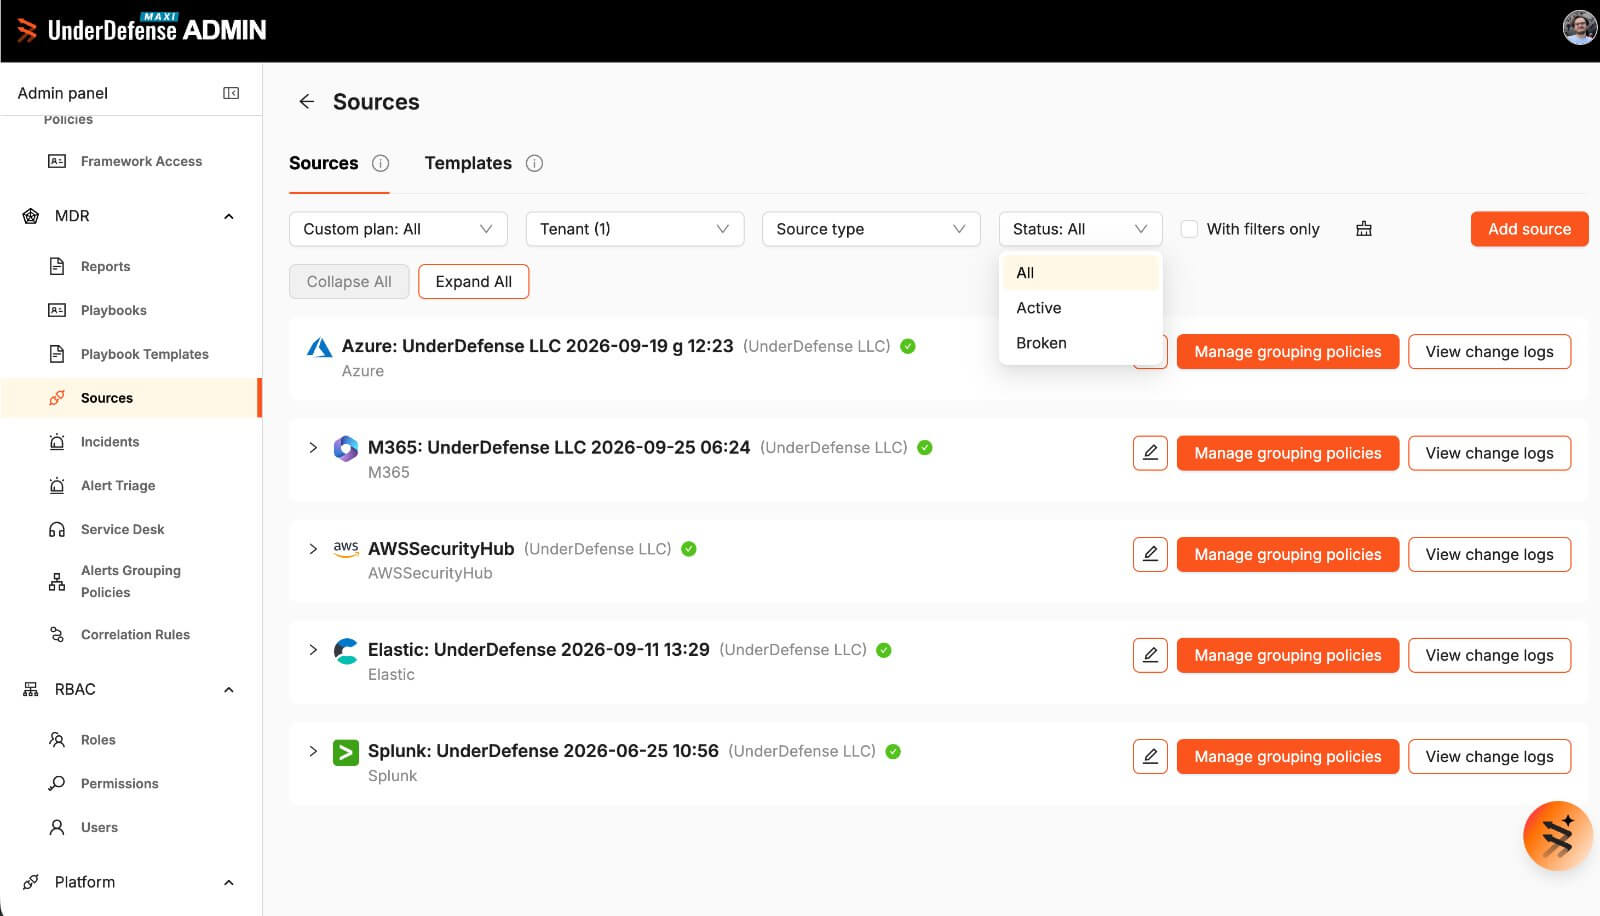
A view for SOC managers, a view for analysts
Managers need the overview, analysts need the workflow — one screen rarely gives both.
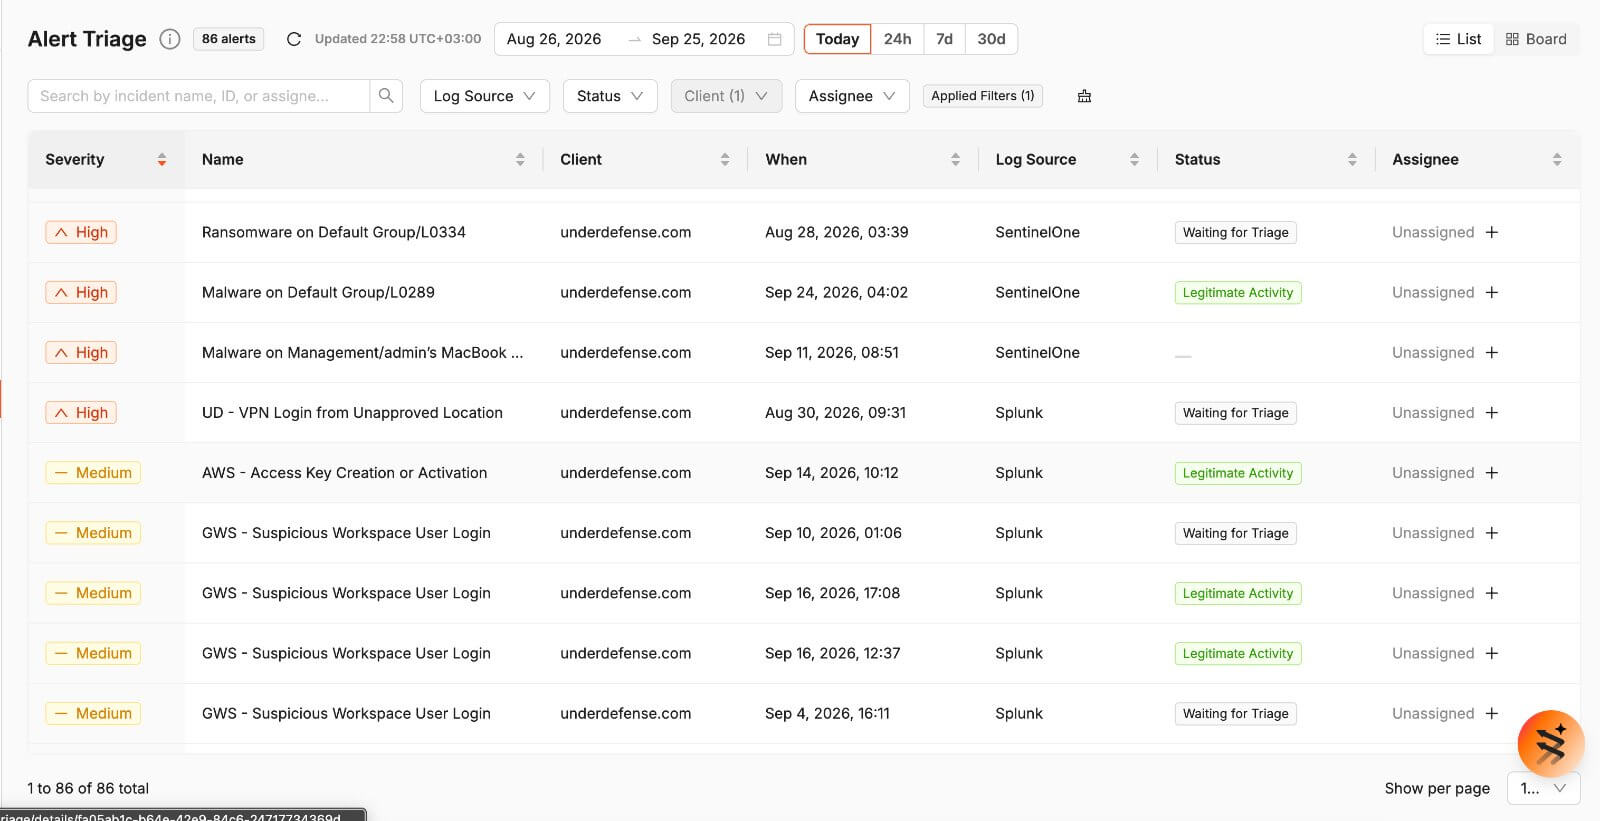
A case with evidence, not a raw alert
Your clients' data is never used to train AI modelsAnalysts get a raw alert and spend the first hour just collecting context.
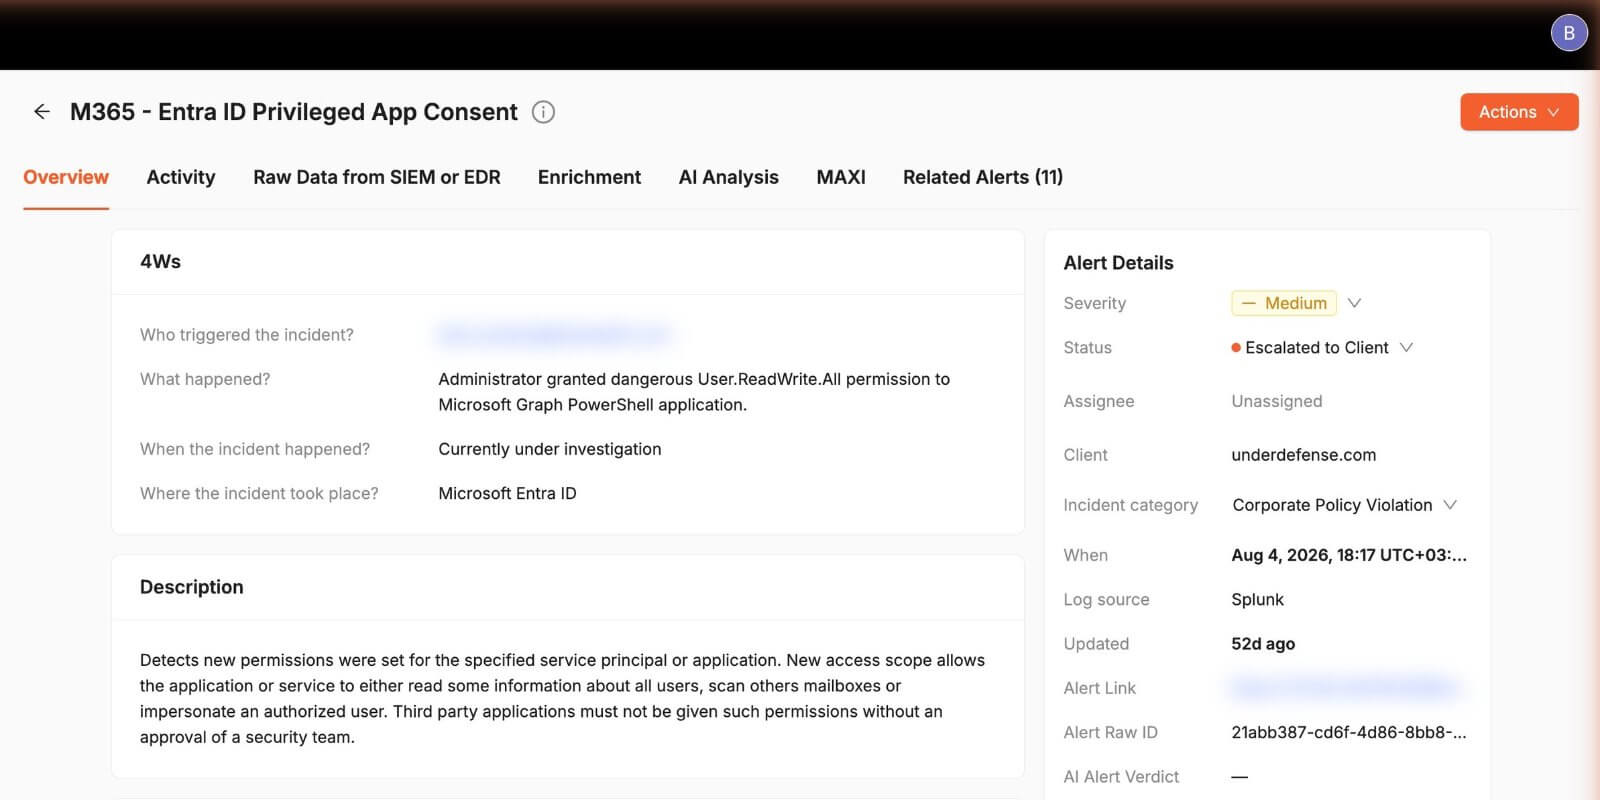
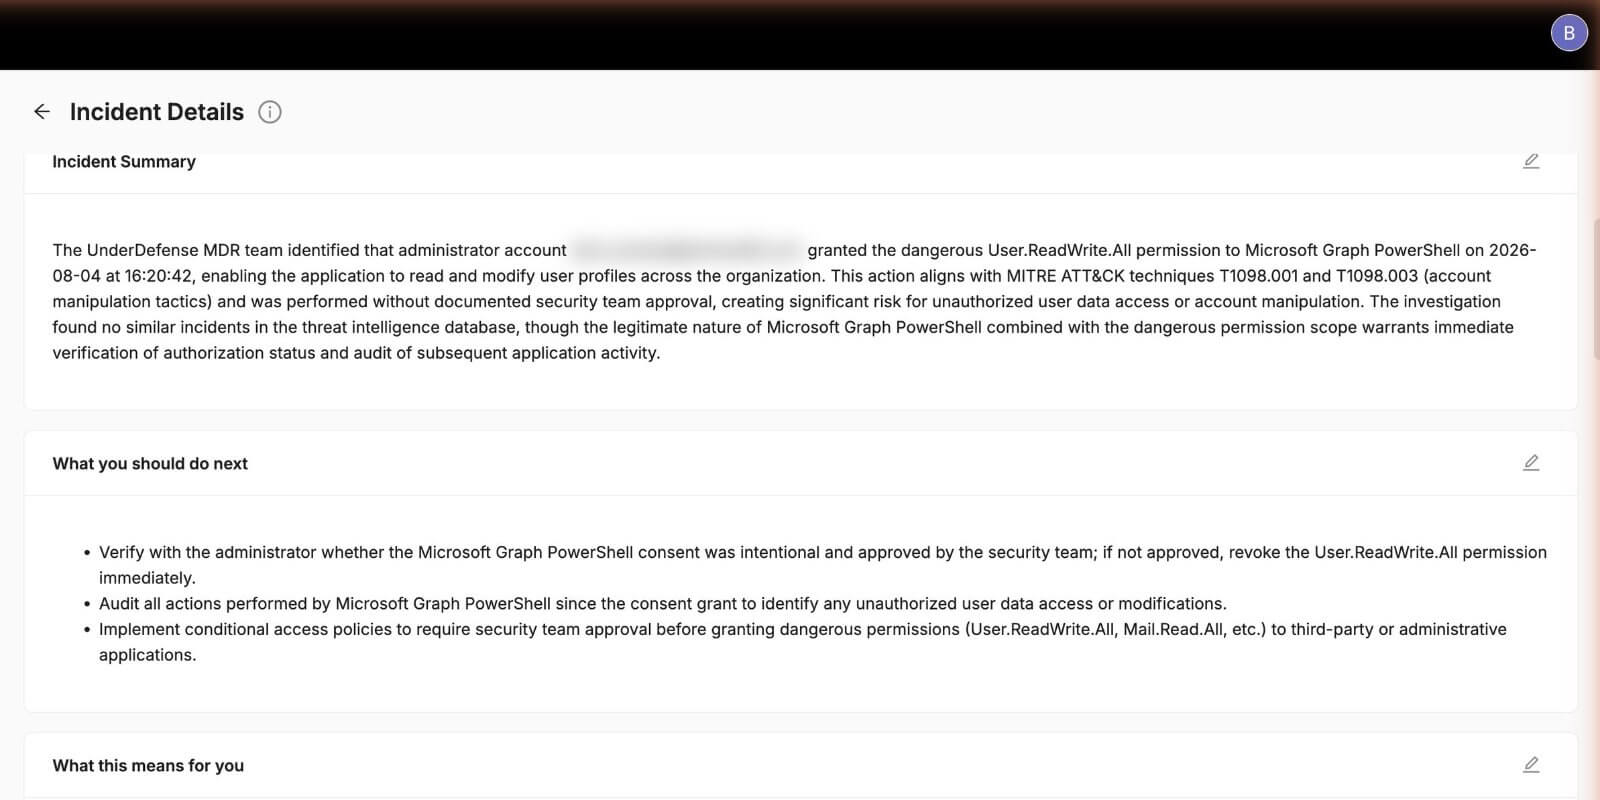
An incident your client actually understands
Clients get raw SIEM dumps they can't act on.
Every incident reads like a briefing — what happened, what it means, what to do next.
Clients act in minutes instead of calling your SOC for a translation.
When · What · Who · Where · What this means for you · What you should do next · IoCs & reputation
Every QBR proves your value — in one click
Reports stitched by hand from five tools make thin QBRs.
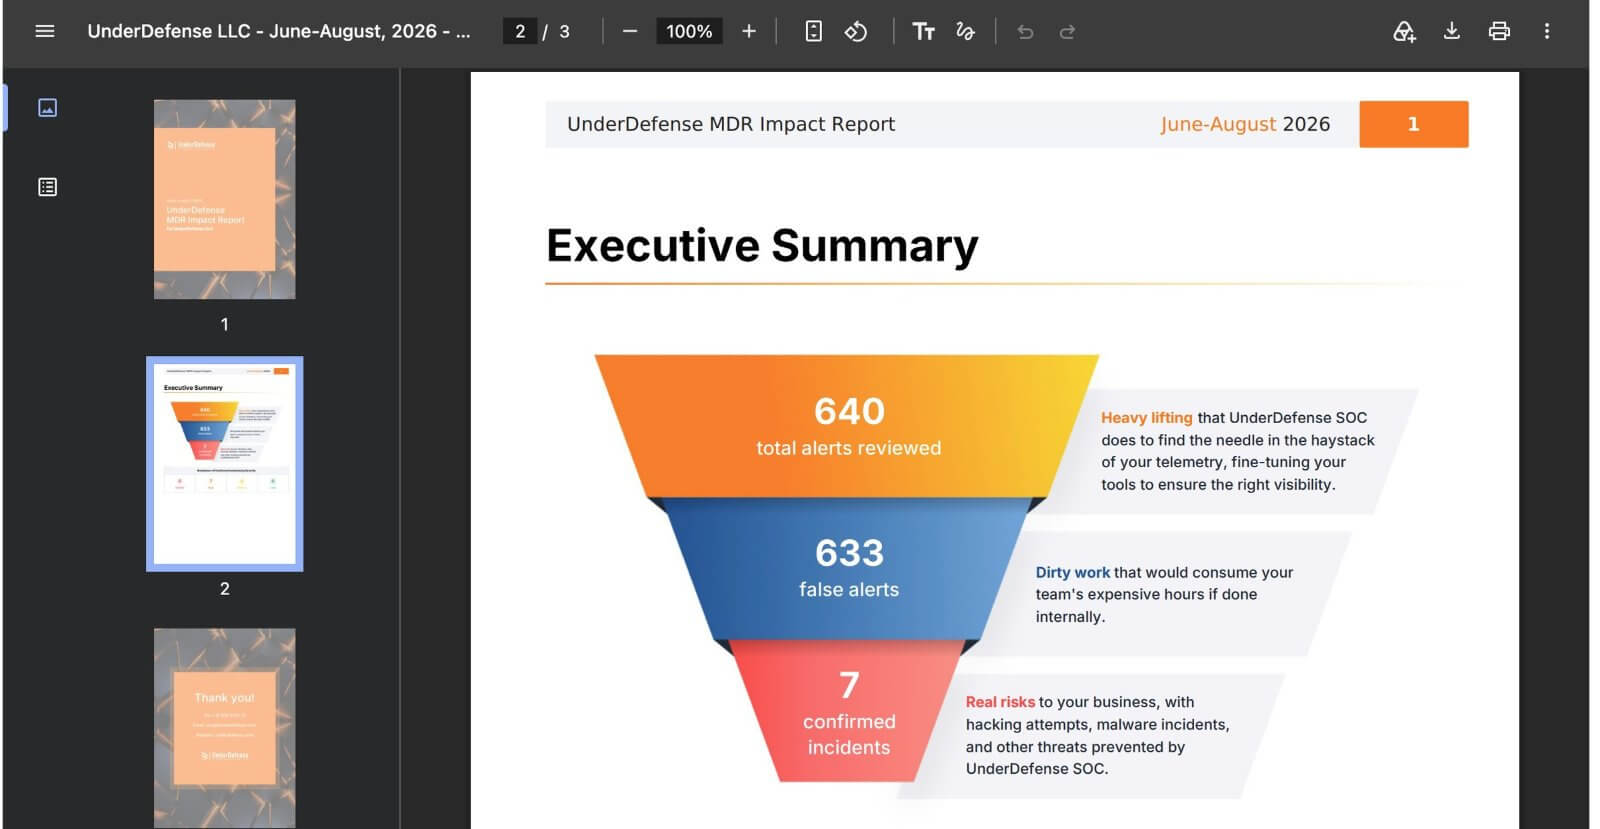
The monthly MDR report in one click — 17 sections, built from data the platform already has.
The SLA you kept and the threats you stopped — the proof that drives renewal.
640 alerts reviewed → 633 false → 7 confirmed · Response times vs SLA · Night-shift coverage · Top detections
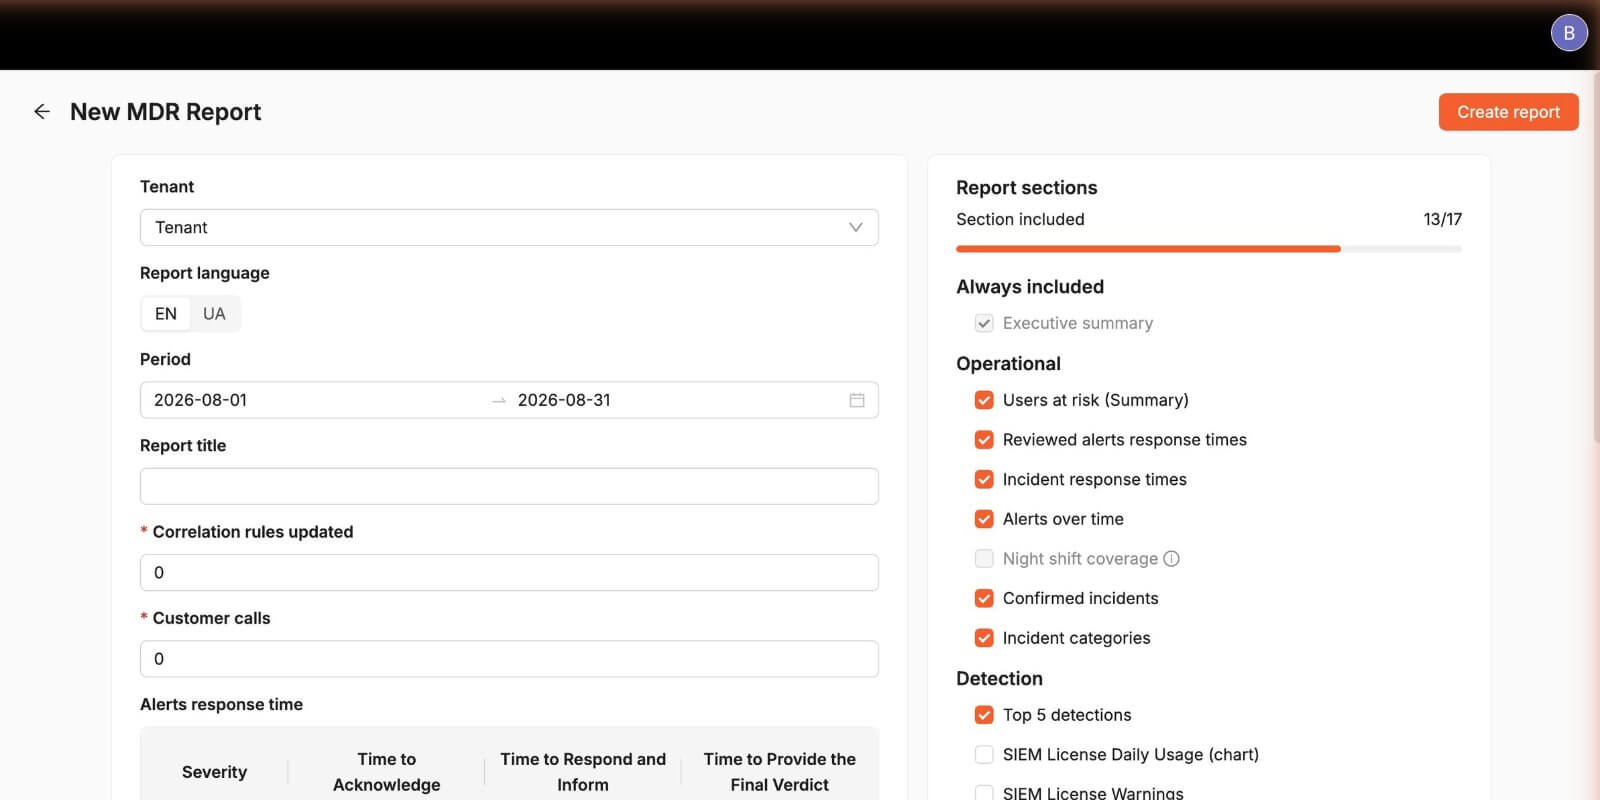
Pick the sections, MAXI writes the report
Monthly reports are assembled by hand from exports and screenshots — for every client.
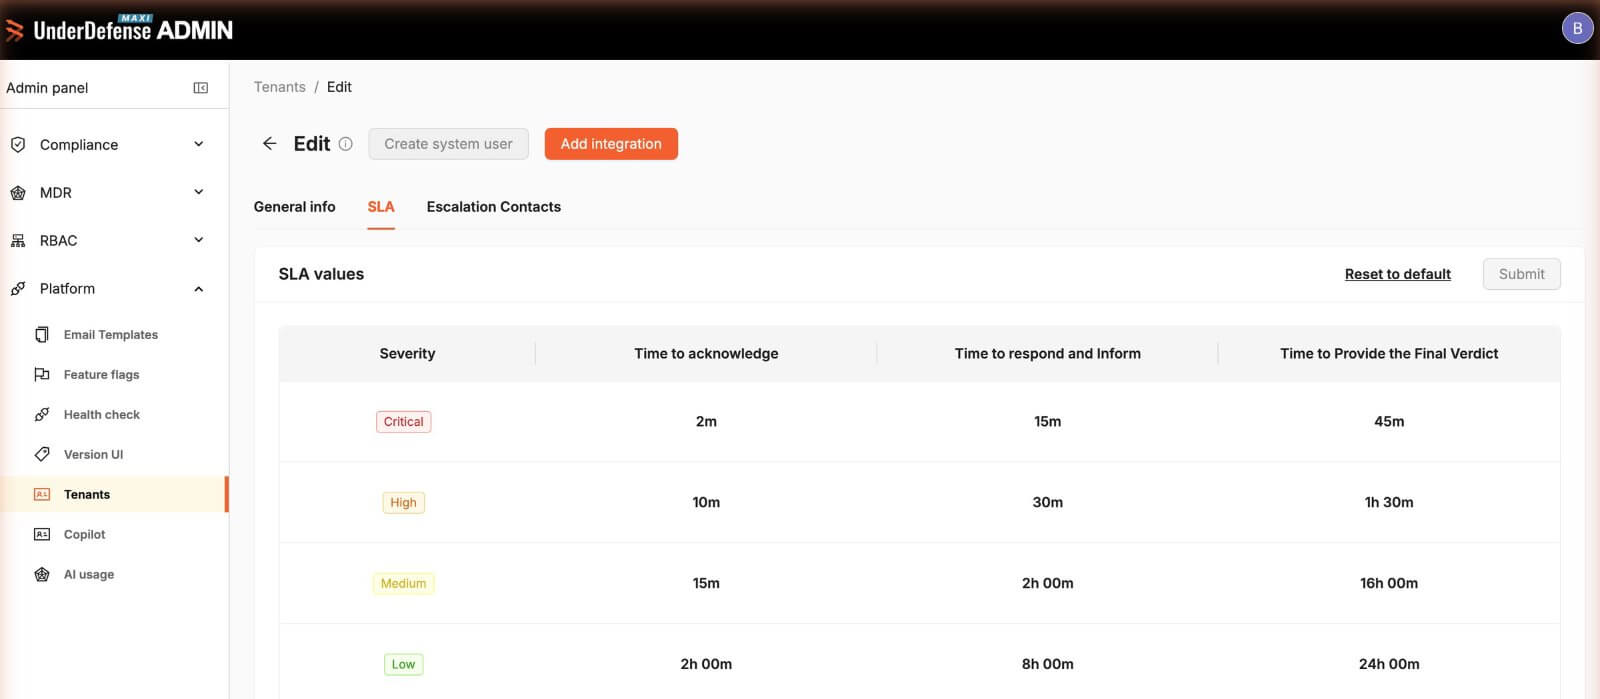
An SLA clock for every client
Every contract has different SLA terms, tracked in someone's head or a spreadsheet.
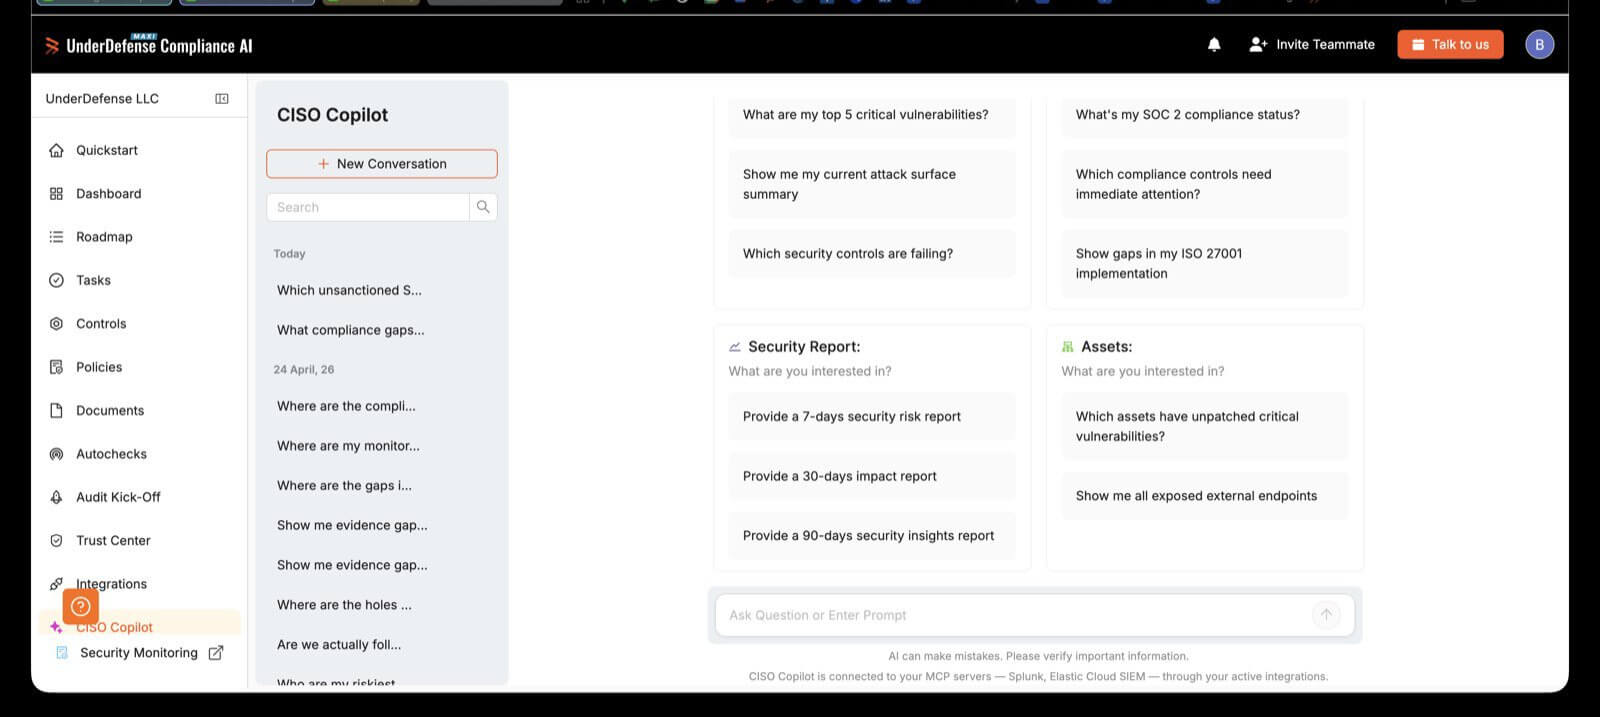
Find answers — SUPER FAST, in plain language with COPILOT
A client's question turns into hours of queries across Splunk, Sentinel and Defender.
Unlock new revenue streams for your MSP/MSSP
Add managed infrastructure and security services to your portfolio without building them from scratch. Bundle with your existing offerings, increase client lifetime value, and multiply your per-client margins.
- Generate recurring revenue from every client with bundled services
- Compete with larger players—offer enterprise-grade managed security at any scale
- Onboarding in 2–3 weeks—sell faster, implement sooner
More to sell on the tenant you already run
Every client you monitor is a ready-made opportunity for the next service — no new platform, no new onboarding.
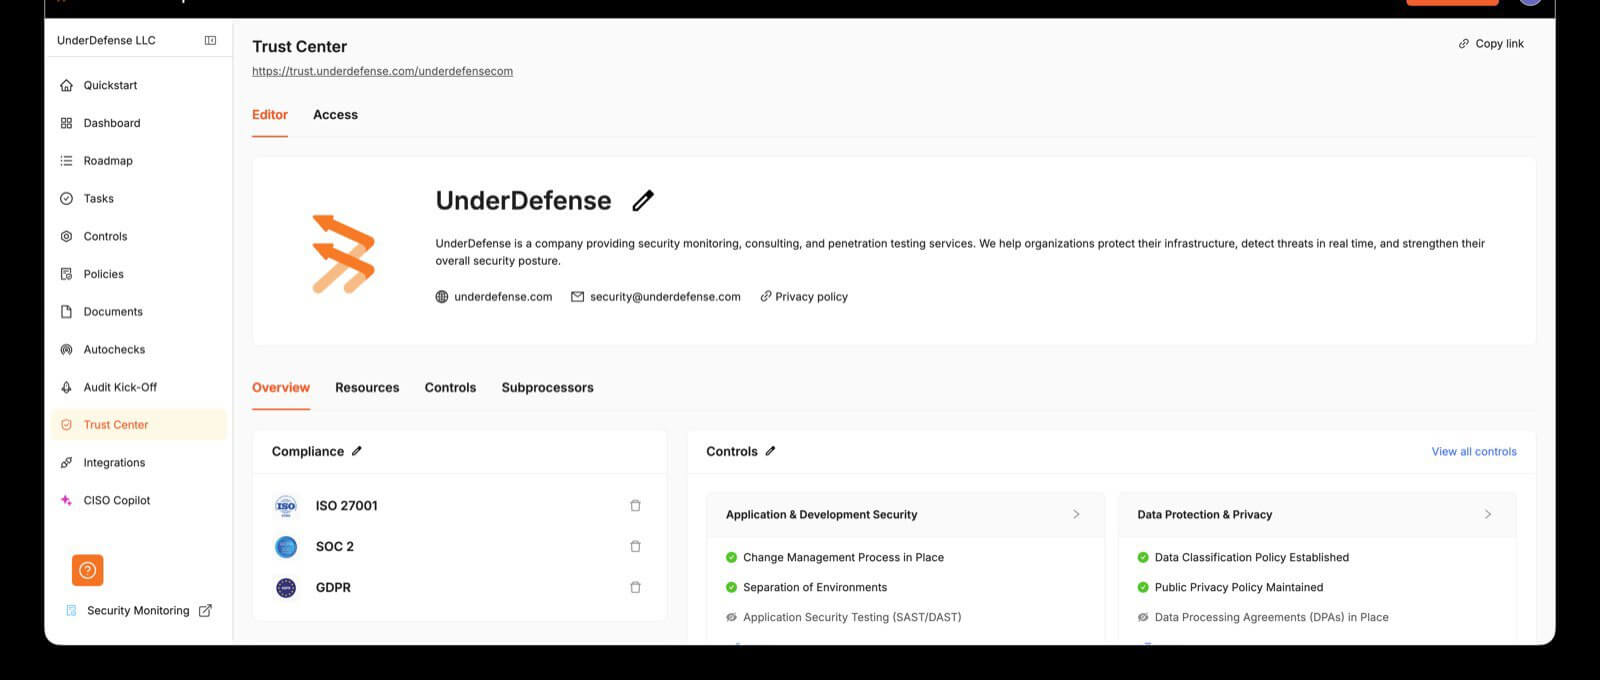
Compliance
Turnkey programs per client — only the frameworks they need, Trust Center included.
Readiness per framework · autochecks · auditor access
External risks
Attack surface, leaked credentials and exposed services monitored continuously.
Subdomains · open ports · TLS · credential leaks
Assessments & pentest
Cloud CIS benchmarks, vulnerability scans and pentest reports in the client's workspace.
AWS · Azure · GCP · Kubernetes CIS · pentest
vCISO with Copilot
Board-ready answers and reports on demand for clients without a security leader.
Board summary · risk report · compliance gap
Sell in tiers from day one — upgrade a client with one switch
A starting blueprint for your own price list — rename, reprice and regroup as you like. Each tier is a preset on the client’s tenant.
Standard
Confident protection 24/7/365
- Endpoint detection & response 24/7
- Dark web exposure & leaked passwords
- Direct chat with on-duty analysts
- Monthly reports & remediation guidance
Enhanced
Extends to cloud, SaaS and email
- Everything in Standard
- Cloud, SaaS & email detection & response
- External attack surface & threat intelligence
- Vulnerability assessment · IR retainer
Professional
360° protection and full visibility
- Everything in Enhanced
- Managed SIEM & XDR
- Advanced threat hunting & automated response
- Compliance reporting · tool fine-tuning
Turnkey compliance — only the frameworks each client needs
Every client needs a different framework — spreadsheets don't scale past three.
Switch frameworks on per client: NIS 2 + ISO 27001, SOC 2, the local regulator.
Each client gets exactly its program — on the tenant you already run.
ISO 27001 · SOC 2 · HIPAA · GDPR · PCI DSS 4.0.1 · NIST CSF 2.0 · DORA · NIS 2 · ISO 42001 · CIS v8 · CCPA · DPF · NBU 143 · All tenants × frameworks on one screen · Fix once — counted in every framework
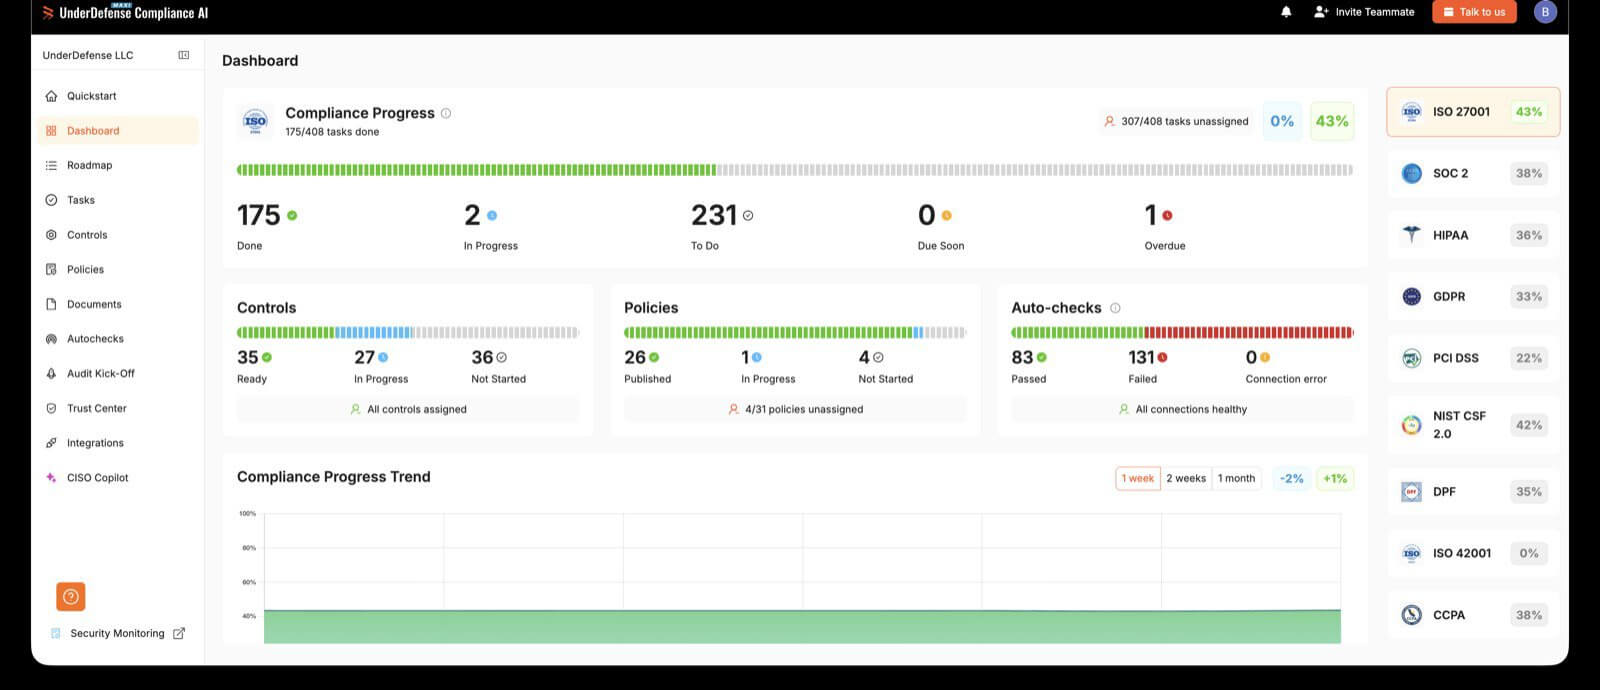
Evidence that collects itself
Evidence is gathered by hand right before the audit — and it's outdated the day after.
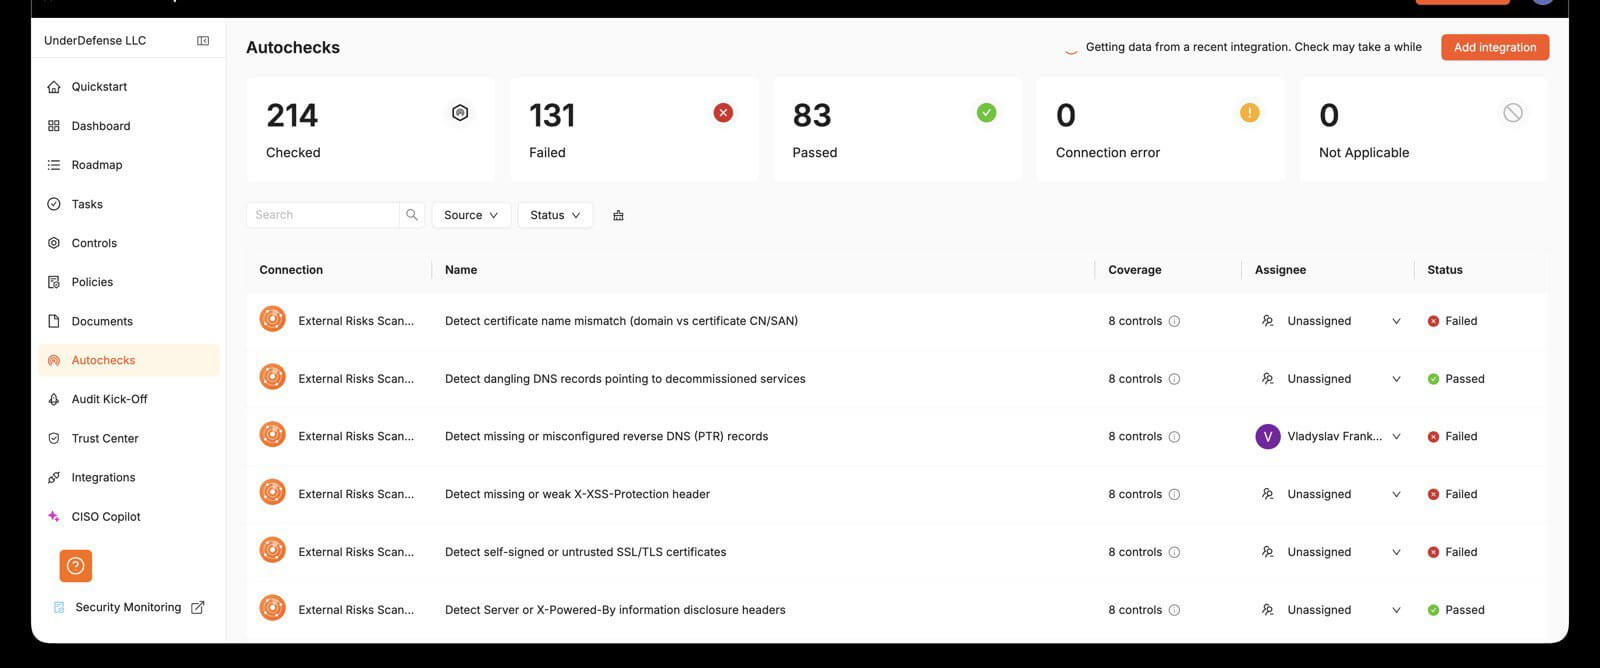
The right access for every client's team — in a minute
Client staff, auditors and your own analysts need different access — shared logins are an audit finding waiting to happen.
Invite from the tenant card with a role per product: AI SOC, Compliance AI, CISO Copilot.
Access is set during onboarding — every permission on one screen.
Active / pending at a glance · Resend or remove in one click · Auditor access scoped to one client
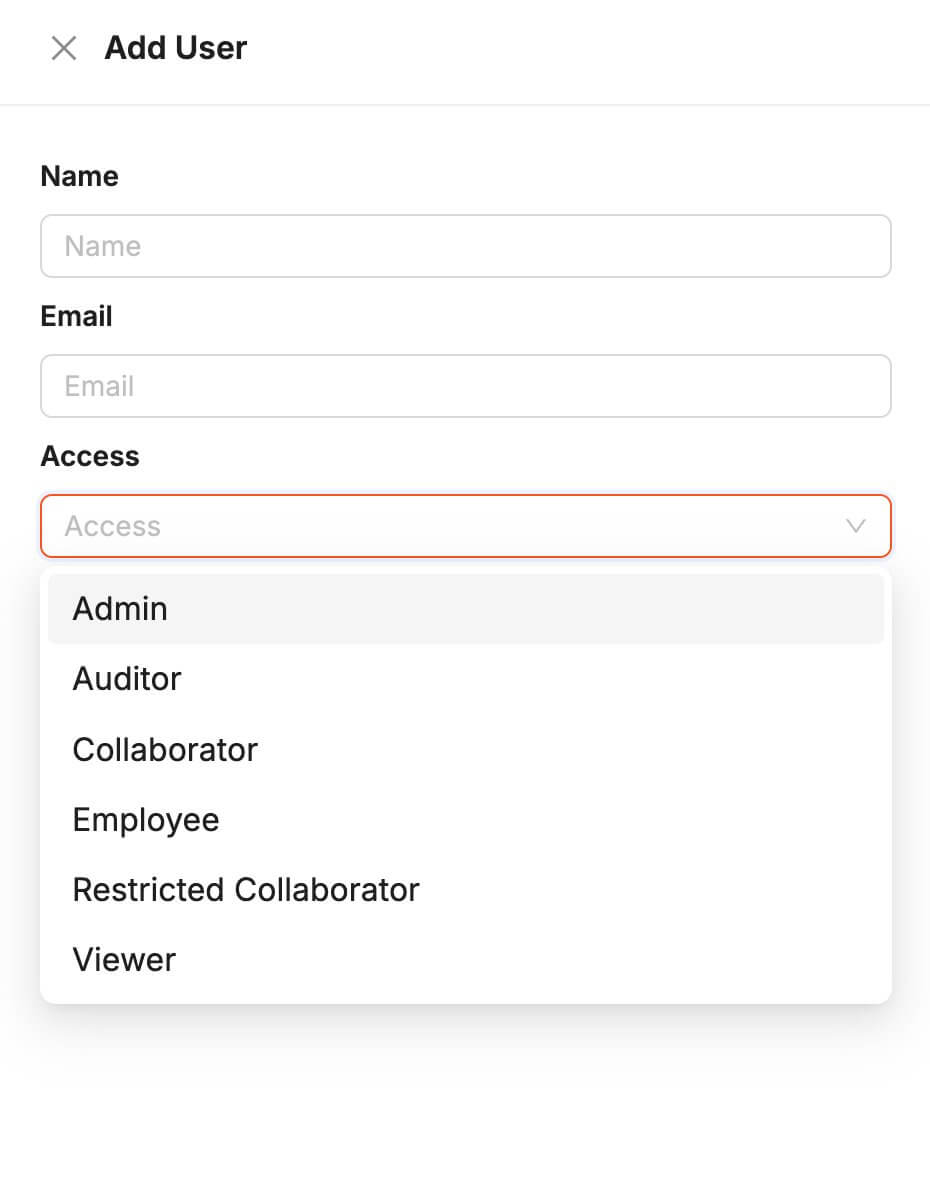
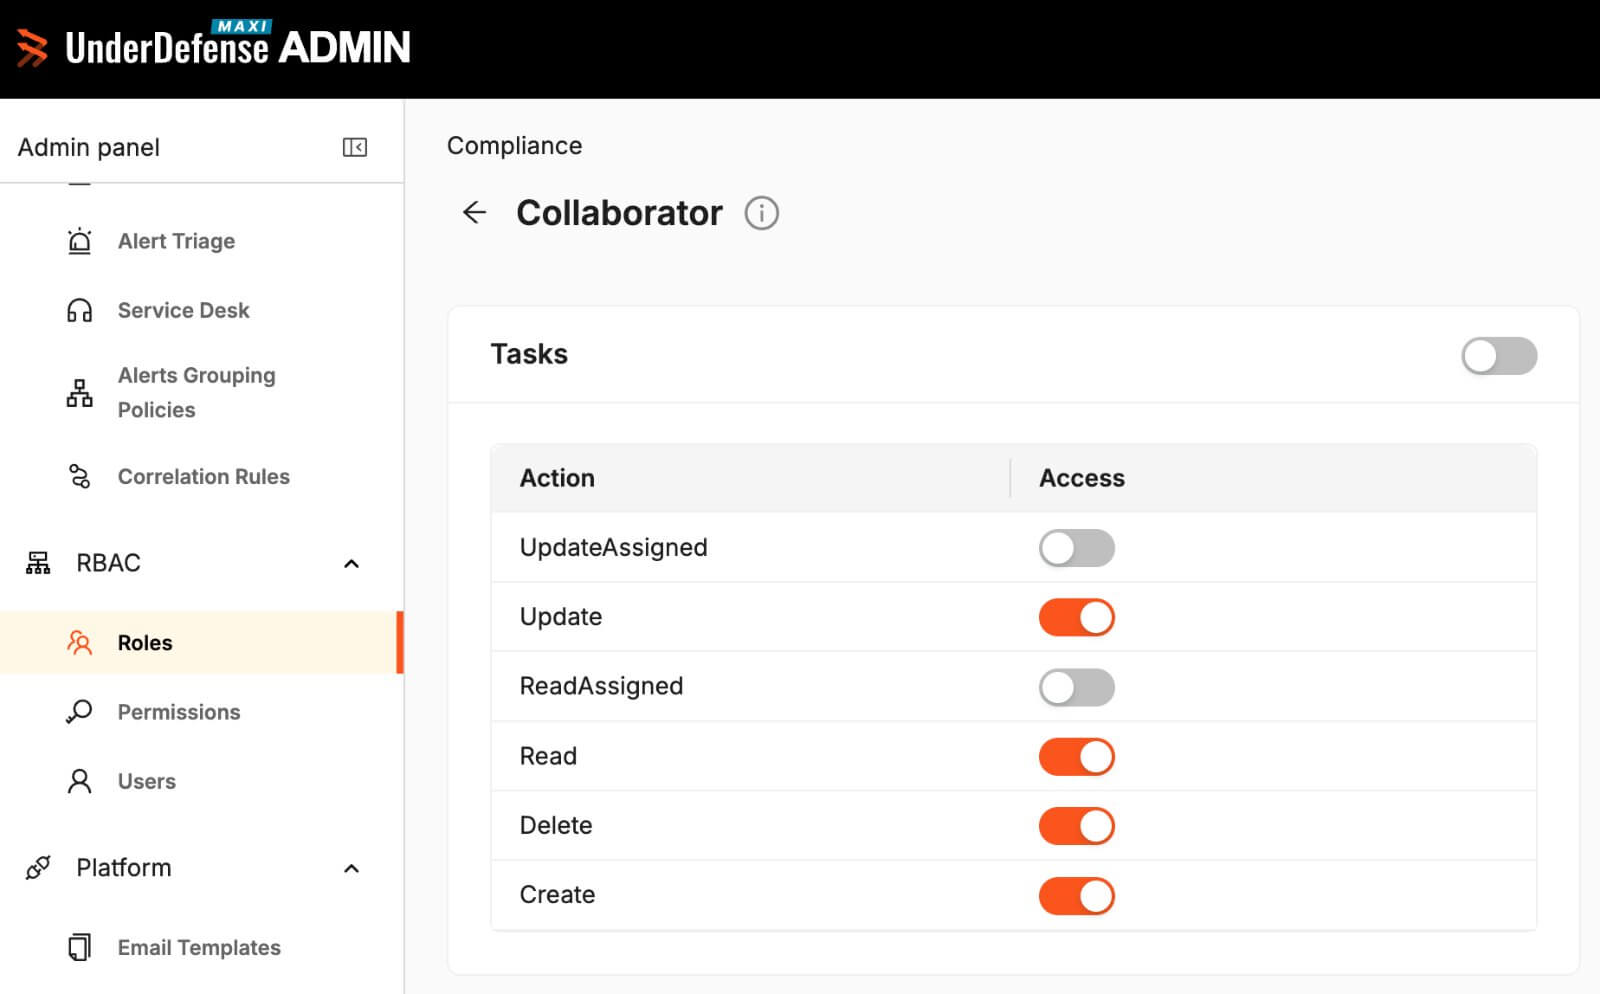
Audits without the scramble — and your own NIS 2 covered
Every audit means questionnaires, PDFs and weeks of back-and-forth with the client.
Build it, stitch it — or run it on MAXI
You are not doing this alone — we have your back
One named contact from kickoff to renewal
Pilot plan agreed up front
Integrations, detections and playbooks tuned with your team
The engineers who run our own SOC on MAXI
Tier 3 and incident response when a case outgrows your bench
Backup when you need it — you stay the face of the service
Optional: the analysts who run UnderDefense’s 24/7 SOC on MAXI work behind your service — per shift, per tier or per incident. Your client only ever talks to you.
Night shift
Offload night shifts or alert triage — the hardest seats to staff.
Tier gaps
Fill Tier 1, Tier 2 or Tier 3 gaps without hiring.
Incident response
An IR retainer with remote forensics when a case outgrows your bench.
Detection engineering
Rule tuning, threat hunting and a library of 1,000+ correlation rules.
Manage security for your clients in a new way
UnderDefense Incident Response Platform helps MSPs to manage ensure 24×7 breach protection through active monitoring, detection, and respond to cyber attacks from a single console across all your clients
24×7 Breach detection and Incident Response
Our 24×7 SOC-as-a-Service ensures security is monitored around the clock by expert team of professionals.
Protect Your Organization
UnderDefense’s 24×7 security teams work around the clock to monitor, detect, and respond to cyber attacks before they have the chance to impact your business.
Tools your clients already have
We support industry-leading security solutions which your clients have or you sold them. Core platforms like: Sentinel One, CrowdStrike, Fortinet, Sophos, TrendMicro
Managed Risk & Compliance
You will get an automated Compliance monitoring, documentation and analytics to help your client meet standards like PCI, HIPAA, ISO27001, SOC2
Security that makes sense
UnderDefense’s 24×7 security teams work around the clock to monitor, detect, and respond to cyberattacks before they have the chance to impact your business.
Product Branding
- Incorporate MSP brand with service offerings
MSP Service Reports
- Customizable reports to illustrate client endpoint security posture & actions taken by MSP to respond to threats
Multi-Tenant Support
- Manage multiple clients from one console with multiple dashboards
Bundled Functionality
- Add on 24×7 SOC, SIEM, MDR, EDR, vulnerability, patch, compliance, as-a-Service
- Reduced total cost of ownership
Cloud Security
- Host your client tenant in your region in Amazon, Google or Azure and other cloud tech
MSP Service Licensing/Price
- Simple Monthly subscription
- Endpoint based pricing
- Low cost per asset
Small, Medium, Large scale enterprises are at continuous risk
MSPs can help protect the end customers by adding (white label) UnderDefense 24×7 security-as-a-service offerings to their portfolio.
- Over 2,000 new attacks are being launched every day that exploits a weakness in software components
- 43% of cyber-attacks target small businesses.
- 60% of small businesses that are victims of a cyber-attack go out of business within six months.
- There was a 424% increase in new small business cyber breaches last year
- 40-60 new vulnerabilities are discovered every day, many are critical
- Many companies take six months or longer to discover vulnerabilities, and several more months to mitigate risks
Launch your AI SOC service on MAXI
A named partner contact, a pilot plan agreed up front, and the engineers who run our own SOC on MAXI.