




TL;DR
- A SOC team is the group that monitors, investigates, and responds to threats for a security operations center.
- Most SOC teams run in tiers: Tier 1 triage, Tier 2 incident response, and Tier 3 threat hunting.
- Staffing one seat 24/7 takes more than four full-time analysts, before leave, training, and turnover.
- SIEM, EDR, SOAR, and threat intelligence form the core toolset, and AI agents now handle much of Tier 1 triage.
Table of contents
- What Is a SOC Team?
- Why Businesses Need a SOC Team: 5 Key Benefits
- SOC Team Functions: What a Security Operations Center Does
- Key SOC Team Roles and Responsibilities
- SOC Team Structure: Getting It Right
- Core Tools Every SOC Relies On
- Emerging Trends: How AI Is Changing the SOC Team
- How UnderDefense Supports an In-House SOC Team
- How to Build a SOC Team: Best Practices
- Conclusion
- Frequently Asked Questions
You have a SIEM, an EDR, and alerts arriving around the clock, and the question on your desk is whether to build a SOC team of your own. Getting the SOC team structure, roles, and responsibilities right decides whether an alert at 2 a.m. reaches someone who can act on it or waits until morning.
This guide covers what a SOC team is, the functions it owns, the roles from SOC analyst to SOC engineer, how to structure the team, the core tools it runs, and how AI is changing the work. It closes with the best practices that keep an in-house team effective.
What Is a SOC Team?
A SOC team is the group of security professionals who monitor, investigate, and respond to cyber threats for an organization, often 24/7. SOC stands for security operations center. The SOC team is the people; the security operations center is those people plus the processes and technology they work with.
Think of a security operations center as your digital command center, and more than a room full of screens. It is where experts keep watch around the clock, hunting down cyber threats before they become disasters. The SOC can sit in-house, in the cloud, with an outside provider, or in a mix of these, and the team can be your own staff, a partner’s, or both.
Why Businesses Need a SOC Team: 5 Key Benefits
A SOC team gives every security event an owner, from the first alert to the closed incident. Here are the top reasons organizations build a security operations center:
- Threats are watched 24/7, because attackers keep no office hours and neither does the SOC.
- Incidents are detected and contained faster, which limits the damage each one does.
- Threat hunters look for attackers that the tools have missed, before an alert ever fires.
- Monitoring and incident records help you meet security requirements and avoid fines.
- The business keeps running during an incident, because someone is already responding.
Each of these benefits depends on the functions and roles below, so the next sections show what the team actually does.
SOC Team Functions: What a Security Operations Center Does
A well-functioning SOC team acts as the organization’s cybersecurity backbone. By executing its core functions of monitoring, analysis, detection, response, and remediation, it protects critical systems and data around the clock. A strong SOC team is an investment in the organization’s resilience: it keeps the business running and limits the impact of security incidents.
Day to day, SOC security work covers five areas:
- Threat monitoring keeps constant watch for suspicious activity, to stop attacks before they spread.
- Incident response handles breaches in real time to minimize damage and downtime.
- Vulnerability management spots weak points and gets them patched before attackers can exploit them.
- Log analysis sifts through large volumes of data to find patterns that reveal threats.
- Compliance management keeps controls and evidence in line with the regulations your business faces.
The five areas group into three core functions. Prevention is the preemptive strike: gathering threat intelligence, managing vulnerabilities, and training staff to spot phishing. Prevention costs far less than dealing with a full-blown attack.
Real-time monitoring and detection is the 24/7 surveillance layer. The team keeps an eye on every security tool and log source, using a SIEM to catch suspicious activity before it spirals out of control.
Incident response and resolution is the emergency crew. When something gets through, the team investigates, contains the threat, recovers data, and updates the incident response plan for next time. The table shows what the SOC team does inside each function.
| Core function | What the SOC team does |
|---|---|
| Prevention | Gathers and analyzes intelligence on emerging threats |
| Prevention | Prioritizes vulnerabilities and drives patching or mitigation |
| Prevention | Runs security awareness training against phishing |
| Monitoring and detection | Watches firewall, IDS/IPS, and EDR alerts continuously |
| Monitoring and detection | Correlates logs and events in the SIEM |
| Incident response | Investigates suspected incidents to set scope and impact |
| Incident response | Isolates systems and shuts down compromised accounts |
| Incident response | Restores systems and data from backups |
| Incident response | Maintains the incident response plan (IRP) |
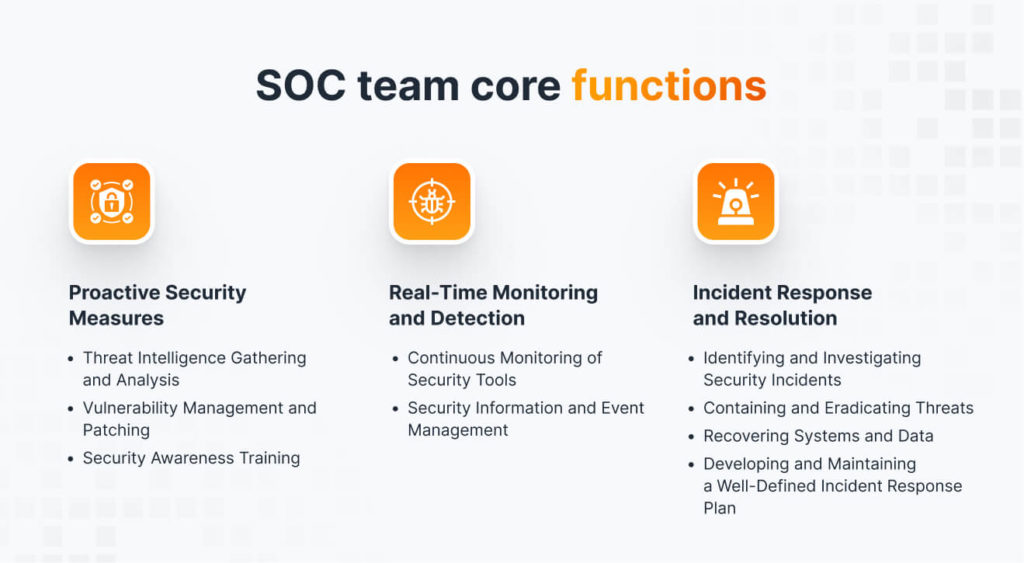
Together, the core functions are how a SOC team safeguards the organization’s data and keeps the business running when an attack lands. Whether you build them in-house or buy them comes down to cost, control, and coverage, which the outsourced vs. in-house SOC comparison weighs option by option.
Key SOC Team Roles and Responsibilities
Although the roles at any company may have different names, all organizations have similar responsibilities when it comes to cybersecurity. Here are the more common roles within a SOC team and the individual responsibilities associated with each role.
SOC Principal
The SOC Principal is the big-picture thinker, ensuring the team operates smoothly and aligns with the organization’s security goals. They set the strategy and oversee critical security initiatives, making sure nothing falls through the cracks.
SOC Manager / SOC Lead / SOC Director
Think of the SOC Manager as the team captain. They manage day-to-day operations, coordinate workflows, and ensure the team responds to threats quickly and effectively. They’re the glue that keeps everything (and everyone) together.
Security Engineer (SOC Engineer)
This is your tech wizard. Security engineers, often called SOC engineers, design, implement, and maintain the tools and systems the team relies on, from firewalls to SIEM platforms, and they write the automation playbooks. They keep the tech dependable so the analysts can focus on catching threats.
Tier 1 SOC Analyst
The first line of defense. Tier 1 SOC analysts monitor alerts, sift through logs, and flag potential issues. They’re the security guards of the digital world, keeping an eye on everything 24/7.
Tier 2 SOC Analyst
Tier 2 analysts are your investigators. They dive deeper into the alerts flagged by Tier 1, analyzing data to determine if it’s a real threat or just noise. When it’s serious, they escalate it up the chain.
Tier 3 SOC Analyst
The threat hunters of the team. Tier 3 analysts search for hidden threats before any alert fires and analyze advanced attack patterns. They’re the detectives, always looking for attackers lurking in the shadows.
Chief Information Security Officer (CISO)
The CISO is the security visionary, steering the organization’s overall cybersecurity strategy. They ensure the SOC aligns with business objectives, manages risks, and communicates with leadership about security needs and priorities.
Additional SOC Roles
Larger SOC teams add specialist roles once incident volume justifies them.
Compliance Auditor
This role ensures the SOC meets regulatory requirements and standards. They review policies, procedures, and reports to keep the organization compliant and audit-ready.
Threat Responder
The rapid reaction force. Threat Responders jump in when incidents occur, taking action to contain and neutralize threats before they cause damage.
Forensic Investigator
The digital crime solver. Forensic Investigators analyze breaches to understand how they happened, who’s responsible, and how to prevent a repeat. They’re the ones digging into the “who, what, and how” after an attack.
Each role is a piece of the puzzle, working together to protect your organization from cyber threats.
SOC Team Roles Comparison Table: Responsibilities at a Glance
Check out this table for a quick breakdown of each role, its starting headcount, and what it brings to the table (literally).
| Role | Starting headcount | Key responsibilities |
|---|---|---|
| SOC Principal | Lead role | Sets strategy, tests new detection ideas, improves procedures |
| SOC Manager | Lead role | Runs workflows, hires talent, builds roadmaps and reports |
| Security Engineer | 1+ people | Builds procedures, automation playbooks, and detection use cases |
| Tier 3: Threat Hunter | 1+ people | Hunts threats, investigates host and network events, mentors peers |
| Tier 2: Incident Responder | 3+ people | Verifies Tier 1 escalations, runs advanced SIEM analysis |
| Tier 1: Security Analyst | 5+ people | Investigates alerts, gathers evidence, documents each case |
The headcounts are starting points for a team that works in shifts. The next section shows why round-the-clock coverage pushes them higher.
SOC Team Structure: Getting It Right
A solid SOC team is the backbone of your cybersecurity defense, handling everything from 24/7 monitoring to incident response. The basics apply to everyone, but a lean security team has to focus on the must-have roles and make the most of its resources. Here is how to build a SOC team structure that works without overcomplicating things.
The SOC team structure outlined here is based on the extensive experience of UnderDefense in managing SOC operations.
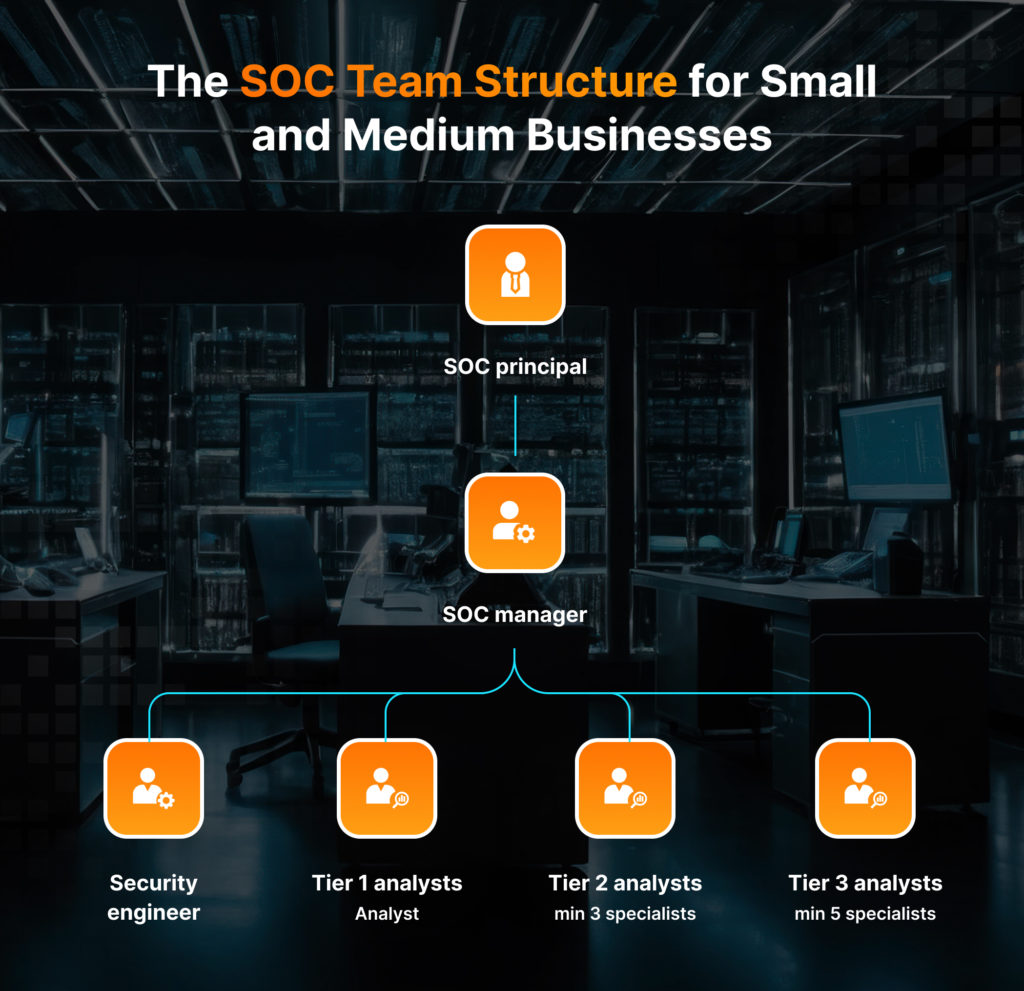
Plan headcount around shifts. A week has 168 hours and a full-time analyst works about 40 of them, so one seat staffed around the clock takes more than four people before vacation, sick leave, training, and turnover. That is why the Tier 1 line in the table starts at five, and why nights and weekends are the first gap most in-house SOC teams face.
Grow the structure by adding analysts to each tier first, then specialist roles such as forensic investigators. To put a price on each step, run your own numbers through the SOC cost calculator.
Core Tools Every SOC Relies On
A SOC team works only as fast as its tools let it see. Most security operations centers run on the same core stack, whatever the vendors behind it, and the table organizes the tools this guide mentions by what each one does for the team.
| Tool | What it does for the SOC team | Common examples |
|---|---|---|
| SIEM | Collects and correlates logs, raises detections | Splunk, Microsoft Sentinel, Elastic |
| EDR | Watches endpoints, isolates compromised hosts | CrowdStrike, SentinelOne, Microsoft Defender |
| SOAR | Automates repeatable response steps with playbooks | Splunk SOAR |
| Threat intelligence platform | Feeds indicators and attacker context into detections | Commercial and open-source threat feeds |
| IDS/IPS and firewalls | Flag and block suspicious network traffic | Network sensors, firewall intrusion prevention |
| Vulnerability scanner | Finds unpatched systems for remediation | Authenticated and external scans |
| Case management | Tracks incidents, ownership, and SLAs | Jira, ServiceNow |
Every tool in the table needs an owner, usually the SOC engineer, and every detection it raises needs a tier that will pick it up. When you fill an empty row, check integration first: a SIEM that cannot pull from your EDR leaves Tier 1 working two consoles, a trade-off the best SOC tools review weighs product by product.
Emerging Trends: How AI Is Changing the SOC Team
AI has moved from the attacker’s toolkit into the SOC itself. According to IBM’s 2026 Cost of a Data Breach Report, one in four malicious breaches was AI-enabled, and those breaches cost an average of $6 million against a global average of $4.99 million.
Defenders are answering in kind. IBM’s 2026 study found that organizations using AI and automation in security operations cut breach costs by almost $2 million on average. More than half of them reported using agents for threat detection and containment, while only 18% apply agents to vulnerability management.
That last gap matters, because the Verizon 2026 Data Breach Investigations Report found that exploitation of vulnerabilities is the most common initial access vector, at 31%. Four shifts are changing how SOC teams are built:
- AI agents take on Tier 1 and much of Tier 2 triage, and analysts review the verdicts.
- Detection rules are managed as code, so the SOC engineer versions, tests, and reviews them like software.
- Alerts from many consoles flow into one queue with one set of SLAs.
- Analysts confirm suspicious activity with the affected user over Slack or Microsoft Teams before escalating.
People stay in charge of the decisions: someone still has to approve isolating a production server at 3 a.m. The shift moves your hiring toward Tier 2 and Tier 3 skills and the engineers who tune the automation, the same direction the 2026 AI SOC trends point to.
How UnderDefense Supports an In-House SOC Team
Building a SOC team in-house usually stalls on one number: the four-plus people it takes to staff each seat around the clock. If your team covers business hours and the nights and weekends sit uncovered, the UnderDefense Agentic AI SOC can take the second seat. It works on top of the SIEM and EDR you already run: AI agents investigate every alert, and analysts on shift 24/7 make the decisions.
For your team, that means a critical alert at 2 a.m. gets an UnderDefense analyst within the 20-minute SLA response time for critical alerts, and your own analysts start the morning with the overnight incidents already investigated. They keep the work that needs knowledge of your business.
A licensed iGaming operator shows what that looks like. In 2019, its monitoring ran only during “business hours of 8 hours a day, 5 days a week,” and in December 2020 an intrusion on the unmonitored corporate segment “remained undetected for three days.” After the move to 24×7 coverage, the published case study reports “zero new internal headcount” and a recent production attack detected “10 minutes from first attacker move.”
The same case study reports that the platform processes “more than 4,500 alerts per month” and “filters 94.5% of those alerts upstream,” leaving “approximately 250 incidents per month” for response.
Book a 30-minute
Agentic AI SOC platform demo
- See AI agents triage and investigate a real alert on your stack
- Check which of the 250+ integrations your SIEM, EDR and cloud need
- Get a rollout plan with triage and containment SLAs for your team
How to Build a SOC Team: Best Practices
A SOC team is your cybersecurity A-team, always on guard and ready to tackle real-time threats. These are the best practices for building a strong SOC team.
Define Roles and Responsibilities
Think of it as casting for a heist movie: every role matters. Analysts, engineers, threat hunters, and even awareness trainers need clear duties so they don’t step on each other’s toes. Bonus tip: tier your analysts like a cake, with Tier 1 watching, Tier 2 investigating, and Tier 3 hunting the sneaky threats.
Recruit and Retain the Best
Your dream team won’t walk in off the street. Look for certified pros (CISSP, CEH, and similar) and keep them with growth opportunities and a healthy work culture. Analysts who spend their shifts on the incidents that matter stay longer than analysts who clear the same false positives every night.
Use the Right Tools
Equip your team with a SIEM, threat intelligence platforms, and automation (SOAR is your friend). If your analysts jump between five consoles to work one alert, a single operations layer saves them the context switch: the UnderDefense platform works on top of 250+ integrations, so the tools you already own feed one queue.
Train Like You’re in Cyber Boot Camp
Threats evolve, so your team should too. Workshops, courses, and regular practice drills keep everyone sharp and ready for real-world challenges. Track KPIs such as how fast your team detects and responds to threats, because the SOC metrics you choose become the team’s scorecard.
Communicate and Collaborate
A SOC works as a team sport, and lone wolves slow it down. Open communication, cross-training, and regular huddles keep everyone in sync and ready to go.
Simulate and Drill
Repetition is the mother of skill. Run regular simulations to test your team’s response skills, find weaknesses, and fine-tune your playbook. The more they practice, the better they’ll perform under fire.
By implementing the best practices outlined in this section, you can establish a strong foundation for effective security operations. From clearly defined roles and skilled personnel to the right security tools and a culture of continuous learning, each element decides how well your SOC works.
Conclusion
A good SOC team is your first line of defense against cyber threats. Whether you build in-house, bring in a partner, or combine the two, the key is having the right people watching your back at every hour of the week. Start with the tiers, staff the shifts you can, and decide early who covers the nights and weekends you cannot.
Staffing a SOC team for nights and weekends? See 24/7 triage in action
Frequently Asked Questions
What does a SOC operator do?
A SOC operator is the first line of defense in cybersecurity. They monitor systems, analyze alerts, and respond to potential threats. Their job involves identifying suspicious activities, escalating serious issues, and ensuring that your organization stays protected 24/7.
How big should a SOC team be?
The size of a SOC team depends on the organization’s size, its hours of coverage, and its alert volume. A lean team can start with 3 to 5 roles: analysts, an engineer, and a manager. Covering one seat 24/7 takes more than four people, and larger organizations run tiered teams with dozens of members, including threat hunters and forensic analysts.
What are the main SOC challenges?
SOC teams face a high volume of false positives, difficulty finding and keeping skilled analysts, and attackers who now operate at machine speed. Budget limits, 24/7 staffing, and integrating tools that do not share data add to the complexity.
What are security metrics for SOC teams?
The key metrics are mean time to detect (MTTD), how quickly threats are identified; mean time to respond (MTTR), how fast incidents are mitigated; false positive rate, how often alerts are wrong; and incident closure rate, how efficiently the team resolves incidents. Together they measure the effectiveness and efficiency of a SOC team.
What does SOC stand for in cybersecurity?
SOC stands for security operations center, the team and function that monitors, investigates, and responds to security threats. In everyday use, “SOC” can mean the people, the room they work in, or the provider that runs it. SOC 2 is a different thing: an audit report on a service organization’s controls.
What is the difference between a SOC analyst and a SOC engineer?
A SOC analyst works the alerts: triage at Tier 1, investigation and response at Tier 2, and threat hunting at Tier 3. A SOC engineer builds and maintains what the analysts use, including the SIEM, EDR integrations, detection rules, and automation playbooks. Smaller teams often combine the engineer role with a senior analyst.