





Incident Response Retainer
Minimize the damage and reduce your incident response time with UnderDefense Incident Response Retainer (IRR)
- Response Time
Get service level agreement (SLA) for onsite and remote consulting
- Budget
Agree on the number of prepaid hours and the hourly rate for additional hours
- Terms & Unused hours
Agree on the length of retainer and payment terms, such as if you need to pay up-front and what happens if you have unused prepaid hours
- Cyber insurance
Consider how your cyber insurance policy reimburses for incident response (IR) expenses and lower premiums by showing a proactive approach
Have UnderDefense IR experts on standby to help when you need it
Improve your readiness for data breach and define IR plan
Get expert response within hours, not days or week
Get ready and
Save at least
4 days when
Breach happens
Have a dedicated anti-malware team on-call
Ensure your first call focuses
on action
Eliminate paperwork-related response delays when every minute matters
Choice and Flexibility:
What Incident Response Retainer is right for you?
We provide tree options for Incident Response Retainer that are designed to suit different needs and budgets.
Basic
No upfront costs
- Establish terms and conditions for Incident Response (IR) services
- Define hourly rates for all incident response-related services and technologies
- Our experts available for you up to 12-hour SLA remotely
- Make no minimum financial commitment or pay no annual cost
- Pay only when Data Breach investigation starts
- Get support based on best effort and current availability
Standart
Incident response plan and SLA
- Establish terms and conditions for Incident Response (IR) services
- Define hourly rates for all incident response-related services and technologies
- Our experts available for you up to 4-hour SLA remotely
- Consultancy on how to improve your current incident readiness and response capabilities
- Access to Incident Response Readiness Service
- Our experts will help you compile Incident Response Plan tailored for your organization
Premium
Prepaid hours and SLA
- Establish terms and conditions for Incident Response (IR) services
- Our experts available for you up to 2-hour SLA remotely
- Our experts onsite for you by request
- Flexibility to repurpose unused hours on a variety of technical and strategic services
- Evaluate and improve your current incident readiness and response capabilities
- Our experts will help you compile Incident Response Plan tailored for your organization
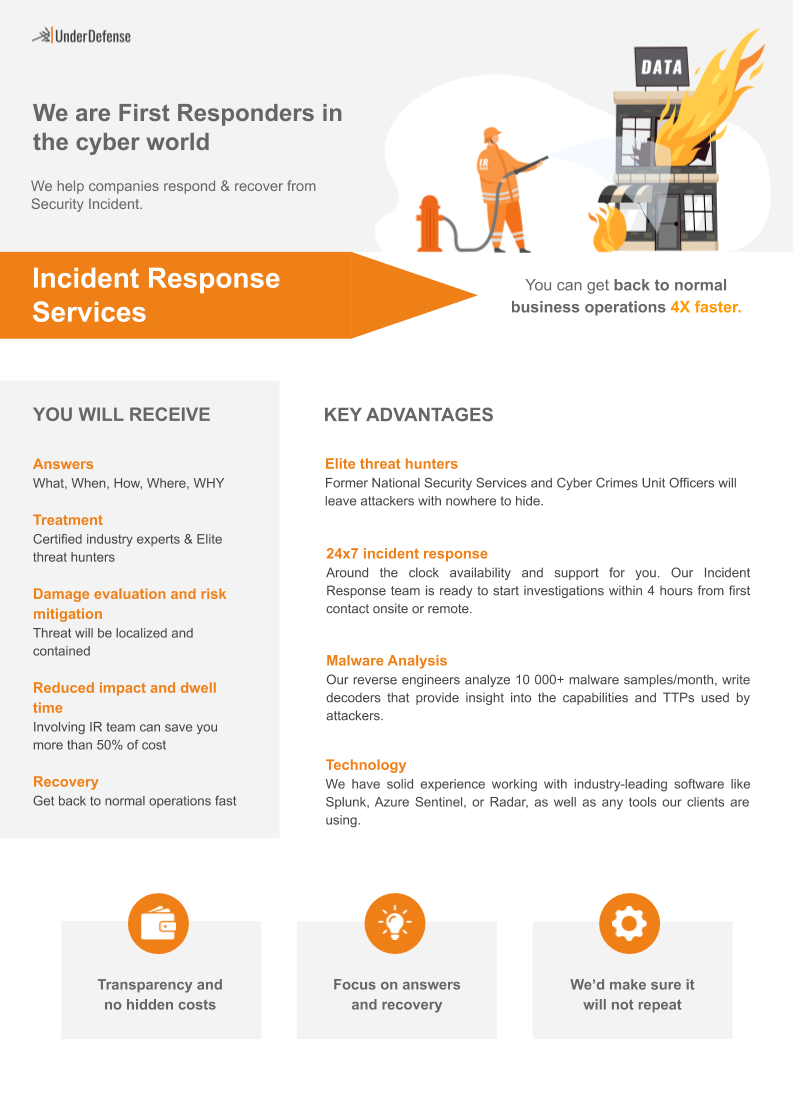
FAQ
What included in Initial Response?
- Triage security issue and preliminary analysis to scope the nature of an incident
- Provide initial assessment based on Threat Intelligence and SOC/IR experience
- Evaluate the damage: assess what part of your network was infected
What is covered under Service-level agreement?
- 24/7 incident response team availability 2, 4, or 12 hour SLA available
- Contact with UnderDefense incident responder who can immediately help with triaging the incident
- The case is accepted once UnderDefense and client deem that incident response services are needed
What included in Incident Response Readiness Service?
- Review of logging, monitoring and detection technologies you own
- Review of the current network and host architecture
- Ensure incident is identified quickly
- Collaborative planning for Incident Response Plan
- Recommendations for improvement
Expertise and Services
Security Monitoring
24x7x365 UD will watch your network & protect you from Malicious Actors and Advanced Persistent Threats
Compliance & Audit
Get compliant fast and easy. SOC2, ISO 27001, PCI DSS, GDPR we know them inside out
Penetration Testing
Find your weaknesses before hackers do. Regular health check is a must for a successful company
Related resources
9 Best CSPM Tools 2026: What Posture Scores Miss
TL;DR Cloud misconfigurations caused 27% of breaches on AI models and applications in IBM's July 2026 study. Three of these nine CSPM tools publish self-serve prices: Defender CSPM, AWS Security Hub CSPM and Prowler Cloud. Weak-password and permission findings took...
10 Best Agentic AI SOC Platforms for 2026
Compare 8 best agentic SOC platforms for 2026. Pricing, integrations, compliance, and POC frameworks scored across 500+ MDR deployments. Evaluate now.
Red Team Assessment: Scope, Process, Deliverables
TL;DR Red teaming measures whether your people, processes and tools catch a realistic attacker. In CISA's 2026 test of two organizations, the team took both domains, and only one SOC noticed. Scope starts with objectives, such as a customer database or domain...
Ready to get started?
We are here for you, ready to prepare you to respond to data breach or answer questions about how you can improve your incident readiness and compliance today