




New capability gives security leaders a second-by-second record of every incident, from first alert to final verdict, with automatic audit evidence and built-in AI governance reporting
Jacksonville, FL, September 15, 2026. UnderDefense, a cybersecurity company delivering Agentic AI SOC and Compliance AI to enterprise clients across the US and EU, today announced the launch of Incidents Timeline 2.0. The new capability captures every automated action, AI agent decision, and analyst determination in real time, giving security teams a complete chronological record of every incident that runs through the platform.
Security teams have long faced the same challenge after an incident closes: reconstructing a response timeline from disconnected systems to answer questions from auditors, cyber insurers, or the board. Incidents Timeline 2.0 removes that step. Every action is captured automatically as the incident runs.
“You can only trust autonomous security tools when you can see how they think,” said Nazar Tymoshyk, Founder and CEO of UnderDefense. “Every AI reasoning step, every analyst decision is now captured as it happens. When a CISO needs to answer for the quality and speed of a response, the proof is already there.”
What Incidents Timeline 2.0 Delivers
Every incident now has a complete log from first alert to final verdict, recorded automatically as it runs, with no manual reconstruction. Every run of the AISOC Tier 1 Agent shows its individual steps: inputs analyzed, reasoning path, execution time, and conclusion. Security leaders can see not just what the AI decided, but how it reasoned. All SIEM queries, playbook executions, and enrichment steps are visible, including checks that were skipped and why.
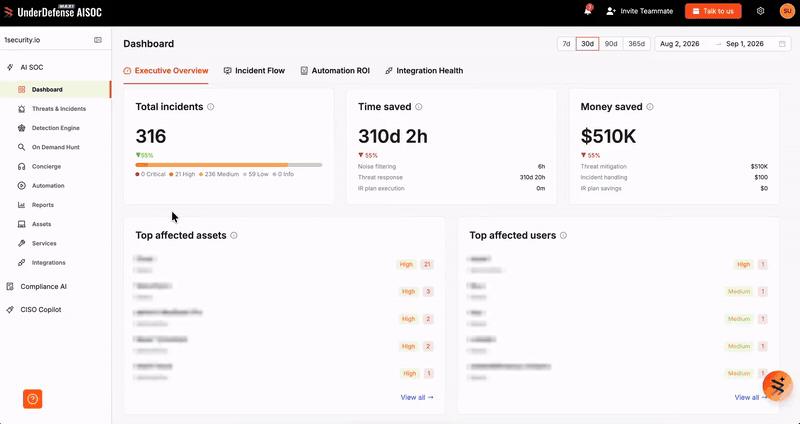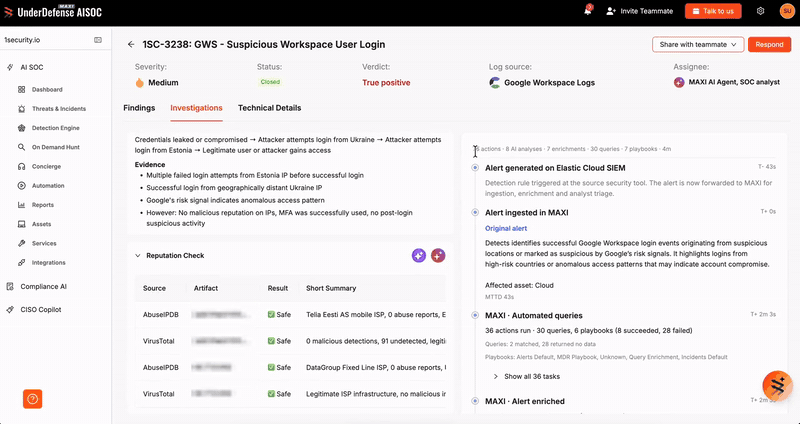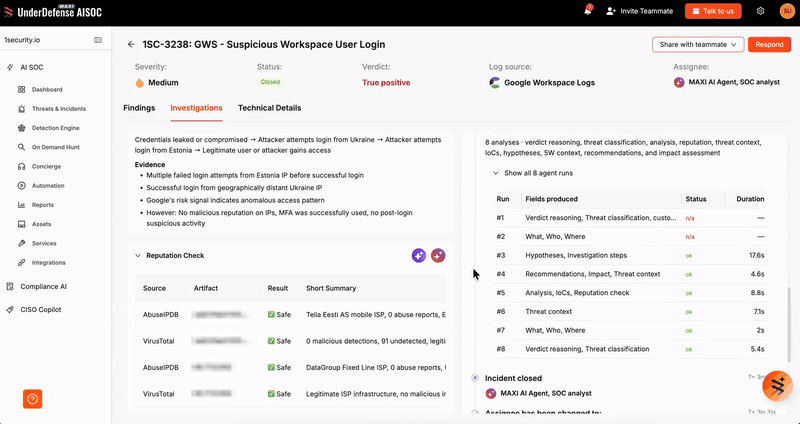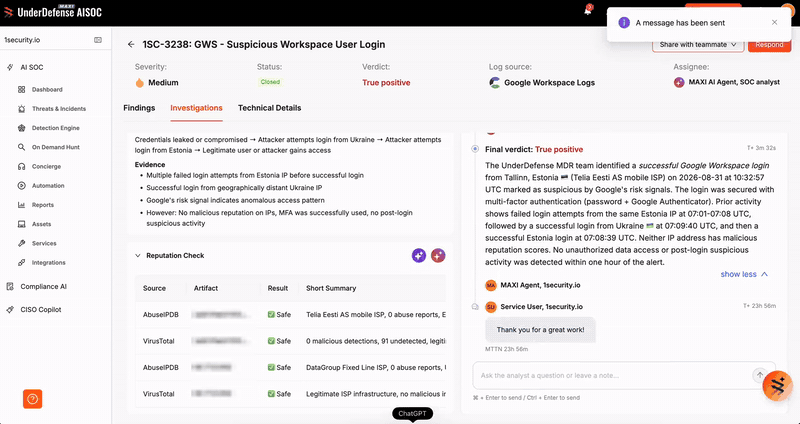
Mean Time to Detect (MTTD) and Mean Time to Triage (MTTT) are calculated and displayed directly on each incident, with the calculation method shown. Every action is timestamped and exportable for internal reviews, auditors, cyber insurers, or board presentations, without preparation.
Analyst verdicts include reasoning, risk levels, and recommended next steps. Security teams can ask follow-up questions directly inside the incident without switching tools.
Common Scenario: The Morning After an Incident, A Call from the CTO
It is a situation most security teams have been in. Tuesday, 8:40 AM. An incident triggered overnight. An hour later, the CISO receives a call from the CTO. The question is always the same: “Did we handle this properly, and were we fast enough?” With Incidents Timeline 2.0, the CISO opens the incident and sees the complete overnight story, tracked second by second: the exact moment the alert fired, when the Concierge ticket opened, what the AI agent verified, when human analysts joined, and why they reached their verdict. In less than two minutes, the CISO has the answer and the proof to show for it.
Incidents Timeline 2.0 is available for all UnderDefense platform clients at app.underdefense.com/aisoc.
To see it in action: underdefense.com/book-a-demo
About UnderDefense
UnderDefense is a global cybersecurity company operating across the United States, Europe, and international markets.
Its Agentic AI SOC is a vendor-agnostic security operations platform that integrates with clients’ existing SIEM, EDR, cloud, identity, and security infrastructure. The platform combines autonomous AI-driven triage with experienced human analysts who retain decision authority over confirmed incidents and response actions.
UnderDefense serves organizations across multiple industries, including financial services, healthcare, technology, telecommunications, and the public sector.
UnderDefense
111 John Street, Suite 420
New York, NY 10038
United States
Tel: +1 (929) 999-5101