Managed SIEM Services: Deployed, Tuned, and Monitored 24/7

We turn alert noise into insight with our managed SIEM solution powered by UnderDefense Agentic AI SOC. It eliminates false positives, tunes your SIEM for maximum detection accuracy, and delivers real-time threat monitoring across your entire environment.
ManagedDetectionandResponse(MDR) MomentumLeader Leader SystemSecurity BestSupport QualityOfSupport Frame 1413068553 image 123412340 (1) scawards
managed siem
Market leaders trust us
yayPay
betssongroup
RemotePass
helpware
enersponse
enersponse
enersponse
enersponse
Bill_Melisa_Gates_Foundation
matrix42
matrix42
Volkswagen
accedian
CohnReznick
avenga
invicti
onit
Blackberry
shelf
materialise
rydoo
skelar
yayPay
betssongroup
RemotePass
helpware
enersponse
matrix42
Volkswagen
accedian
CohnReznick
avenga
invicti
shelf
materialise
rydoo
skelar

Compare SIEM-as-a-Service by UnderDefense to Traditional SIEM

Traditional SIEM approach
logo white
SIEM-as-a-Service
Getting up and running
6 months
On average, it takes six months* for companies to select, purchase, deploy and fine-tune a security information and event management solution to start receiving high-value alerts.
20 minutes
We make your new SIEM up and running in 20 minutes, fully ready for log ingestion in your geo location. 
Budgeting & licensing
Unpredictable budgeting
Unpredictable budgeting and skyrocketing expenses, while deployment engineers ingest all your data sources and even don’t realize a proliferation of cloud app data, due to expensive, legacy server-based architecture.
Pay-as-you-go model
We offer transparent pricing with a pay-as-you-go model. We take care of all the questions related to licensing and budget fitting. By partnering with leading security providers, we tackle all the issues related to purchase on your behalf ensuring the fastest deployment and time-to-value.
Log aggregation
Risky log juggling
Imposed risks that you take when picking and choosing which logs should be ingested to keep cost and performance at acceptable levels.
Only valuable, relevant data
We help you with ingestion, selection, and standardization of only valuable security-relevant data from your security stack within a single Security-as-a-Service platform.
Use cases
Detections not matching use cases
Default detections that are often outdated and don't work as expected.
 Personalized, relevant detections
We give the freedom of choice to select tailored detections from our library of 1000+ correlation rules, aligned with your use cases.
Threat hunting
No time for threat hunting
No time to hunt for threats while the team is buried in alerts and scattered security data.
 Proactive security measures
We proactively hunt for access and traffic anomalies, correlating hosts, risks, vulnerabilities, and threats in real-time.
Incident response
Time-consuming, manual processes
Manually correlate and investigate alerts, wait hours or even days for large queries to complete, impeding critical incident investigation and response activities.
Clear answers in minutes
We provide you with all the answers in minutes, not hours. Actionable context explaining threat severity and the where, what, and when of an attack is available to you promptly, allowing you to react to threats immediately.
Operational cost
Massive capital investments
Massive capital investments (CAPEX) into hardware, software, and engineers are required. You have to deal with burdensome software administration, DevOps, and resource planning instead of focusing time and energy on your security.
OPEX+SIEM-as-a-Service model
We ensure the OPEX model and SIEM as a Service approach with zero overhead, allowing you to focus effort on your business rather than managing complex DevOps or security information and event management teams.
Correlation rules
Only default correlation rules
The inability of teams to write new effective correlation rules increases the number of alerts and false positives, leading to alert noise, missed critical threats, overloaded analysts, and constant employee attrition. All that leads to breaches and lack of answers.
1000+ new detections
We select and deploy correlation rules depending on your use cases, using our growing database of 1000+ new detections. By doing so, we help you easily find even a needle in a haystack, reduce false positives, effectively deal with threats, and optimize the workload of your security team.
Situation awareness
Postponed
Reliance on standard reports leads to the lack of actual situation awareness and poor security posture management.
Real-time situation awareness
We offer full real-time situation awareness including risky employees, assets, threats, and vulnerabilities with clear monthly reports and dedicated account managers. All you need to meet compliance requirements and gain confidence.
20 min

SLA response time to critical threats

1000+

Unique SIEM correlation rules to cover all your use cases and find a needle in a haystack

20 min

To make your SIEM up and running in our cloud, ready for log ingestion in your region

96%

MITRE ATT&CK framework coverage to spot intrusion at any step of the kill chain

Get your managed SIEM quote

How managed SIEM works

From the first log source to the monthly report, here's what our team runs for you at each step of managed SIEM services.

Data ingestion
We connect your log sources, from EDR and firewalls to cloud and identity logs, and filter out data with no security value. A SIEM in our cloud is ready for log ingestion in your region within 20 minutes.
Tuning and correlation rules
We select detections for your use cases from our library of 1000+ correlation rules, tune them to your environment, and switch off the ones that only create noise.
24/7 monitoring
Our SOC analysts watch your alerts around the clock, triage them, and escalate critical threats within a 20-minute SLA, with the context your team needs to act.
Reporting and response
You get monthly reports and log evidence for SOC 2, ISO 27001, and PCI DSS audits. When an incident needs hands-on work, our incident response team can join through an IR retainer.

How UnderDefense solves your SIEM challenges

How UnderDefense solves your

SIEM

challenges

  • Tuning overload. Most teams struggle to configure detection rules and log sources. We manage SIEM tuning and alert logic, so it works 24/7.
  • Expertise gaps. No internal SIEM expertise or time? Our SIEM-as-a-Service team covers ops, scaling, and SIEM consulting.
  • Deployment delays. SIEM onboarding is slow and painful. We streamline co-managed SIEM deployment and go live faster.
  • Console chaos. Switching tools kills visibility. We connect SIEM with MDR & IR workflows for full context.
  • Alert noise. Too many false positives eat your team's time. We fine-tune rules to cut noise and put real threats first.
  • No threat context. Can’t connect logs to real incidents? We unify telemetry so every alert comes with the context to act on it.
  • Compliance pressure. SOC 2, HIPAA, ISO 27001, and GDPR add up to too much to manage. Our managed SIEM cloud services automate reports and simplify audits.
  • Staff turnover. Security churn breaks SIEM performance. Our always-on SOC fills the talent gap with no learning curve.

Benefits of managed SIEM services
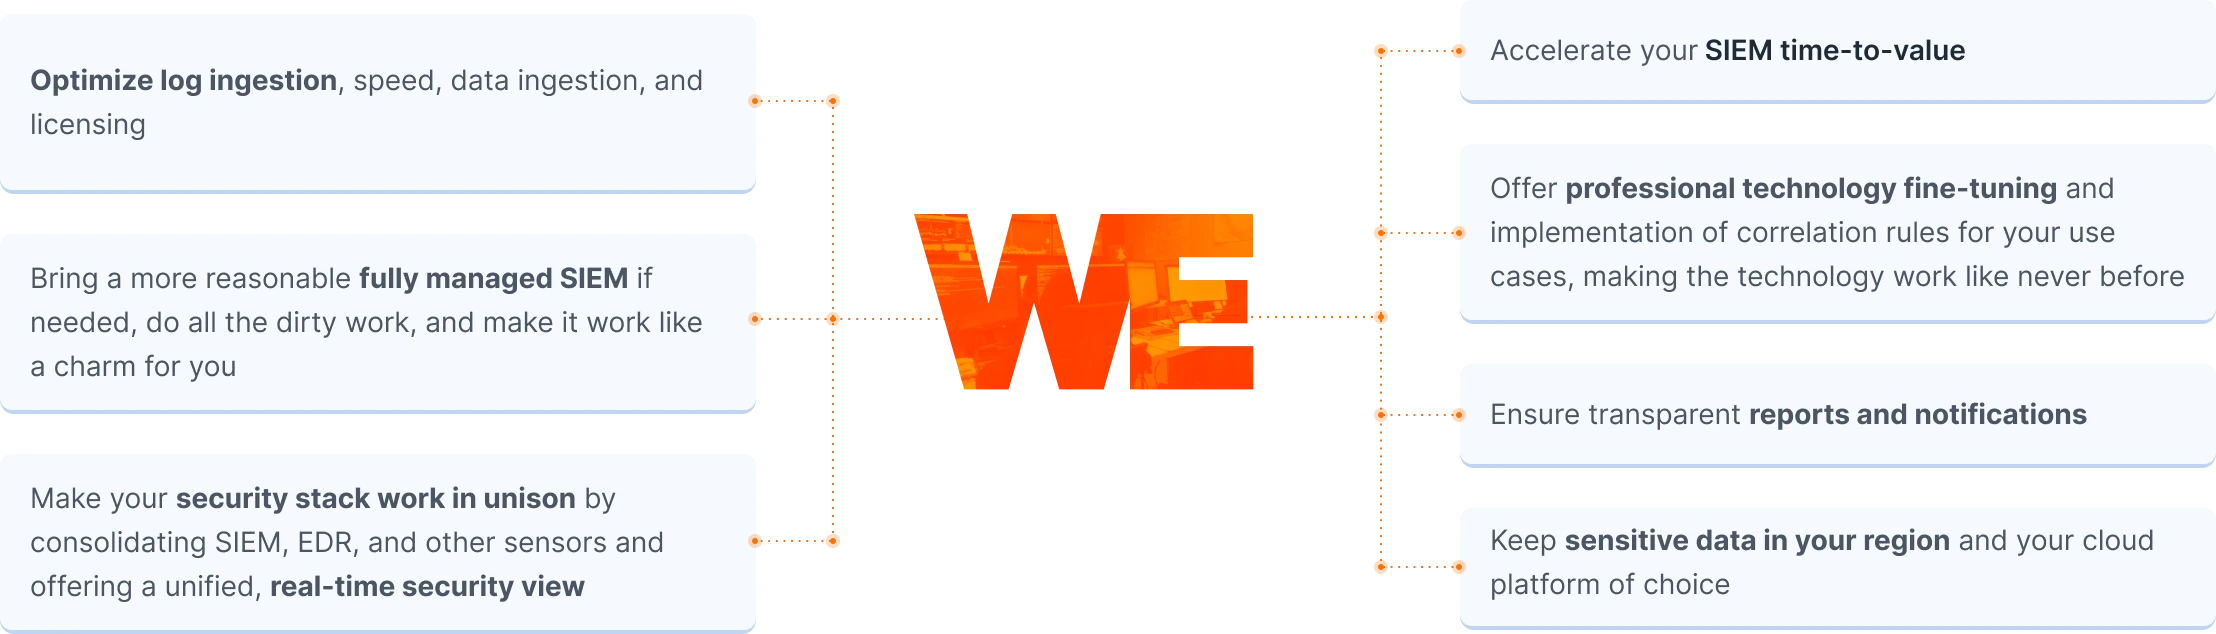
Go beyond basic SIEM: Real outcomes with managed SIEM services

Improve threat detection and response
Enhance detection and response across hybrid environments with SIEM as a Service. Triage faster, cut through alert noise, and detect real threats using all your log data.
Enable faster alert triage and enrichment across your on-prem, hybrid, and cloud environments and tools with SIEM managed services. Use all your data to identify and address current and future risks in no time.
Meet and maintain compliance
Use managed SIEM solutions to centralize log management, streamline reporting, and meet SOC 2, ISO 27001, and GDPR without the manual burden.
Consolidate your security tools and enhance event log management to react to threats immediately. Ensure proactive risk detection and mitigation to not only become but stay compliant and avoid fines.
Lessen the burden on your in-house IT team
Let your internal team focus on what matters. We handle rule tuning, alert triage, and correlation with co-managed SIEM services tailored to your tech stack.
Leave alert triage to our SECaaS platform and security automation playbooks. Let your in-house team focus only on those requiring genuine attention. Cut alert noise and make proactive security a part of your strategy.
Win larger deals and strategic partnerships
Build trust with customers, auditors, and partners by proving your SIEM platform supports supply chain protection, threat detection, and ISMS compliance.
Leverage managed SIEM solutions to unlock your business expansion to new markets. Prove to your most profitable customers and partners that you are ready to prevent supply chain attacks and meet the ISMS requirements.

We provide SIEM as a Service for the following world-class technologies

See All Integrations

Visibility, context, prioritization at your speed and scale

Product-agnostic
approach
Don't be confined to vendor-forced security tools. Get a solution that meets your expectations and budgets, and make the most of it with UnderDefense SIEM as a service. Use our skills and expertise with most leading solutions to maximize your security investments.
Professional SIEM
fine-tuning
Expand your threat detection capabilities with 1000+ new correlation rules included in managed SIEM service by UnderDefense. All rules are selected, implemented, and regularly updated by our SOC experts to improve your threat visibility and save you time.
Quick and cost-effective service deployment
A SIEM in our cloud is ready for log ingestion in your region within 20 minutes, and we connect your log sources and tune detections from there. Improve data accuracy, cut alert noise, and keep up with new attack techniques.

What to look for in a managed SIEM provider

Before you sign, ask every vendor questions that show how the service runs day to day. Four to start with:

MITRE ATT&CK coverage you can verify
What share of MITRE ATT&CK techniques do your detections cover, and can you show the heatmap?
Your stack, kept
Do you work with the SIEM and EDR we already run, or do we have to replace them?
Documented response times
What are your documented mean time to triage and mean time to respond for critical incidents?
Data ownership at exit
Who owns our log data, and what happens to it and to our detection rules when the contract ends?
See all 20 questions

Our customers say it best

Named as a high Perfomer Incident Response System Security by G2 Crowd
4.8
“Not having to worry about ransomware, alert overload and reporting. Getting a clear view of my security posture, where the threats are coming from and how they are handled. They literally took care of all our problems.”
Read Reviews
Managed Detection and Response (MDR)
4.9
“Holistic approach, exceeding requirements with added value and cost savings; smooth transition to Crowdstrike EDR and Elastic SIEM implementation; flexibility with a 120-hour incident response retainer, surpassing the standard 40 hours.”
Read Reviews
Named as a Top Cybersecurity Company 2025 by Clutch
5.0
“UnderDefense impressed us with their ability to tailor their services to our unique needs and challenges. They didn't simply provide a one-size-fits-all solution, but instead took the time to understand our specific environment and requirements.”
Read Reviews

Frequently asked questions

What is SIEM as a managed service?

Managed SIEM-as-a-service is a more cost-effective alternative to in-house, on-prem installation, setup, and maintenance of a security information and event management solution. In this case, an organization delegates software deployment, fine-tuning, and ongoing support to a third-party provider.

By engaging SIEM managed service providers, organizations gain access to experienced personnel, save expensive internal resources, accelerate time-to-value, and avoid unnecessary staff training and professional development costs.

What does co managed SIEM mean?

A co-managed SIEM solution means a collaboration between an organization and a managed provider. Such an approach combines and augments the strengths of both parties by allowing them to share the responsibility, experience, and knowledge. The client and the managed cloud SIEM solution provider can create a scalable and effective solution that maximizes security risk monitoring, threat detection, and response capabilities amid the ever-evolving threat landscape.

What do UnderDefense managed SIEM services include?

UnderDefense offers a full range of security services and cooperation models that easily adapt to your needs, goals, and budgets. We can cover the entire SIEM-as-a-service process, from software selection, installation, setup, and maintenance to 24/7 remote SOC team and custom reporting. Finally, we are a product-agnostic SIEM as-a-service provider, meaning that you can choose security tech, and we’ll make it work better for your business.

What's the difference between managed SIEM and MDR?

Managed SIEM services run your SIEM platform: log ingestion, parsing, correlation rules, tuning, reporting, and the log retention auditors ask for. MDR focuses on finding and stopping active threats around the clock, usually starting from endpoint telemetry, and includes containment. Many teams need both: the SIEM gives visibility and an audit trail across every log source, and 24/7 detection and response acts on what it surfaces.

Why do I need SIEM if I already have antivirus or firewalls?

Antivirus and firewalls each see one part of your environment and block what they recognize. A SIEM collects logs from all of them, plus identity, cloud, and application logs, and correlates events across sources: a login from a new country, followed by a privilege change and a large data transfer, looks harmless in each tool alone. SIEM also keeps the audit trail that frameworks like PCI DSS require, which asks for at least 12 months of audit log history.

Do I need anything else to run managed or co-managed SIEM?

For SIEM-as-a-Service, no: we provide the sensors and log collectors, and the SIEM license is included. For co-managed SIEM, you keep your current SIEM license and we work inside your platform. In both cases your team gives us access to the log sources you want covered. If you also want endpoint protection or hands-on incident handling, managed EDR and an incident response retainer are available separately.

How much do managed SIEM services cost?

The cost depends on the model you choose (SIEM professional services, co-managed SIEM, or SIEM-as-a-Service with the SIEM tool included), the number of service hours, and the volume and number of your log sources. Current rates and what each model includes are on our managed SIEM pricing page. For an exact figure, contact us with your environment details.

What data do you access when providing managed SIEM services?

We take into account client’s requirements, compliance controls, and other business specifics. That’s why, as a managed SIEM monitoring services company, we leverage only telemetry and incident metadata. We don’t have access to PII and other sensitive data unless the client requests it.

Which SIEM platforms do your managed SIEM services support?

We're vendor-agnostic: we run managed SIEM services on Splunk, Microsoft Sentinel, IBM QRadar, Elastic, Sumo Logic, and LogRhythm, and we work with the security tools you already have. If you're choosing a SIEM from scratch, we help you pick one that fits your data volume, budget, and compliance needs.